

Cyber Security Researcher | Bug Bounty Hunter | Student | Acknowledged by Apple, Berkeley, Drexel, Nasa Etc @yeswehack
Dubai, United Arab Emirates
Joined October 2019
- Tweets265
- Following616
- Followers474
- Likes4.5K




Yayyyyy!!! 🎉🥳
Apple just rejected my application for the Offensive Security Researcher role. 🍎💀
Apparently, finding vulnerabilities in Apple products is easier than getting hired to find them. 😂
#Apple #OffensiveSecurity #BugBounty

2
122

Tr.ffn 🇦🇪 retweeted

For the second time in Google Chrome’s history, Google awarded a $250,000 bounty for a full-chain exploit… to @XBOW. Here’s the full story:
At an all-hands at the start of 2026 in Malta, I set the team a crazy challenge. A full-chain exploit of Chrome by the annual Black Hat cybersecurity conference in August.
I believed there were few better tests of whether @XBOW could move beyond web applications to desktop software, servers and devices.
Chrome is one of the most hardened pieces of software on the planet, used by more than half the world’s population.
A full-chain exploit lets an attacker take total control of a machine, where they can read every email, password and bank login the user types. You don’t need to download anything or click a phishing link. Visiting the wrong site is enough.
So @moyix, Andres Luksenberg, Baul Lee, and Willem Pinckaers took on the challenge along with a fifth teammate: OpenAI's GPT-5.6 Sol.
They built a chain they thought would win, but Google told us they already knew one of the bugs.
We were already in Las Vegas for Black Hat and DEF CON, and the team didn’t want to go home without the win.
So Brendan and the agents built a new exploit in just 6 days.
We submitted it to Google and waited.
The news came through that we'd done what should’ve been impossible. A full-chain bounty of $250,000, the first awarded under Google’s 2026 rules.
It took just 6 days and $40,000 of compute to construct an exploit that affects a billion users of Chrome on Windows. An intelligence-agency veteran told me his team used to spend 6 months on this kind of vulnerability.
My takeaway: the cost of finding truly critical vulnerabilities is collapsing, for attackers and defenders alike. Restricting powerful models is not the answer; GPT-5.6 Sol is already public.
But defenders have one advantage attackers never will: they can test their own code first.
Assume your software is exploitable. Whoever is hunting your bugs has the same building blocks we did.
This is cause for urgency but not panic.
XBOW is now developing an autonomous product for testing compiled software (desktop applications, servers, embedded devices), and partnering with the world’s top organizations to design that product.
If you’d like to be one of them, get in touch.
P.S. Restart Chrome whenever the Update button appears!

Thrilled to share that I've successfully completed my Digital Forensics & Incident Response (DFIR) from EC-Council Learning and received my Certificate of Achievement! Grateful for this learning journey and excited for what's next. learn.eccouncil.org/certific…

2
53
Tr.ffn 🇦🇪 retweeted

Telegram Desktop: one-click account takeover via IPC injection
beaksec.github.io/posts/tele…

ChatGPT is acting super weird right now. 🤔
Is it just me, or is everyone getting bizarre responses? 👇
Reply with:
🤖 = Yes, acting totally weird
✅ = Nope, working fine for me
🤯 = It gave me something completely unhinged
#ChatGPT #OpenAI #TechTwitter #AI #CyberSecurity

2
115

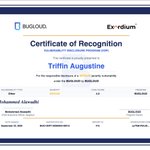
Happy to share that I received a Certificate of Recognition from BUGLOUD for responsibly disclosing a Medium severity vulnerability (CVSS 4.3) through their VDP.
Always great to see responsible security research recognized. 🔐
#CyberSecurity #BugBounty #VulnerabilityResearch

2
180
“AI found the bug. I found the bounty. Teamwork. 😂💸”
#BugBounty #BugHunting #CyberSecurity #EthicalHacking #InfoSec #HackerLife #SecurityResearch #Pentesting #AI #ChatGPT #ClaudeAI #CyberSecurityMemes #HackingMemes

9
503

Just got a reward for a vulnerability submitted on @yeswehack -- Double Free (CWE-415). yeswehack.com/hunters/trffns… #YesWeRHackers

1
23
771
100% Free Claude Fable 5, Opus 5 and Opus 4.8 etc
1. Open: agentrouter.org/register?aff…
2. Click Continue with GitHub.
3. Sign in with a GitHub account that was created 3–4 months ago or earlier.

1
2
243
Aww, you miss me? Then act like it.
A whole month of 'escalated to *Program' and zero follow-ups. Pay your researchers or stop crying in my inbox. 🥱💰
@HackenProof

6
774
Just completed the "Dojo #52 - StreamCore" challenge on @YesWeHack!
Level up with me! 🌟
dojo-yeswehack.com/challenge…
#YesWeHack #ChallengeAccepted

2
103
Crypto bugs don’t always scream.
Sometimes they hide in a helper function.
I wrote about a Critical FROST threshold-signing bug where incomplete nonce-context binding could lead to secret-share recovery.
#BugBounty #Cryptography #SecurityResearch
medium.com/@trffnsec/two-sig…

2
113
I just pwned the "Dojo #51 - DeadBolt" challenge on @YesWeHack!
Who’s next to join the fun? 🚀
dojo-yeswehack.com/challenge…
#YesWeHack #ChallengeAccepted

3
123
I just crushed the "Dojo #49 - Secret manager" challenge on @YesWeHack!
Ready to learn and pwn? 🌟
dojo-yeswehack.com/challenge…
#YesWeHack #ChallengeAccepted

1
2
289
Tr.ffn 🇦🇪 retweeted

Found an interesting Android target in a Bug Bounty Program but have no idea where to begin?
Here’s a simple workflow to follow 👇
