
Lisp to Script compiler: https://xitter.cf/t.co/GkISb9T8oB Free support on discord: https://xitter.cf/t.co/BWKWJev5u9
Joined April 2019
- Tweets1.5K
- Following429
- Followers306
- Likes1.3K



Pinned Tweet
I wrote a Lisp->Script compiler for #bsv
Thanks to feedbacks from early testers it should be ok to use. So here is the documentation: replit-docs.frenchfrog42.rep…
It has a link to a "repl" where you can use the compiler (no download required)
If you have any feedbacks, let me know


Damn sCrypt is very very legit tech now 🔥🔥🔥
Congrats to them all! Can’t wait to see that in prod live on btc ahah

The first step toward a trustless L2 bridge connecting Starknet to Bitcoin has been achieved by @scryptplatform!
A few months ago, we partnered with sCrypt to build a Bitcoin Signet (OP_CAT-enabled) PoC bridge, designed to lay the foundation for a production-grade bridge for Starknet.
Today, they’ve officially shipped a smart contract on Bitcoin Signet capable of locking and unlocking funds; in other words, a trustless bridge between an L2 and Bitcoin.
As a key milestone in enabling Starknet to scale Bitcoin, we strongly encourage you to explore the bridge design in this article:
starkware.co/blog/implementi…

Damn 👀👀👀👀

** ZKPs live on Bitcoin SV mainnet!! **
In a world first, we have implemented Groth16 verification on BSV mainnet at a cost of just 1.5 cents. It opens up a whole new era of smart contract functionality on Bitcoin that is practical and cost-effective as of today.
This is a massive achievement that required a new approach to Bitcoin scripting. I couldn't be more proud of the team at nChain R&D!
Read more in Wei's article below. Full academic paper coming soon.
medium.com/@w.zhang/snark-ve…
Ok too much hype on the brc20/ordinal thing
Is there something interesting to build there with SCRIPT?
Would be very nice if I can leverage my knowledge of script to build something
Nikamoto [SV] retweeted

6/ the validators need to go off chain to begin discussing what to do!
Where do they go? Discord! 👀
They then need 66% of validators I believe to agree on a solution to get back up
But what if many aren’t available? Maybe sleeping or just unavailable? 🤔

"Track unique number" -> may be a solution to b2g
Anon please try :))

3/ For those who don’t know, every Bitcoin can be subdivided into 100,000,000 satoshis. Recently, @rodarmor found a way to associate a unique number with every satoshi so that they can be individually tracked and transferred.


I moved from getrevue to substack. Please subscribe here to my newsletter nikamotosv.substack.com
New post soon^tm on recursive functions

Airlines don't APIs to check price and book? Why?
The only websites I find are offering free APIs call up to X calls per booking
Is it to upsell customers useless stuff? Prevent price analysis?
Why is this not true?
Easy to use API => more middle men's => less fees paid to them?
Revue (where I host my blog) is shutting down
Any bsv powered alternative? Or any interesting alternative?
@ProjectBabbage do you have something I can copy paste that could be a blog?
Otherwise I'll go with substack I think
Tried my library (my submission to the hackaton) on one of the project. Works as planned. Size is 1 954 015 instead of 7 575 932
(Haven't tested tho, but should work fine)
ZK project creators, all you have to do is replace a single file. Check diff here github.com/frenchfrog42/zk-m…


Bitcoin + ZKP is a win: the 1st-ever Bitcoin Zero-Knowledge Proof hackathon finalists are here bsvhackathon.devpost.com/pro… #BSV

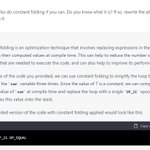
Teaching an AGI how to compile
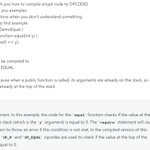
It's somewhat interesting, but can't make it learn a lot of stuff. It fails to compile
contract DemoEqual {
public function equal(int a, int b) {
require(3*a == 2*b);
}
}
but is fine if there is only the 3*, or only the 2*


Somehow it somewhat gets what needs to be done, but fails to write the opcodes
Probably hard for it to reason about the position in the stack of each element
Will try to compile to an assembly with variables later


At the ZK hackaton thing, I optimized the smart contract that verifies ZK proofs
The verifier code is now 1.27MB instead of 5MB
A quick thread about it & scrypt optimization in general
However the code is properly tested. I overall just rewrote 7 functions. Each of them is tested against the scrypt implementation against random inputs
It should be correct and safe to use
Here is my hackaton submission devpost.com/software/zkbague…
And the associated github repo github.com/frenchfrog42/zk-h…
If you build a ZK app please use my code, just copy/paste the bn256.scrypt and bn256pairing.scrypt files, and enjoy reduced fees (from 5MB/9MB to 1.27MB/1.38MB) 🚀🚀🚀🚀
