

Professional security consultancy based in North Wales and providing services UK wide.
UK
Joined February 2011
- Tweets1.1K
- Following485
- Followers270
- Likes205


Pinned Tweet
Ransomware: Don't panic - deal with it j.mp/1WGG4hv #CyberEssentials #InformationSecurity #malware #Ransomware #Security
Halkyn Consulting retweeted

U.S. DoJ Dismantles Warzone RAT Infrastructure, Arrests Key Operators i.securitythinkingcap.com/T2…

Halkyn Consulting retweeted

2023 Zero-day vulnerabilities Summary
R1 - 14 Jan 2024
H/T @uuallan @pancak3lullz for the original idea
(I was missing yours, so I made my own but included all zerodays, not just initial access for ransomware as the original was.)

Halkyn Consulting retweeted

Come and join our #Cybersecurity #summit this Thursday and Friday online (UTC+1): eventbrite.com/e/brussels-cy…. I'll be moderating the #CTI track with these amazing speakers during the live stream: @paulvixie @stefant @trompi @craiu @FDezeure @netnod @juanandres_gs and many more!


🙌🏽 Join the virtual Brussels Cybersecurity Summit on Jan 18 and 19, 2024! An initiative of the @Centre for Cybersecurity Belgium
Get your tickets 🎫
eventbrite.be/e/brussels-cyb…
#eu2024be #brusselscybersecuritysummit #cybersecurity

Halkyn Consulting retweeted

⚠️ A new exploitation technique called '📩 SMTP Smuggling' could let attackers send malicious emails with fake sender addresses while bypassing security measures.
Read more 👉 thehackernews.com/2024/01/sm…
#infosec #cybersecurity #hacking

Protect Your Business with Our Premier Incident Response Service!
#cybersecurity #infosec #dfir
linkedin.com/feed/update/urn…

Halkyn Consulting retweeted

It took me almost 3 years, but I finally restructured the Practical Malware Analysis section of my site. This is now broken up into more digestible sections, and I've also revamped the MITRE ATT&CK tests to come with appropriate categories and tagging.
jaiminton.com/Tutorials/Prac…


Cyber security people: Ever heard the term "VAD tree" and wondered what it meant?
Check this out for an easy-to-read explanation: linkedin.com/posts/taswake_d…

Linux Incident Response - introducing objdump.
#Linux #DFIR #Forensics
linkedin.com/pulse/linux-inc…
Halkyn Consulting retweeted

U19s ⚽
MIFC vs. @CPDCaerwysFC
📅 Saturday 10th September 2023
⏰ 13:30 kick off
🏟️ Argoed Sports Club, CH7 6SZ
🏆 @FlintshireJnrFL Youth League
💵 Free entry
Match Sponsor: Margden Heating
Please show the lads your support as they begin their league campaign! #uptheisa 🟡⚫

Halkyn Consulting retweeted

🚨Sponsor Appreciation Post🚨
A big thankyou to our sponsors this season: @HalkynSecurity, OMS, LP Builders and @MaestrosMaking. It means a lot to have your support on the shirt and on the sideline.
On behalf of coaches and players, a huge thank you. We are incredibly grateful


Halkyn Consulting retweeted

1/ Windows Error Reporting (WER) can provide investigators with a wealth of data including:
• SHA1 hashes of crashed processes
• Snapshot of process trees at time of crash
• Loaded modules of crash
• Process minidumps
#DFIR #Threathunting
See 🧵 for new #Velociraptor artefact

Halkyn Consulting retweeted

Additional BR C4
18.176.11.157
3.113.109.1
164.90.181.205
142.93.230.121
13.82.141.216
spectrumofinnovation.]org
152.67.78.82
170.254.185.1
3.27.18.66
20.74.155.146
52.199.127.115
54.92.22.199
85.208.22.36


Threat actors using nation-state tradecraft have begun to adopt the pentest tool #BruteRatel C4 bit.ly/3acaivi


Halkyn Consulting retweeted

Threat actors using nation-state tradecraft have begun to adopt the pentest tool #BruteRatel C4 bit.ly/3acaivi


Halkyn Consulting retweeted
Catch @Intel471Inc presenting at the @SANSInstitute #RansomwareSummit this week! Intelligence analysts Samantha Van de Ven & Beth Allen will be presenting research on Access Brokers and Threat Actor Partnerships on June 16th at 10:00 am ET. hubs.la/Q01dv2M-0

Halkyn Consulting retweeted
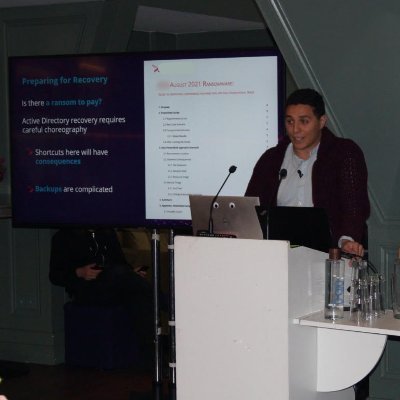
There are lots of blue team guides for monitoring & detecting, but there's not much on what to actually DO when you catch an active adversary.
This article's small contribution is to help you evict the adversary in your environment 🧵
huntress.com/blog/evicting-t…

Halkyn Consulting retweeted

This thread is 🌶🔥🌶🔥🌶 #dfir

There are lots of blue team guides for monitoring & detecting, but there's not much on what to actually DO when you catch an active adversary.
This article's small contribution is to help you evict the adversary in your environment 🧵
huntress.com/blog/evicting-t…
Halkyn Consulting retweeted

1/ So you go shopping for a PIV card reader, because the US govt gave you one and you're curious to look at what's on it. You settle for this "DOD military USB common access smart card reader," because it's compatible with Mac OS. Cool! Only $15! What a bargain!
