

Cyber Security Engineer @Resecurity || Intigriti Top 25 || Intigriti 2023 Q3 Leaderboard 1st || Bug Hunter || Penetration Tester || Programmer || Student
Bangladesh
Joined January 2019
- Tweets649
- Following827
- Followers1.9K
- Likes10.3K




Pinned Tweet
My 2023 #BugBounty Recap
- Earned 41,000K$+ in Bounties ( From @intigriti & @Bugcrowd )
- Made it to worldwide top 25 in @intigriti
- Made it to worldwide top 542 in @Bugcrowd
- Top 1 worldwide in 2023 Q3 @intigriti
I just hunt around 6 month this year.


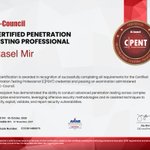
🎉 Passed the EC-Council CPENT Exam!
Happy to achieve another milestone in my cybersecurity journey. 🔐
Grateful for the learning experience and excited for what’s next! 🚀
#CPENT #ECCouncil #Cybersecurity #PenetrationTesting #InfoSec

1
9
731
In some cases, they claimed that a certain domain doesn’t contain real user data, yet they still haven’t marked that domain as out of scope.
Even though the triage team reviewed my reports, once the program manager added such comments, the process just stopped there.
2/n
2
601
Rasel Mir retweeted

🚨 OSCP GIVEAWAY ALERT🚨
We’re giving away 3 OSCP vouchers to supercharge your pentesting journey – proudly sponsored by @offsectraining ! 💥🙌
To enter:
1.✅ Follow Us
2.🔁 Retweet this post
3.❤️ Like this post
4.💬 Reply with your funniest cybersecurity meme
🎯 We’ll pick 3 random winners – don’t miss your chance to win the gold standard in offensive security!
🗓️ Deadline= 20 June
Let the hacking+meme battle begin! 🧠💻
#OSCP #OffSec #Giveaway #BSidesAhmedabad #Infosec #Cybersecurity

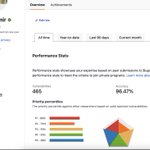
🔒 Just hit a new milestone on @Bugcrowd !
⚡ 465 valid vulnerabilities
📈 96.5% accuracy
🏆 Ranked 295th globally
Proud to be doing what I love: helping secure the web, one bug at a time.
#BugBounty #EthicalHacking #CyberSecurity #Bugcrowd

Last few days I submit few interesting bug on @Bugcrowd program collaborating with @akbar_ohi . It was an excellent experience.
We earned $$$ for our submission on @bugcrowd #ItTakesACrowd

Wrapped up my bug bounty presentation 20th February! 📷 Had an amazing session sharing knowledge and connecting with future ethical hackers on Cumilla University.
#BugBounty #CyberSecurity #EthicalHacking


20
1,039


Agree. Recently I face same issue with the @Bugcrowd. My 20+ report mark as duplicate with the one report and that report is not match with my report path, parameter, Disclose information also.

@Bugcrowd @Hacker0x01
Why not hire people like who have seen the struggle of real hunting? Why not hire people who are working day/night for years, These people are Gems, They know what are the real problems and how to overcome them.
Hire bug hunters instead of Pentesters,
Hire talent instead of certs,
Hire those who would love to build the platform.
90% reports goes to N/A because Triagers (Pentesters) couldn't understand it.
5% goes to invalid priorities.
4% goes to no response.
1% goes to accepted because ur lucky that time.
There were times when triagers (Bug hunters) help hunters to exploit their submissions to escalate the priority (Bug hunters).
vs
We don't have time to check your report, Kindly create a video because it takes time to create a new user (Pentesters).
14
1,137
Nice finding. And got more motivation for finding P1.

Exciting News: My Second Write-Up is Now Available!
medium.com/@HX007/a-journey-…
Dive into the details of the bounty that ranks as the 3rd highest I’ve received on @Bugcrowd
"A Journey of Limited Path Traversal To RCE With $40,000 Bounty!"
Collaborated with @GodfatherOrwa ,
This Write-Up is not just informative but also a fun read.
Enjoy reading and happy hunting!
#BugBounty #BugBountyTip #BugBountyTips #Bugcrowd #HackerOne #SOC #CyberSecurity #infosec

2
451
Rasel Mir retweeted

👍Thanks to @RashedulCSS's organization, we have seen the style of Bangladesh security researchers! 🥰We also look forward to more fresh blood joining us in 2025! Contribute your strength to the 2025 TECNO security journey! #infosec #bugbounty #AppSec #cybersecurity #hack #MEETUP


I found a target site 3rd party subdomain like target.okta.com. And from web archive I got a link where leaked PII data. Should I report or not ?
@GodfatherOrwa @krishnsec
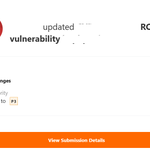
I never twitted about any platform. But this is totally unacceptable @Bugcrowd. 17 days ago one RCE is triaged by @RelentlessT7 . Today I see this bug mark as “Informational”. Program team says this is their test environment.
1/n

3/n
Finally that RCE bug accept as P3. At least accepted. That's why I am happy. Thanks @RelentlessT7

1
7
612


Sorry sir 😅
I am trying to focus on android and IOS. And this is the result. I didn't understand the out of scope properly. Actually out of scope is soo confusing. That's why this is happed.

@araselmir Sir ,
Ig you found something dangling ,hope you share soon about your research😁🤞
#bugbounty

2
4
1,928