

The 2 minutes that matter from 3-hour AI interviews. Fact-checked, no hype.
Joined April 2022
- Tweets203
- Following104
- Followers30
- Likes212


Pinned Tweet
Most people use AI every day without knowing the five equations running it.
They explain why it sounds sure and is wrong, why it forgets, why answers change, and why it would rather guess than say “I don’t know”.
All fact-checked. All fit on a napkin.

6 hours to remove 47 records is impressive. it's also the hard way.
if you live in California, there's now a state tool called DROP. one request goes to 600+ registered data brokers, and they get 90 days to delete you.
AI is great at writing the requests. the law is what makes them stick.

step 5: close old accounts.
search your inbox for "welcome", "verify your email" and "your account". that's your list of forgotten accounts.
ask Claude to find the delete-account page for each one. justdeleteme.xyz also lists direct links for hundreds of sites.
step 4: use the law, it's faster.
- California: use DROP. one request goes to 600+ registered brokers
- EU / UK: under GDPR you have the right to erasure. companies generally have one month to respond
ask Claude: "write a GDPR erasure request to [company], short and formal"
step 3: data brokers.
most have an opt-out page buried in the footer. ask Claude:
"for each of these sites, find the official opt-out or data deletion page and write me a short removal request with my details: [name, city, email]"
then send them one by one.
step 2: remove yourself from Google results.
Google has a free tool called "Results about you". it finds search results with your phone, home address or email and lets you request removal in a few clicks.
it won't delete the page itself, but it hides it from search. that's most of the damage.
here's how to do it yourself, step by step 🧵
step 1: find where you are.
google your full name + city, your phone number and your email in quotes. then check your email on haveibeenpwned.com to see which old accounts leaked.
paste everything you find into Claude and ask: "group these by site and tell me which ones are data brokers"

A 13-year-old wrote a free Polymarket bot, a stranger made $200,000 with it and sent him $20,000. Heartwarming story. One problem: the numbers keep changing.
In July, a different account posted the same story. Back then the kid was 14 and the thank-you was $18,000.
Same summer break. Same GitHub upload. Same “two months later.” Same $200,000 month.
Neither version names the kid. Neither links the repo. Neither shows the transfer or the trader.
When a story gets younger and richer every time it’s retold, it isn’t news. It’s a template.
And the template sells something. It tells you there’s a free trading bot on GitHub that can make you $200,000 a month, and all you have to do is find it and run it.
That is exactly the wrong lesson to take from it.
A trading bot needs access to your account or your wallet keys. Running a stranger’s code with those keys is how people lose money, not how they make it.
Just last week, attackers slipped malicious code into a third-party script on Polymarket’s own site. In under an hour it moved about $2.6 million from 726 wallets. Polymarket is refunding traders.
Free code is great. Unverified code with your money attached is not.
Watch the clip. Then ask the only question that matters: where are the receipts?
Will Stephen gave a TEDx talk with nothing to say. He told the audience so. Then he spent six minutes sounding brilliant anyway.
He was a Saturday Night Live writer, and the talk is a parody: “How to sound smart in your TEDx Talk.”
He opens by asking the room a question anyone can answer. He tells a small personal story. He shows a pie chart and a bar graph that mean nothing. He admits his glasses are just frames, and his vision is perfect.
At one point he says it plainly: if you watched with the sound off, you’d think he knew what he was talking about.
That’s the joke. The structure sounds like expertise even when the content is empty.
Here’s why it lands differently in 2026.
AI chatbots are very good at the structure. A confident opening. A neat list. Numbers. A tidy conclusion.
None of that proves anything is true. Polish and accuracy are two different skills.
A well-formatted answer can be just as empty as Stephen’s slides. The tone of expertise is the easy part to generate.
So the useful question isn’t whether something sounds smart. It’s what it actually claims, and whether you can check it.
Stephen proved this with a clicker and fake glasses. AI makes the same trick cheap and endless.
The talk is free on YouTube. Watch it with the sound off first. Then turn it on.
One engineer, 50 AI agents, coffee every morning. That’s the fucking fantasy going viral.
Lauren Tan actually ships about a thousand PRs a month with agents. Her real secret: she spends MORE time checking their work, not less.
The bots don’t replace the engineer. They make her the bottleneck.
his is a fucking video game that can get you into a real robot fight.
REK’s simulator runs on the same AI as their six-foot humanoid fighters. Top the leaderboard and you could end up piloting a real one in a cage.
Gamers are about to become robot fighters.
if you use Claude Code inside Cursor, check your extension version right now.
a tampered build, anthropic.claude-code 2.1.313, showed up on Cursor's marketplace yesterday. the moment the extension loaded, it quietly:
- added the attacker's SSH key to your machine
- turned on SSH and opened a reverse tunnel out
- set itself up to survive reboots
no click needed. just opening the editor was enough.
what's not affected, per the researchers: the npm Claude Code CLI and the Microsoft VS Code version.
quick check:
- grep "svc-telemetry" in ~/.ssh/authorized_keys
- look for com.apple.sysmond (macOS), a SysMon task (Windows) or an @reboot cron (Linux)
if anything hits, the researchers' advice is blunt: rotate your keys from a clean device and rebuild the machine. deleting the files isn't enough.
the scary part isn't the code. it's that the extension looked exactly like the real one.

Claude Code found 214,856 files I thought I'd permanently deleted from my Android.
Three years of photos, videos and screenshots. Still there.
I connected my Pixel to my MacBook and asked Claude Code to search for deleted files.
It found a hidden folder:
DCIM/.thumbnails
Over 215,000 files dating back to 2021.
What was inside shocked me.
A passport photo. Banking screenshots. Private photos from a breakup. My crypto seed phrase. Pictures of my ID and credit card.
Things I was certain I'd erased.
Most were compressed previews. Some were nearly full size.
None appeared in my gallery's Trash.
Here's what nobody tells you:
Deleting a photo doesn't always erase its cached previews. Some can survive long after the original is gone.
Then I checked app permissions.
27 apps had storage or media access.
Weather apps. QR scanners. PDF readers. Apps I'd forgotten existed.
I cut that list down to 5.
Modern Android limits file access, but leftover caches and unnecessary permissions are still worth checking.
The scary part?
I thought deleting meant gone forever.
Full step-by-step below.
Save this. Every Android user should know.
A viral post says a 19-year-old built a trading bot with Claude Code in 48 hours and turned $68 into $750,000. Before you believe it, look at what the post leaves out.
No name. No trade history. No wallet address. No screenshots of the account. Nothing you can check.
What it does include: a “Paid partnership” label from X, and a Binance sign-up link with a referral code right in the middle of the story.
That’s the business model. The bot story is the ad.
This template isn’t new. Earlier versions claimed a student turned $0.90 into $408,000 in 48 hours. Italian outlet Money.it ran the numbers: around 1,600 trades, one every two minutes, with order books too thin to fill positions that size.
The technical idea is real. Bots can spot tiny price gaps between exchanges and markets, and Claude Code can help write that kind of script.
The returns are not. Those gaps are small, everyone is hunting them, and they close fast once known. Fees and slippage eat most of what’s left.
Claude Code writes code. It doesn’t know which trades will win, and it doesn’t make a $68 account immune to losses.
If a post promises life-changing returns and asks you to sign up through a link, the link is the product.
The clip shows how easy it is to fake a dashboard like this.

19 岁日本学生,用 Claude Code 两天搭出交易机器人:68 美元起步,第一晚赚 6732 美元,总利润做到 75 万美元
他把 iPad 当成第二块屏幕。
第一晚:6732 美元利润。
起始资金:68 美元。
迄今总利润:750,000 美元。
它是怎么跑的:
· 机器人同时扫描 50 多个市场
· 每秒从 Binance 同步实时 BTC 数据:
accounts.binance.com/registe…
· 在人类注意到之前,先发现价格错误
· 核心优势就两个:纯粹的速度 + 模式识别
当交易员还盯着图表猜下一步,他的机器人已经在几十个市场里执行错价交易。
没有猜测。
没有情绪。
没有犹豫。
就是 Claude Code 的逻辑,去找那些几秒内就关闭的价差。
他用 48 小时搭完整个系统:
→ Claude Code 处理交易逻辑
→ Binance API 提供实时 BTC 数据
→ iPad 显示多市场监控
→ 套利窗口一开,自动执行
系统 24/7 运行。
每一个价格错位,就是一个利润机会。
大多数人还在手动交易、刷新图表、犹豫要不要进场。
与此同时,这个 19 岁工程学生让 Claude Code 去做人类做不到的事:即时处理 50 个市场,并且无畏执行,把 68 美元变成了 75 万美元。
所以问题来了:为什么人们还在手动交易?
A like costs nothing. A long press will cost $1.
That's the whole bet: turn the cheapest action on X into a payment, so creators get paid by fans directly, not only through ad revenue share.
Two things to watch:
- X Money launched in the US this year. No word yet on when creators outside the US can get paid
- no date or fees announced. it's an announcement, not a launch
If even 1 in 100 likes turns into a dollar, a post with 1,000 likes pays $10.
The number that matters stops being likes. It becomes how many fans would actually pay you.


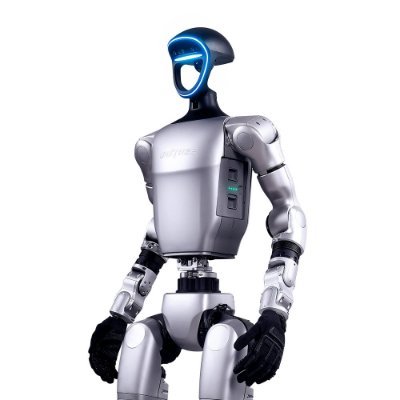
Unitree’s new humanoid dents a car with a kick, does backflips, and lifts the front of a vehicle.
They’re pitching it as a guardian.
The demo doesn’t establish how autonomous it is. But it raises a very practical question:
Would you trust a robot this strong to decide when to intervene?

The 4090 numbers come from one card and one cold boot, per the repo's own README. Linux only, and the author calls them issue rates, not inference speedups. Worth waiting for independent tests.

Modders unlock hidden AI performance on NVIDIA RTX 20, 30 and 40 series GPUs, with up to 2× tensor throughput
🔗videocardz.com/newz/modders-…

Linux went the opposite way. Torvalds called rules like "don't use AI for X" utterly stupid, and the kernel recently dropped its Assisted-by disclosure tag. The rule is simple: you own every line, however you wrote it.

