

Offensive Security & Exposure Management Platform 🎯 https://xitter.cf/t.co/57gODBq2WZ 👾 https://xitter.cf/t.co/ICc6RyhJTp 💡 https://xitter.cf/t.co/KNYxhkKuzt
World
Joined July 2012
- Tweets9.4K
- Following3.4K
- Followers43.4K
- Likes9K


YesWeHack ⠵ retweeted

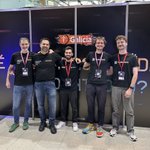
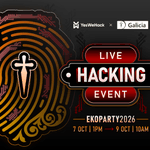
¡Sumate a @BancoGalicia Super Live Hacking Event! 🔥
En colaboración con Banco Galicia y @yeswehack organizamos un exclusivo evento de hacking en vivo durante la EKO Buenos Aires 2026. 🚀
🚩 ¿El objetivo? Banco Galicia. Los participantes van a tener la oportunidad de poner a prueba su seguridad, buscar vulnerabilidades y demostrar sus habilidades de bug hunting sobre un scope especialmente preparado para el evento.
Durante el evento, no solo te vas a sumergir en el hacking, sino que también vas a poder colaborar con otros bug hunters, e interactuar con expertos en seguridad de Banco Galicia y YesWeHack. Y, por supuesto, habrá jugosos bounties y mucho swag para quienes encuentren bugs. 🤓💪
👀 La competencia estará abierta a los asistentes presenciales durante el miércoles y jueves de la EKO, pero todavía no podemos contarte todo. En los próximos días vamos a revelar las fechas, horarios, dinámica y todos los detalles para que puedas sumarte.

YesWeHack ⠵ retweeted
Our Bug Bounty Bulletin – featuring a research roundup, new hacking opportunities, technical advice & hunter Q&As – is now available on X!
Inside: high-calibre research from @albinowax @t0xodile @garethheyes @olivier_boschko @citizenlab & more 👇

YesWeHack ⠵ retweeted

We're thrilled to welcome @yeswehack as a Silver Sponsor of Bug Bounty Village at DEF CON 34! Their ongoing support helps us create a space for hackers to connect, learn, and push boundaries.
#defcon #bugbounty #bbv #bugbountyvillage


YesWeHack ⠵ retweeted
🚨Bug bounty opportunity for ethical hackers:
#OpenProject has launched a public bug bounty program via @yeswehack, supported by the European Commission.
Learn how to participate and help secure open source: openproject.org/blog/bug-bou…
#OpenSource #BugBounty #DigitalSovereignty

ALT Man sitting in front of screens showing a developer console and OpenProject, with text overlay 'Bug bounty
YesWeHack ⠵ retweeted

📱 Des hackers piratent le ministère de l’Intérieur : des fichiers sensibles volés
🎙️ "Ça peut arriver partout", indique Pierre-Paul Giannetti, Consultant sécurité offensive YesWehack. "Ces mécanismes d'attaque ne sont pas nouveaux"
#ApollineMatin
YesWeHack ⠵ retweeted

Limitations are just an illusion – advanced server-side template exploitation with RCE everywhere - @yeswehack
yeswehack.com/fr/learn-bug-b…

YesWeHack ⠵ retweeted
Android Recon for Bug Bounty
Learn how to extract APKs, find hidden endpoints & secrets before exploitation using tools such as:
APKeep, APKTool, apk2url, jadx-gui, MobSF, MARA, Drozer
yeswehack.com/learn-bug-boun… via @yeswehack

YesWeHack ⠵ retweeted

Check out this great article by @yeswehack on google dorking: yeswehack.com/learn-bug-boun…


YesWeHack ⠵ retweeted
The minefield between syntaxes: exploiting syntax confusions in the wild - @yeswehack
yeswehack.com/learn-bug-boun…

YesWeHack ⠵ retweeted
How to build Android Bug Bounty lab
Guide to configuring emulators, real devices, proxies, Magisk, Burp, Frida by @yeswehack
yeswehack.com/learn-bug-boun…


YesWeHack ⠵ retweeted
The best thing I've read in months. Outstanding research.

Find the full article here ⤵️
yeswehack.com/learn-bug-boun…
YesWeHack ⠵ retweeted

HackerNotes TLDR for episode 145! — blog.criticalthinkingpodcast…
►⠀Syntax Confusion: Two or more components in a system may interpret the same input differently due to ambiguous or inconsistent syntax rules. Learn more in @yeswehack's new blog: The Minefield Between Syntaxes: Exploiting Syntax Confusions in the Wild (yeswehack.com/learn-bug-boun…)
►⠀The Note GOAT: Download @gr3pme's note templates:
⠀•⠀General Template - terrific-dart-70e.notion.sit…
⠀•⠀JS Monitoring Template - terrific-dart-70e.notion.sit…

YesWeHack ⠵ retweeted

Guillaume Vassault-Houlière présente les hackers éthiques de YesWeHack (cc @yeswehack) 🎥 🎙 C'était aux Assises de la cybersécurité (cc @Les_Assises) #YesWeHack #ethicalhacking #hackeréthique #cyber #cybersecurity
YesWeHack ⠵ retweeted

Still amazed at how fast things move on @yeswehack Reported a bug this morning → accepted within 1 hour → fix pushed another hour later! Incredible turnaround 👏


YesWeHack ⠵ retweeted
My writeup for the July Dojo challenge on @yeswehack - CCTV Manager 🎥
1️⃣ Predict the correct token to access the CCTV manager (insecure time-based PRNG)
2️⃣ Exploit the yaml.load() function to achieve RCE
Read the full writeup and PoC script ➡️ book.cryptocat.me/ctf-writeu…

ALT CCTV Manager (YWH July Dojo)
YesWeHack ⠵ retweeted

Good writing here by @yeswehack. When I get nostalgic on recon, I often 'dig' into the past using some variation of what's mention in the article, though my approach is more manual than tools (by simply spending more time on wayback machine).
yeswehack.com/learn-bug-boun…

YesWeHack ⠵ retweeted

🇬🇧🔓 Hack live, earn real 💰
@YesWeHack’s Live Bug Bounty is back @ leHACK!
🗓️ June 28–29 | @ Le Loft
🎯 Exclusive target, open to all attendees
🎟️ billetweb.fr/lehack-2025-the…
🕹️ yeswehack.com/page/yeswehack…
#leHACK #BugBounty
