

@Web3_Devs
Account based inIsrael
About this account
- Account based in
- Israel
- Connected via
- Israel App Store
Account-level information from X, not a live location or the device used for a specific post.
Join us! Luma https://xitter.cf/t.co/vZULX1wZuc Telegram https://xitter.cf/t.co/5SLGVdjGgG Meetup https://xitter.cf/t.co/YYNSBxNC4I
Web3
Joined March 2025
- Tweets583
- Following38
- Followers492
- Likes628




Are token sales back?
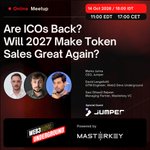
@zord4n joined The Underground to walk us through how @jumperapp ran theirs on @legiondotcc.
It drew $48.6M with a $3M hardcap.
Are ICOs Back? Will 2027 Make Token Sales Great Again? | Web3 Devs Underground xitter.cf/i/broadcasts/1wxWjlwmB…

Starts in 60 minutes!
We'll be streaming here on X, so pay attention to this feed and set a notification 🔔

The @jumperapp sale on @legiondotcc drew $48.6M for a $3M cap.
In 4 hours, CEO @zord4n joins @notdevid and @SHAP0W to break down how it happened.
🕕 Today · 18:00 IDT / 17:00 CEST / 11:00 EDT
📍 Online Live Stream
There's still time to register 👇
luma.com/web3devs-xllv

The @jumperapp sale on @legiondotcc drew $48.6M for a $3M cap.
In 4 hours, CEO @zord4n joins @notdevid and @SHAP0W to break down how it happened.
🕕 Today · 18:00 IDT / 17:00 CEST / 11:00 EDT
📍 Online Live Stream
There's still time to register 👇
luma.com/web3devs-xllv
Web3 Devs Underground retweeted
Just in: @jumperapp's JUMP sale on @legiondotcc drew $48.6M in applications at a $3M hard cap. 16x oversubscribed.
Next week, Jumper CEO @zord4n joins @notdevid and @SHAP0W to break down how.
Are ICOs back?
📅 Wed Oct 14 · 🕐 18:00 IDT · 📍 ONLINE
luma.com/web3devs-xllv

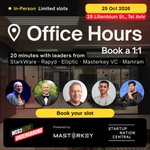
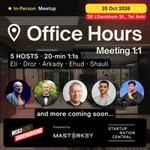
You're all invited to Office Hours on Sun 25 Oct in Tel Aviv: 20-min 1:1s with Eli Ben Sasson, Dror Avieli, Arkady Karpman, Ehud Naos and Shauli Rejwan. Bring a real question; the hosts pick who they meet. Free, apply by 18 Oct.
office-hours-landing.vercel.…

Yes, AI has the potential to find bugs we didn’t know existed, but what if there are none?

I don't recommend anyone scramble to move their funds to new wallets today. But we should take the risks to cryptography from AI-accelerated math seriously, and minimize our exposure to not just quantum-vulnerable cryptography, but also potentially AI-vulnerable cryptography.
The core new area of risk from this viewpoint is, unfortunately, ML-DSA / FHE / lattices.
(and it's also another reason, along with quantum, why ECDSA might fall even faster than expected, hence the "fresh address" recommendation)
So far most people have been in the mode of thinking "elliptic curves broken, hashes safe, lattices safe". But there is a good chance that the concrete security of lattices will take serious hits from the next two years of AI math.
The basic threat model is: factoring is something that naively takes 2^(n/2) time, but over decades smart people have found and optimized number field sieves, and degraded that to 2^O(n^(1/3)), which is why RSA keys and signatures need to be ~400 bytes (and not 64 bytes). What if there are skeletons in the closet like that, both for elliptic curves and lattices, that we are simply not smart enough to discover - but bots soon will be?
This is a major part of the reason why for the past year ethereum's lean roadmap has been going in the "hash-only" direction: no lattices, no ML-DSA, no Falcon, no lattice-based commitments inside ZK proofs, etc. Signatures in lean ethereum are all hash-based, either WOTS or SPHINCS-.
For signatures and proofs, we already know how to go hash-only. The bigger challenge is for *public-key encryption* - and this goes far beyond blockchains. Secure communication, anonymizing protocols, lots of things need public-key encryption.
And unfortunately there are long-standing mathematical theorems showing why public-key encryption cannot be done with hashes alone. You have to have some kind of trapdoor object that has at least one form of usable "structure" - either group theory (incl. isogenies) or lattices or code-based or potentially in the future even more newfangled and spooky things (local mixing?). But for anything that has structure, you should assume that AI will make at least some progress in breaking that structure. Here, one reasonable inference is that if you want to make something plausibly long-term secure, multiply the key sizes by 10.
To me that's a very plausible world and something not at all extreme to predict. If AI will bring us 50 years of math in 2 years, then that 50 years of math may very plausibly include a "naive factoring -> GNFS" level of improvement to our ability to break lattices. In that world, lattices will still exist, but they will have to be significantly bigger to guarantee the same level of safety.
And at those new larger sizes, hash-based constructions will beat lattice-based constructions on concrete efficiency in every use case where hash-based constructions are possible at all.
Theoretically, of course it's possible that hashes are broken too (eg. P = NP would imply that). But I think P = NP is very unlikely. And intuitively, it's much more likely that a mathematical object has exactly no exploitable structure (like hashes are intended to), than that a mathematical object has exactly ~3 forms of exploitable structure (for elliptic curves: associativity, Schoof, pairings) and not some secret fourth form of structure we have not yet discovered that greatly degrades its security (for elliptic curves, ECDLP and pairing security). Similar for LWE, SVP, RLWE and the zoo of lattice problems.
For this reason, we do not yet see any reason to worry and start padding the byte size of hashes (if we start to worry more, we would pad the round count first before doing anything to the byte size).
Concrete TLDR, my own personal views:
* Hash-based > lattice-based, in those situations where hash-based is possible at all
* For anything lattice-based, be much more paranoid on param sizes. Remember that blockchains are only a small portion of the cryptography story; this point goes far beyond blockchains and applies to eg. access to websites, secure messaging, Tor / VPNs ...
* For privacy protocols, strongly favor NOT putting encrypted notes onchain. Instead, send them offchain through some third-party mechanism.
* If it's not difficult for you, keeping your funds in addresses which have not yet been used to make a transaction is a good idea. If it's easy for you, do it. **But be careful about migrations; I personally have lost more money in botched migrations than I have lost in all hacks combined**.
* For multisig wallets, doing confirmations offchain is better than onchain, because this way the signatures of signer wallets do not get exposed to the public, so if ECDSA falls to AI much faster than expected, at least the multisig "gracefully degrades" to a 1-of-1 where the 1 is whoever was gathering the signatures - a much better place to be than "anyone can take the money"
firefly.social/post/x/210783…

Just in: @jumperapp's JUMP sale on @legiondotcc drew $48.6M in applications at a $3M hard cap. 16x oversubscribed.
Next week, Jumper CEO @zord4n joins @notdevid and @SHAP0W to break down how.
Are ICOs back?
📅 Wed Oct 14 · 🕐 18:00 IDT · 📍 ONLINE
luma.com/web3devs-xllv


Mid-Chain is a one-day research conference at Ben-Gurion University on Mon 26 Oct. Free, by approval.
Seven of the thirteen talks have a paper you can read today. A reading list 🧵
luma.com/rzaklefv?utm_source…

The day before, Sun 25 Oct, at @sncentral_ in Tel Aviv: Office Hours, 20-min 1:1s with @EliBenSasson (@StarkWareLtd), @avieli (@elliptic), Arkady Karpman (@RapydGlobal), Ehud Naos (Mamram Alumni Assosiation) and @SHAP0W (@MasterkeyVC ). Then a panel and rooftop cocktails at 18:00.
office-hours-landing.vercel.…
