
CISO, Advisor, Investor
Joined April 2009
- Tweets69
- Following134
- Followers286
- Likes30


Kathy Wang retweeted

So excited for the partnership with Gem!

Today, we're thrilled to announce that over 30 leading CISOs have personally invested in Gem as part of @SVCIangels. We are incredibly excited to partner with SVCI as we revolutionize cloud detection and response.
Read more here: bit.ly/3qcS9oO
#cdr #cloudsecurity

Kathy Wang retweeted
SVCI PITCH DAY! 📣📣📣Our CISOs-turned-angel-investors got together this morning to connect with promising cybersecurity startups... And we can tell you this: The future looks bright! Thanks to everyone who attended and a special shout-out to the wonderful founders who joined us.

Kathy Wang retweeted
Congratulations @Tromzo on coming out of stealth, we are excited to officially welcome you to the SVCI fam. Tromzo is the textbook definition of founder-market fit, on the path to building a foundational platform for modern application security programs. siliconangle.com/2021/10/21/…
So glad that the company I work for @getVGS is helping out businesses that are hurting right now. VGS is holding a free webinar on how to implement their tokenization API for free until January – check it out get.verygoodsecurity.com/how…
Good opportunity to evaluate tokenization for your org's data!

Take VGS’ advanced tokenization solution for a test drive – don’t pay until January 2021.
verygoodsecurity.com/use-cas…

Looking forward to this event next Tuesday!

Join me and .@fykim .@wangkathy .@lennyzeltser .@russelleubanks & .@lspitzner for a virtual summit "Security Leadership: Managing in Turbulent Times" next Tuesday starting at 2:30 EST. #CISO sans.org/webcasts/security-l…
Looking forward to co-presenting with @iyampaul at this event!

Speaker Spotlight🗣 As companies continue to tune their #zerotrust model, they are finding osquery a powerful tool for securing huge #'s of corporate + server endpoints. @fullstory #CISO, @wangkathy, is a veteran in this area & is here to tell her story. #osqueryatscale

Join us! I’m hiring for multiple security roles - work remotely in US or Canada.

We're thrilled to announce that we've been recognized as the 28th fastest growing company in America by the Deloitte 2019 Technology Fast 500™ list! 🥳
Read more about this exciting achievement: prweb.com/releases/fullstory…

Very excited to be part of this great team, and looking forward to working together to raise the bar on security and privacy!
This quoted post is unavailable.
Kathy Wang retweeted

FullStory is now SOC 2 Type II certified! 🥳
Why are we celebrating and why is knowing something about SOC 2 engagements well worth your time? We cover it all here: blog.fullstory.com/fullstory…
The secure coding challenge is real. How do we close the gap in #devops?
Rob Lemos and I discussed in @DarkReading: ubm.io/2JHTH0Y
Looking forward to delivering this keynote in November. #CloudDevOpsSummit #ZeroTrust

Kathy Wang @wangkathy from @gitlab will keynote day 2 of our upcoming #CloudDevOpsSummit: Building Zero Trust: A Cloud-Native Perspective | Nov 4-5 | Denver | Agenda: sans.org/u/Qas

What kind of projects does a security #automation engineer work on at @gitlab?
Check out Alexander Dietrich's interview and find out: bit.ly/2XcxfGL

We're proud of the success that @ngalongc and @fransrosen have had so far in their career and grateful for their contributions toward making @GitLab more secure through our #bugbounty program! @Hacker0x01

How to make $1 million from hacking: Meet six hacker millionaires forbes.com/sites/daveywinder…

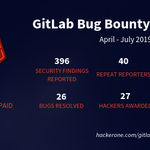
Our @gitlab #bugbounty reporters are helping us secure our product and services.
Another important outcome? Their input helps us identify vulnerability trends and focus areas for developer secure coding training: bit.ly/2SAgNKX
Thanks to our reporters!

Our security team is full of amazing individuals with diverse experiences and skills.
Sr. @gitlab security engineer, @awgneo helps us scale through his deep #automation expertise: bit.ly/2XR46kE

We implemented and adapted an #opensource #compliance framework at @GitLab.
Now you can too: bit.ly/2xDFjRB via @BurrowsJeff
.@gitlab Sr. #Security Researcher @simplenomad talks about the history of the hack and why you you should take the Occam's Razor approach when implementing security measures: usenix.org/publications/logi… via @usenix

What's it like working day and night to kill spam, bitcoin mining, malware and more? Meet @atiaxi, Senior @gitlab #Security Engineer: about.gitlab.com/2019/06/14/…
