

Upgrade partner with ALL major hardware and software vendors. For over 20 years we have worked with customers to find the right solution at the right price.
Tilford Surrey GU10 2DZ
Joined February 2009
- Tweets23.5K
- Following3.3K
- Followers2.5K
- Likes9K





Pinned Tweet
Your One-Stop IT Solutions Provider
We understand the pressure IT teams face - tight budgets, evolving threats, and constant change.
Whether you're looking to refresh your hardware, tighten your cybersecurity, or streamline procurement, we're here to help.
mailchi.mp/bab500cab198/intr…

You will have seen in the press that extreme heat has caused SEVERE DISRUPTION to I.T. in critical services like hospitals.
This can have a SEVERE FINANCIAL IMPACT ON YOUR BUSINESS TOO.
Its not worth gambling. Get the warranty now.
mailchi.mp/72615f653cb0/tigh…
FortiBleed credential-theft campaign linked to Lynx ransomware
bleepingcomputer.com/news/se… @BleepinComputer

🛡️ WinRAR Vulnerability Could Allow Attackers to Take Control of Your Computer
Source: cybersecuritynews.com/winrar… @The_Cyber_News

#FortiBleed credential-theft campaign linked to Lynx ransomware
bleepingcomputer.com/news/se… @BleepinComputer
🛡️ WinRAR Vulnerability Could Allow Attackers to Take Control of Your Computer
Source: cybersecuritynews.com/winrar… @The_Cyber_News

🛑 A new #Linux kernel exploit (CVE-2026-46331) gets root without modifying a single file on disk.
It poisons the cached copy of /bin/su in memory.
The root shell is already open.
Details here ↓ thehackernews.com/2026/06/ne… / @TheHackersNews #icymi

Upgrade Options Ltd retweeted

🛡️ WinRAR Vulnerability Could Allow Attackers to Take Control of Your Computer
Source: cybersecuritynews.com/winrar…
WinRAR 7.23 addresses a newly disclosed heap overflow vulnerability in the RAR5 recovery volume processing code, tracked as CVE-2026-14191. Closing a memory-corruption flaw that could be triggered by malicious recovery volume (.rev) data and potentially lead to application crashes or further exploitation.
WinRAR 7.23 is a security-focused maintenance release that primarily fixes two vulnerabilities impacting archive handling and extraction safety. The most critical issue is a heap overflow in the RAR5 recovery volume data reconstruction logic, which affects WinRAR, command-line RAR, and UnRAR components.
#cybersecuritynews

Windows Secure Boot Certificate Expired — Billions of PCs Affected, Including Linux Distros
Source: cybersecuritynews.com/window… @The_Cyber_News
Every UEFI-capable PC since the Windows 8 era, more than a billion devices worldwide, including systems running Linux distributions.

25 years ago, Microsoft’s CEO called Linux “a cancer.”
In 2026, Microsoft is shipping its own Linux distribution.
That’s not a joke. Azure Linux 4.0 is now public, free to download, open-source, and maintained by Microsoft.
It does not have a desktop or a GUI. @WindowsLatest

🚨 FortiBleed Attack Hit 430,000+ FortiGate Firewalls, Stealing 110M+ Credentials
Source: cybersecuritynews.com/fortib… @The_Cyber_News #icymi

🚨 CVE-2026-55200 now has public PoC code.
The libssh2 flaw lets a malicious SSH server trigger memory corruption in a connecting client.
> No credentials
> No user interaction
> Affected through libssh2 1.11.1
Learn more ➝ thehackernews.com/2026/06/pu… /@TheHackersNews

🛑 A new #Linux kernel exploit (CVE-2026-46331) gets root without modifying a single file on disk.
It poisons the cached copy of /bin/su in memory.
The root shell is already open.
Details here ↓ thehackernews.com/2026/06/ne… / @TheHackersNews
Upgrade Options Ltd retweeted
🛡️ Nissan Confirms Data Breach Following Oracle PeopleSoft 0-Day Attacks
Source: cybersecuritynews.com/nissan…
Nissan Americas has officially confirmed a data breach affecting current and former employees across four countries after threat actors exploited a critical zero-day vulnerability in Oracle PeopleSoft software, a campaign attributed to the ShinyHunters extortion group.
The attack stems from CVE-2026-35273, a CVSS 9.8-rated unauthenticated Server-Side Request Forgery (SSRF)-to-Remote Code Execution (RCE) vulnerability residing in the Updates Environment Management (PSEMHUB) component of Oracle PeopleSoft PeopleTools versions 8.61 and 8.62.
#cybersecuritynews #databreach

Your One-Stop IT Solutions Provider We understand the pressure IT teams face - tight budgets, evolving threats, and constant change. Whether you're looking to refresh your hardware, tighten your cybersecurity, or streamline procurement, we're here to help. mailchi.mp/bab500cab198/intr…

#Apple users told to watch out for 'unpatchable' #iPhone security issues - here's what we know techradar.com/pro/security/a… / @techradar

Windows Secure Boot Certificate Expired — Billions of PCs Affected, Including Linux Distros
Source: cybersecuritynews.com/window… @The_Cyber_News
Every UEFI-capable PC since the Windows 8 era, more than a billion devices worldwide, including systems running Linux distributions.

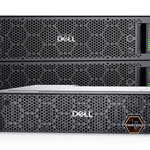
Business growth starts with storage
It’s Really Simple – Dell PowerVault ME5 delivers the kind of simplicity that Small and Medium Businesses require.
Want to Learn More?
mailchi.mp/35bcaa1cad10/arct…

You will have seen in the press that the heat is causing SEVERE DISRUPTION to I.T. in critical services like hospitals.
This can have a SEVERE FINANCIAL IMPACT ON YOUR BUSINESS TOO.
Its not worth gambling. Get the warranty now.
mailchi.mp/72615f653cb0/tigh…
"💻 Is your #DellTechnologies PC not detecting #USB devices?
Start troubleshooting now ➡️ del.ly/6018BBgP6i ⬅️
✅ Fix it today and keep your workflow smooth!
💡 Follow @DellCaresPRO for more #TechTips that keep you productive. "
🚨 FortiBleed Attack Hit 430,000+ FortiGate Firewalls, Stealing 110M+ Credentials
Source: cybersecuritynews.com/fortib… @The_Cyber_News
At the time of analysis, more than 80,553 FortiGate devices and 23,406 unique domains were implicated, with active sniffing on 19,000 firewalls.
