

Solutions to complex digital problems.
🇬🇧 🇨🇷 🇦🇪
Joined April 2014
- Tweets5.9K
- Following1.4K
- Followers10K
- Likes13.5K




I get messages like this all the time from people trying to buy @ticket from me on Instagram


stopping sophisticated bots is impossible.
i will die on this hill.

This isn't a solvable problem. It's a constant cat-and-mouse game. Everything can be emulated at a higher level, it is impossible to accurately detect sophisticated bots.
Whoever the founder is you spoke to cannot solve it, there's not a single antibot on the market that doesn't have a reversed solution you can't buy for a few beans on a discord server.
i say this because sophisticated bots are the ones real people using the internet see day-to-day.
The ones that are scalping shoes, tickets and pokemon
The ones that are posting on reddit, instagram and x
The ones that you're matching with on tinder and bumble
The ones buying restaurant reservations
The ones entering raffles
The ones reselling appointments for visas and driving tests
The ones posting fake reviews
The ones farming gold in online games to sell
this was my first real bot that was written 12 years ago, i scraped youtube channels and then mass messaged them inviting them to swap to a youtube network and would earn between 10-20% commission on all their earnings


The Adidas stock bypass:
So this was only protected on the Akamai WAF layer rather than being removed from the website meaning any Akamai bypass on the path would let me access the endpoint as if it was normal.
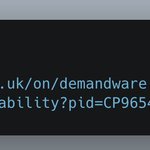
The rule spec was any path directory with "Product-GetAvailability" would be blocked. I had to find a way to trick Akamai into thinking it was a different path whilst the origin still returned the same content
The specific bypass for this was appending: "; %2f" before "Product-GetAvailability".
Akamai interacts with semicolons very strangely, it would ignore everything after the semicolon up until the next forward slash, in this case it was the %2f (encoded "/") This caused Akamai and the origin to disagree about what the URL truly means. Akamai thought it was different but Adidas' origin normalized it to the same demandware URL returning the correct response.
The reason for the massive quantity parameter was because if you put 1,000 it would only return up to 1,000 in the "IN_STOCK" quantity.


Me and @chillMati sold a bypass for $1m a few years ago. We had to fly out to meet them and everything, that was the first time Mati and I ever met in person.
Now I couldn’t imagine a life without him

Like every bypass, the method of accessing the product page was then patched, however, the queue bypass itself via ATC was still working at this point.
The problem was you needed the product's ID and the product's size IDs which could only be found on Solebox through the product page (Which was now queue-locked)
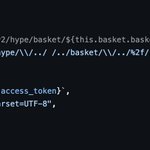
I dug into the OXID ecommerce Github repo and found a bunch of endpoints that I'd never seen before on Solebox but after researching on other sites that used OXID I found an amazing request that still worked on the backend, there was just no frontend way to use it on Solebox.
Since most php sites routed backend requests through index.php you'd just need to append these parameters
cl=suggest&
fnc=send&
anid=
Since the product IDs were incremental we could brute force these numbers, every time it would send me an email with the product name. Once we got an email with the product ID we were looking for, we would then know the IDs for each size but that was just +1 on the original product ID
So if the product ID was 1000, the sizes would be:
1001 = 36
1002 = 36.5
1003 = 37.5
etc
We could estimate the size range by going up to the number that gave us a different product email.
Before the product even went live we had these early ATC links that would bypass the queue that we would post to all our users.

The first bypass I found that got me started in Sneakers and bypass hunting was for off white prestos on Solebox. I was in a free cookgroup ran by @rycao18.
At the time I was programming in PHP and I saw a bug that affected a website I built. If didn't add the code "die();" after a location redirect it would attach the location header and the browser would redirect, but the code underneath would still execute if you made your browser ignore the redirect (or used something like curl)
So when I tested this on the Solebox product page it worked, I would not get redirected to the queue. I downloaded the source code and then hosted this page on a server and shared the link and watched people absolutely cook these prestos without having to go through the queue.
In hindsight, I could have just done add to cart links since what was really unprotected was the carting endpoint (No queue token was being sent/enforced) but this was my entrance into sneaker twitter and later starting Express Notify and finding many more bypasses

Selfridges used to restock hyped shoes but they would sit in stock because card checkouts and other payment methods wouldn't work for them. We would send people into Selfridges to buy gift cards which would let us buy all the available stock for these shoes.
Buying the giftcards online didn't seem to work either. In store Selfridges staff didn't want to sell £1000s worth of giftcards (I assume fraud issues) so you had to keep buying like £400 worth from different staff.
Guy we were paying for buying them ended up using the jig to loop his own pairs to sell. We caught him, banned him and then he got angry and then posted the method on the timeline


Another cool exploit I used a lot (that was surprisingly common) was finding exposed /.git/config paths and downloading the full source codes from a bunch of sneaker sites and bot websites
breakdown of how it worked:
en.internetwache.org/dont-pu…
When SNS restocked they had cart hold on their website, the problem was to cart a sneaker you needed to solve recaptcha v2.
We couldn't afford to use captcha solving services like 2cap and run them 24/7, always having 50-100 tokens ready to use for when a restock came in (I believe they expired every two minutes)
We used AI captcha solving in 2020 through XEvil. We hosted XEvil on a server and were generating millions of recaptcha tokens 24/7 which we then used when a restock came in to reserve the sneakers and generate the accounts.
We then had a raffle discord bot that lasted about 15 seconds, you could react to the cart and everyone that reacted would be entered into a raffle, if you won you would be DM'd an email and password to access the account with the sneakers carted.
I'm really shocked it wasn't used more, an amazing piece of software


The first bypass I found that got me started in Sneakers and bypass hunting was for off white prestos on Solebox. I was in a free cookgroup ran by @rycao18.
At the time I was programming in PHP and I saw a bug that affected a website I built. If didn't add the code "die();" after a location redirect it would attach the location header and the browser would redirect, but the code underneath would still execute if you made your browser ignore the redirect (or used something like curl)
So when I tested this on the Solebox product page it worked, I would not get redirected to the queue. I downloaded the source code and then hosted this page on a server and shared the link and watched people absolutely cook these prestos without having to go through the queue.
In hindsight, I could have just done add to cart links since what was really unprotected was the carting endpoint (No queue token was being sent/enforced) but this was my entrance into sneaker twitter and later starting Express Notify and finding many more bypasses

