




What an event. Massive thanks to the @zdi team for running this year's #P2Otokyo . And big shout out to @fluoroacetate for a seriously impressive set of submissions!
trotmaster retweeted
#Pwn2Own Tokyo is underway! The contest order has been decided via random drawing. Our program starts with @fluoroacetate targeting the #Xiaomi Mi6 with an NFC exploit. See the full schedule and updated results at bit.ly/2RQyUdT. #P2OTokyo

trotmaster retweeted
The drawing to determine the order of attempts will be at 9am tomorrow with the first attempt coming at 9:30. Until then, enjoy this preview of the Master of Pwn jackets.

Using @intel Remote Web Console? Time to patch! intel.com/content/www/us/en/…

trotmaster retweeted

Project Zero blog: "OATmeal on the Universal Cereal Bus: Exploiting Android phones over USB" by @tehjh - googleprojectzero.blogspot.c…

trotmaster retweeted
Announcing #Pwn2Own Tokyo 2018. This year, we bring #IoT devices along with phones as targets. Over $500,000 USD available in cash and prizes. Get all the details here: bit.ly/2oF20R6. See you in Tokyo! #P2OTokyo

trotmaster retweeted
#DNSRebinding isn't just for owning your router, it's also for owning your #AWS #cloud deployments, @alxk_mwr pops headless analytics services labs.mwrinfosecurity.com/blo…


trotmaster retweeted

📝 New post! I stumbled across a serious browser security bug & I can finally talk about it. The post covers:
➡️ An exciting new logo.
➡️ Range requests.
➡️ "No-cors" requests.
➡️ Sneaking past origin security.
➡️ The importance of standards.
jakearchibald.com/2018/i-dis…

trotmaster retweeted

A very warm welcome to F-Secure @mwrinfosecurity! F-Secure takes a big step towards cyber security leadership by acquiring MWR InfoSecurity press.f-secure.com/2018/06/1…

trotmaster retweeted
Last batch of bugs now patched from Mobile Pwn2own 2017 for the Huawei Mate 9 Pro: huawei.com/en/psirt/security…. Tech whitepaper to follow later in the week #pwn2own
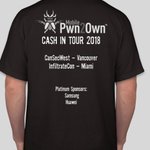
This year at @InfiltrateCon we're being honest, both with our exact methodology for pwn2own, and with our tour T-shirts ;)

trotmaster retweeted

At #CYBERUK18 next Tuesday? Our very own Robert Miller and Georgi Geshev talk vulnerabilities and automating the research process to make efficiency savings [14:50 - Exchange Auditorium] | #infosec #vuln xitter.cf/CYBERUKevents/status/9…

CYBERUK In Practice Track 1: Vulnerabilities and Bug Hunting #CYBERUK18
ncsc.gov.uk/blog-post/cyberu…

Remote keystroke injection in Intel's Remote Keyboard application. Product is discontinued, so remember to uninstall! security-center.intel.com/ad…
trotmaster retweeted

Exploring Qualcomm Baseband via ModKit
#MobileSecurity #AndroidSecurity
[SLIDES] #cansecwest2018
cansecwest.com/slides/2018/E…
