
Dad 👶👱♂️, engineer👨💻⚒, fixed wheel cyclist 🚲, Australian 🌞🍻 immigrant in Germany 🌦🍺. My partner @HannahNeumeyer 😘 does good work for society 👏.
Berlin, Germany
Joined July 2007
- Tweets11.5K
- Following308
- Followers400
- Likes1.4K




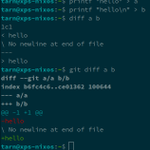


It might not be a waste of time if anyone ever needs needs to understand/revert the changes. It's not fun finding the commit that caused an issue and the commit message is twenty commit messages concatenated by a squash.
You receive the headers of the response first, after negotiating TLS and a HTTP protocol. In HTTP/1.1 the headers might specify an encoding like chunked for the body. In HTTP/2 the body is sent in one of more subsequent frames. The fetch API exposes the body as a ReadableStream.
Many shells support the fc command which opens the previous command your default editor and runs the modified command.
I wrote a couple of posts about a private PKI (tarnbarford.net/journal/simp…) and securing TCP sockets with TLS and peer authentication (tarnbarford.net/journal/secu…).
This isn't helpful. You used "we" too and in your anecdote from more than two decades ago, years before git was even released, you don't specify the important thing you released.
I can't speak for the parent but "We release multiple times a week" doesn't necessarily mean that every developer or team is releasing at that frequency.
Apparently it's possible to brute force with the public record of a transaction made with the wallet and a couple of days processing on a standard gaming PC.
I was expecting it to be some impressive hack exploiting the Mersenne Twister PRNG by somehow finding enough values in the sequence reduce the keyspace a bit.
This is so wild, the bx tool generates 24 word mnemonic pass phrases intended to be used for bitcoin wallets but it generates at most 2^32 unique phrases.
milksad.info/
Hey. I'll be in Melbourne in January and I'd love to catch up with you and others from those Alt.NET days.
htmx is the hero we don't deserve 😭


Yeah, that's true it's not just C#/.NET. Now you mention it, I have done some work on a project using Spring Boot which uses DI for everything.
I'm quite happy I haven't had to deal with a dependency injection framework in probably a decade. Is this still quite common in C# projects?
Not a security expert, but I still do. Some systems, like Elasticsearch, also make it harder not to use TLS. Keen to see the other replies.

