

security researcher
Joined November 2020
- Tweets2.5K
- Following591
- Followers47
- Likes3.2K

SweetBlue👥 retweeted
Transition from vulpocalypse to breachpocalypse is here. IR firms are saturated & turning away work. Now one hacker unleashed AI agents on 1,200+ websites, compromising 100+ for ~$5,000 in tokens. $50 per hack. Agents won and compromised targets. reuters.com/legal/government…

SweetBlue👥 retweeted

🚨NEW INVESTIGATION: University of Belgrade Rector who resisted crackdown on students was hacked with zero-click Pegasus.
Authorities raided his offices in March.
Serbia's snap elections are 6 days away.
There are more targets 1/
With @ShareConference citizenlab.ca/research/pegas…


SweetBlue👥 retweeted
NEW @citizenlab report (in collaboration with The Share Foundation)
We find more cases of Pro-Democracy figures in Serbia 🇷🇸 targeted with NSO Group's Pegasus spyware
citizenlab.ca/research/pegas…🇷🇸🇷🇸


SweetBlue👥 retweeted

Last year, @amnesty revealed technical evidence of spyware firms like Intellexa developing tools for zero-click infection through online ads.
We warned of a dangerous new threat to civil society. Now @citizenlab has caught devices at Al Jazeera being hacked via malicious ads. 🧵


SweetBlue👥 retweeted

Thread 🧵
1/ NEW REPORT: Billions of advertising auctions determine in real time which ads we see on websites and in apps every day. Our latest research shows how the same data fueling this advertising ecosystem is being used to profile millions of users and silently infect targets with zero-click mercenary spyware, a novel attack technique we call "Adfection.”
Read the report: citizenlab.ca/research/how-d…

SweetBlue👥 retweeted
NEW @citizenlab report We uncovered an Israeli firm using online ads to run vast spy operation
This is the first-ever public confirmation of zero-click mercenary spyware delivered via targeted ads.
45 devices at @AJEnglish confirmed infected
citizenlab.ca/research/how-d…
SweetBlue👥 retweeted
Despite claims by Trezor today that none of its crypto devices have been compromised - unlike the devices of Ledger, its competitor - hardware hacker @joegrand says he found implants in two Trezor devices and reported this to Trezor in August. My story: zetter-zeroday.com/trezor-wa…

SweetBlue👥 retweeted

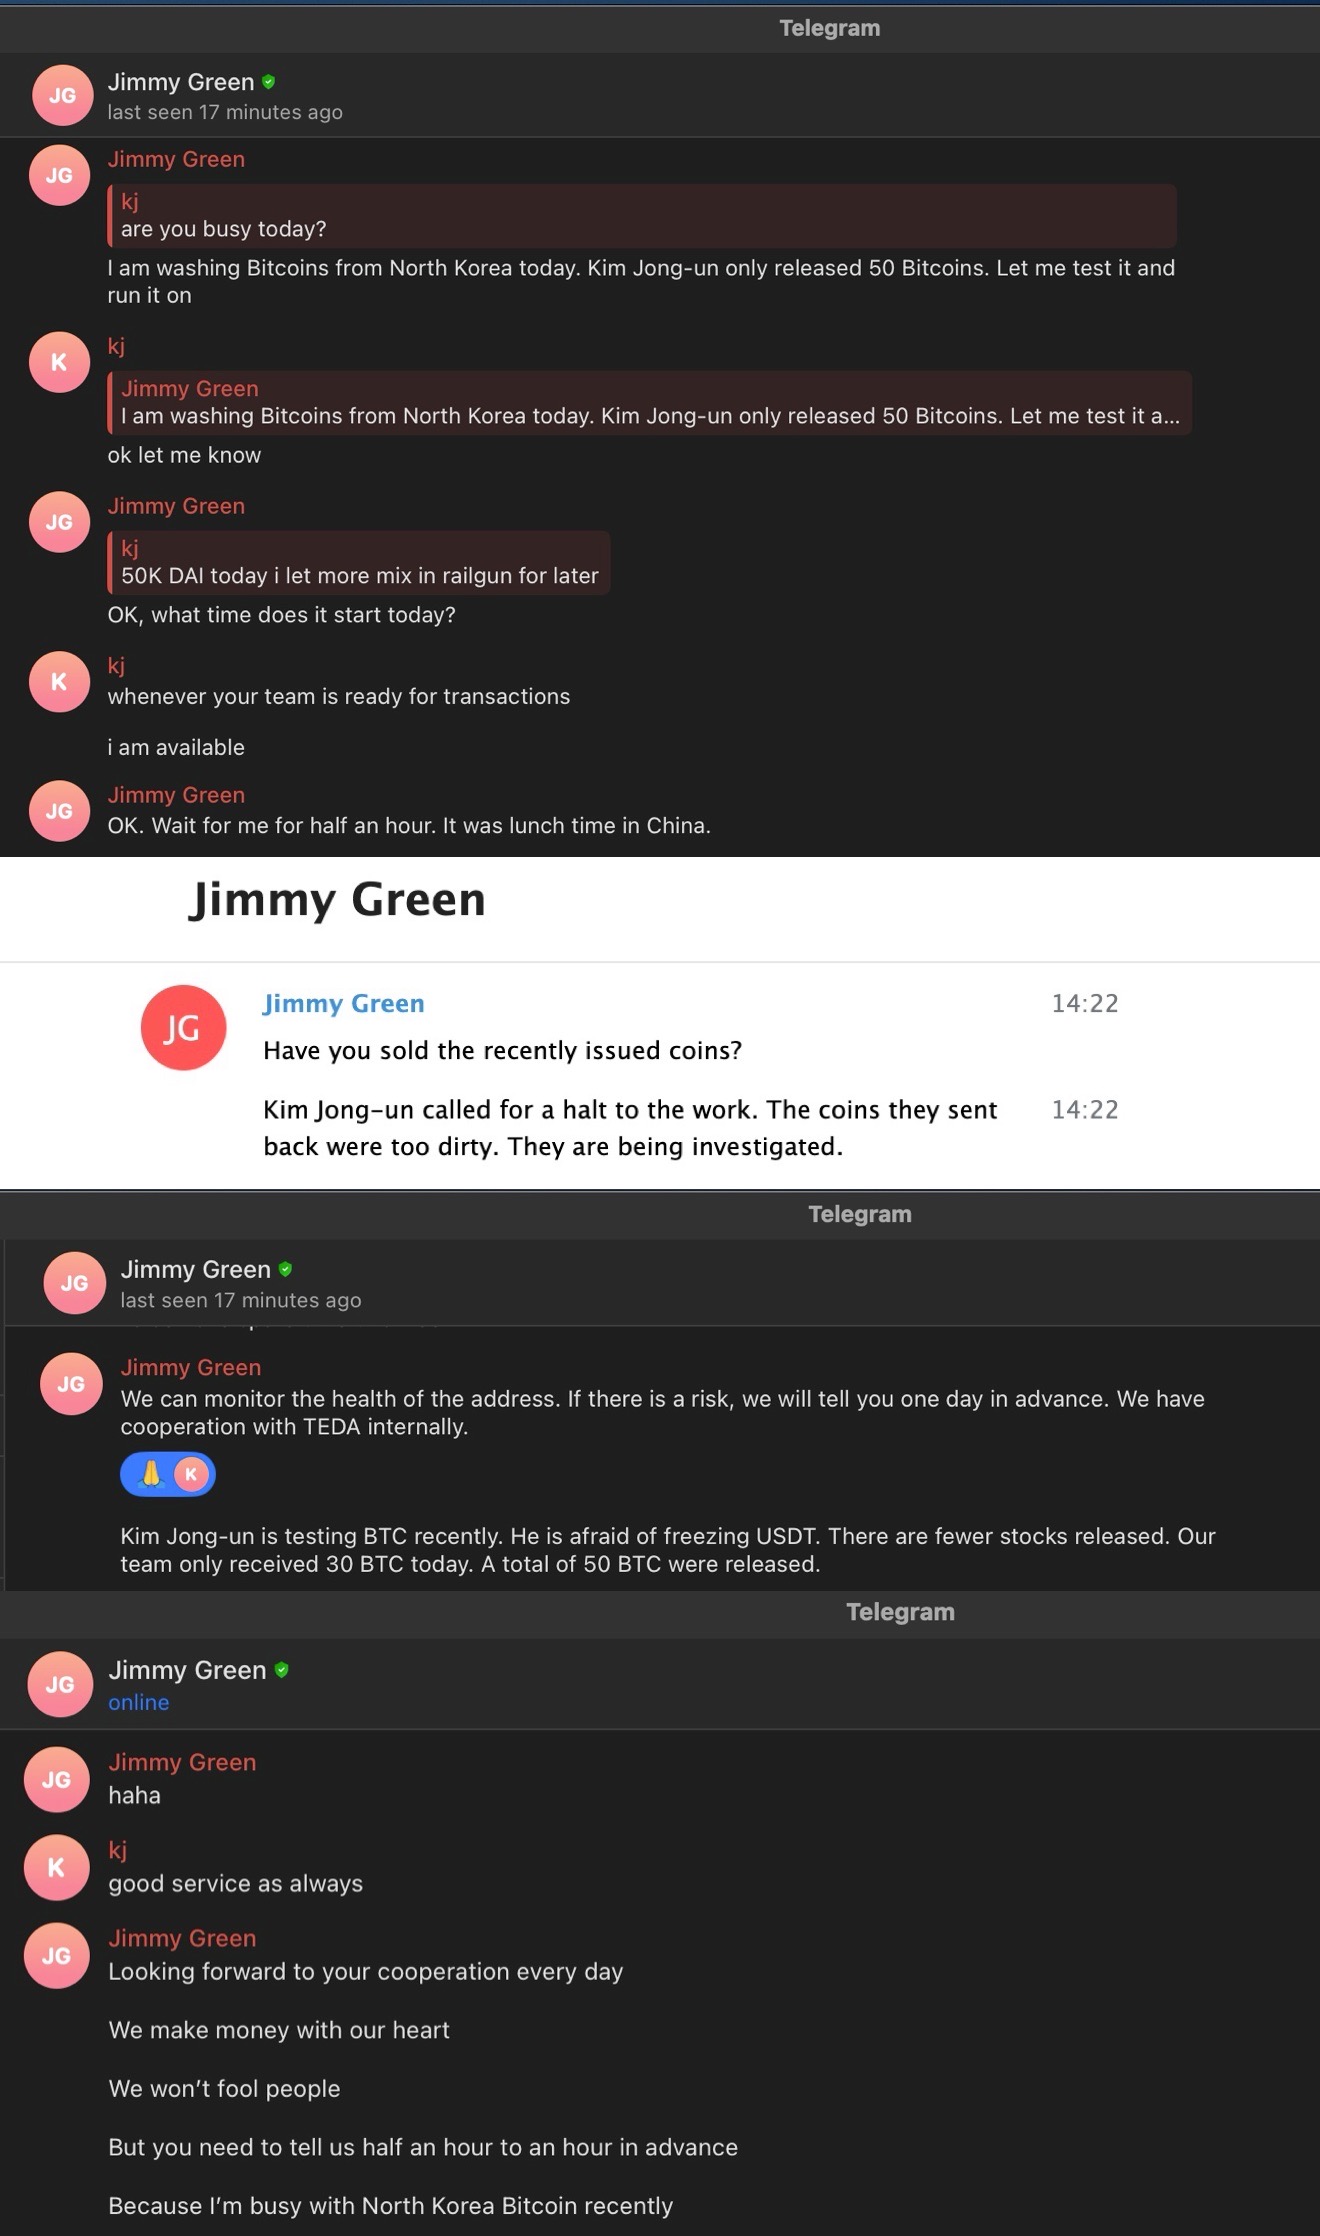
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.


SweetBlue👥 retweeted
UPDATE: he was hacked with Pegasus while investigating spyware.
He's just sued NSO Group's executives.
We @citizenlab found MEP @SteliosKoul's phone was hacked during particularly significant periods of the EU's PEGA committe to investigte spyware abuses.
Case adds to NSO Group's growing legal troubles as spyware victims from around the world seek legal remedies.
tovima.com/society/kouloglou…


BREAKING: 🇪🇺EU lawmaker investigating spyware abuses was hacked with Pegasus.
Infected during key moments of the PEGA committee.
More proof that it's spyware open season in Europe.. yet nothing is being done 1/
Our @citizenlab forensic investigation: citizenlab.ca/research/membe…


SweetBlue👥 retweeted

A vulnerability can be patched and still be a zero-day for millions of users. Volexity co-founder and president @stevenadair will deliver the keynote at our upcoming Volexity Cyber Sessions in Amsterdam (October 29) on multiple cases from September 2026, when Volexity uncovered three distinct Chinese threat actors exploiting Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) vulnerabilities. The Chrome vulnerabilities had already been fixed upstream in Chromium—but hadn't yet reached a public Chrome release—potentially allowing the threat actors to compromise fully up-to-date users. The identical exploit code reused across otherwise unrelated operations points to a shared supplier.
Steven will reconstruct these campaigns, tracing the exploit from upstream patch to active deployment and examining the evidence linking the operators despite their different infrastructure, targeting, and tooling, including a false-flag campaign designed to pin the blame on a Russian threat actor. The talk covers what this reveals about exploit supply chains, the risks created by the patch gap, and the attribution challenges posed when capabilities are shared between threat actors.
Seating is limited. Register now to secure your spot: luma.com/0qtkw49c
#dfir #threatintel

SweetBlue👥 retweeted
Thread 🧵
1/ 🚨 NEW RESEARCH: We identified a training program provided to government employees in Angola by the Israeli influence-for-hire company BlackCore.
Full report: citizenlab.ca/research/black…


SweetBlue👥 retweeted

We're publishing our most detailed threat intelligence report to date.
It covers how people tried to misuse Claude—for cyberattacks, influence operations, surveillance, biology, and building weapons—and how we found and stopped them.
We disrupted every operation in the report, and used the lessons from them to strengthen our safeguards. Where appropriate, we also shared what we found with authorities and other AI companies.
These cases are not typical: we’re highlighting some of the most sophisticated misuse we’ve seen. But they’re especially important to discuss, because they show us where AI misuse is headed, where our safeguards work, and where they need to improve.
We’re publishing this report so others can spot the same activity on their own platforms, and so we can give the public a clearer view of how emerging threats develop.
Read the report: anthropic.com/threat-intelli…

SweetBlue👥 retweeted

As you watch everyone losing their minds over this alarmist nonsense, hold onto this 9 year old talk.
idlewords.com/talks/superint…
youtube.com/watch?v=kErHiET5…
SweetBlue👥 retweeted

On November 2nd 2026 our public Encrypted DNS servers will be shut down.
This does not impact customers of our VPN if DNS content blockers are used.
Read more here: mullvad.net/blog/shutting-do…

SweetBlue👥 retweeted
1/ NEW: an investigation by our collaborator @shareconference reveals widespread spyware targeting Serbia's pro-democracy student movement.
The Citizen Lab can confirm that an iPhone belonging to a student was infected with Pegasus spyware in a zero-click attack over iMessage.
This is the most recent public Pegasus case, and it comes amidst a critical series of elections in Serbia 1/
Read more: sharefoundation.info/en/shar…

SweetBlue👥 retweeted

More than just a GRU Hacker School💻
DTI researchers analyzed the internal documents leaked from a long-term training pipeline for Russian military intelligence and cyber operations.
Read our investigation: dti.domaintools.com/research…
#Cybersecurity #ThreatIntel #Russia
