

Security research for Web3 & DeFi | Lido, Curve, Fluid, Symbiotic, Valantis, Yield Basis, Vyper | Top in Paradigm CTF | ICPC |
Blockchain
Joined May 2022
- Tweets788
- Following89
- Followers1.8K
- Likes156





Pinned Tweet
Statemind. DeFi Security Audit & Research.
The protocols we partner with ship and scale.
Contact: statemind.io/request
Public Audits: github.com/statemindio/publi…

Glad to be one of the security providers on Areta Marketplace. Great to see it live on @Aptos, congrats @0xboo & team 👏

1/ The Aptos Security Marketplace from Areta Market is now live on @Aptos!
Proven across 10 ecosystems, 2k+ quotes submitted, and up to 30% average cost savings per audit. Alongside the Aptos Foundation, we’re excited to make top-tier security accessible to Aptos builders.
→ aptos.areta.market


At Statemind, manual audits are the heart of what we do. We create tools that support the work, widen coverage, and strengthen the audits.
That's why @forefy's autonomous-audit benchmark was a nice point of reference for us. Statemind's agent ranked first of 14, a sign that we're building these tools the right way.

SEAL Certifications are now open, a framework for protocol operational security across six domains: Multisig Ops, Treasury Ops, Incident Response, DNS & Registrar, DevOps & Infrastructure, Identity & Accounts.
Statemind is in the accreditation process. Come talk to us.


Off-chain Python operator. Not the contracts.
During an internal review of @stakewise_io, our researcher @melemmeme found a vulnerability that could let anyone freeze automated withdrawals and consolidations. No exploit, no special access, just spam.
We flagged it. They fixed it fast.
If a project has off-chain and on-chain components connected, errors can occur in any part and attack vectors become more complex, each layer interfering with the other.
Writeup: gist.github.com/Leminkay/9e9…
Fix: github.com/stakewise/v3-oper…

If your protocol has off-chain dependencies, it's not DeFi. It's CeDeFi.
Echo proved it: one compromised admin key, $76M minted from nothing. The contracts worked as intended.
CeDeFi needs security at every layer:
→ Key management & policies
→ Backend audit
→ Infrastructure / opsec
→ Smart contract audit
Only one of these has become an industry standard. That needs to change.

Bitcoin DeFi Platform Echo Protocol Hit By $76M Monad Exploit
decrypt.co/368315/bitcoin-de…
Permissionless MetaVault creation is a meaningful upgrade for the @stakewise_io Happy to contribute to the security side. 🔒

@stakewise_io has hit quorum on two votes in parallel: opening MetaVault creation to anyone, and making it 5x more expensive to push proposals into a binding vote.
The first lets anyone spin up a MetaVault (a diversified ETH staking position that mints $osETH) without DAO approval. New factory contracts audited by @statemindio.
The second raises the $SWISE bond required to advance a proposal through StakeWise's escalation game (the security gate against low-quality or malicious proposals reaching a vote) from 200,000 to 1,000,000 $SWISE.
Author @kiriyha1: "200,000 SWISE now costs less than $1,000, putting the protocol at additional risk of malicious votes being tried because they're cheap to attempt."
So far unanimous on each: 3 voters, 5,706,939 $SWISE in favor, zero against (190% of quorum required). Voting closes May 11th at 1pm UTC.
Proposals:
1. [SWIP-39] Upgrade MetaVault Factory to Enable Permissionless MetaVaults: snapshot.box/#/s:stakewise.e…
2. [SWIP-40] Increase Bond Requirement For Initiating Escalation Game In Governance & Remove Manifold Relay: snapshot.box/#/s:stakewise.e…


New from Statemind: Audit of @stakewise_io Core V3. The vault-based liquid staking protocol powering osETH and osGNO. Operator model, meta vaults, overcollateralization math.
Report → github.com/statemindio/publi…

Proud to be among the trusted providers in this.
$1M in audit subsidies for builders on Ethereum.
Read this and apply 👇
2/ The Ethereum Security Subsidy Program is proud to be launching with access to 20+ of the leading audit providers active in the Ethereum ecosystem:
@AdevarLabs, @bailsecurity, @BlockSecTeam, @Certora, @chain_security, @cyfrin, @dedaub, @GuardianAudits, @hackenclub, @HackenProof, @Hashlock_, @hexens, @immunefi, @LeastAuthority, @lethalspoons, @NethermindSec, @Quantstamp, @QuillAudits_AI, @rv_inc, @SecurityOak, @sherlockdefi, @spearbit, @statemindio, @zellic_io, and @zokyo_io.
These top-tier security providers make the program possible through their commitment to support Ethereum mainnet.

New from Statemind: a full implementation walkthrough of @yieldbasis . From the leveraged liquidity math behind LEVAMM to deposits, withdrawals, fee splits, and the price oracle migration. All the way down to the Vyper code.
Full breakdown → statemind.io/blog/how-yieldb…

New from Statemind: we dove deep into @CurveFinance's Donations mechanism for CryptoPool. How pools can be "refueled" when fees aren't enough for repegs, with built-in safety considerations.
Full breakdown → statemind.io/blog/curve-cryp…

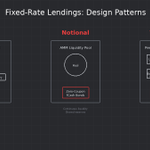
We’ve been researching fixed-rate lendings in DeFi.
@pendle_fi , @NotionalFinance, @TermMaxFi: mechanics and design trade-offs, compared side by side. Thanks to the teams for feedback and to @dsstore345 for the research.
For a thoughtful weekend deep dive
statemind.io/blog/fixed-rate…

Statemind retweeted

Big thanks to @statemindio for the great CTF challenges🫡
CTFs are one of my favorite ways to learn something new, explore edge cases, and sharpen security thinking in practice. Always fun and useful.


Ready to feel the same?
Get on the interest list for the next Statemind Blockchain Security Fellowship cohort → statemind.io/fellowship
📽️ Kudos to Ilya @ilya_komar0ff for this masterpiece
The doors to Statemind Fellowship are opening again 🚀
✓ Ace our entrance challenge
✓ Dive into a month-long training program with expert guidance
✓ Battle-test your skills in our handcrafted CTF
✓ Get a chance to join our team
Apply: statemind.io/fellowship
