

Founder & CEO @ Cinta Infinita ;-) Fan de la Encarta 98 y de la Menta Granizada.
Buenos Aires
Joined May 2010
- Tweets11K
- Following5K
- Followers2.8K
- Likes21.2K





👾Moebius retweeted

Quitar un parámetro. Modificar un header. Reenviar el pedido HTTP. Comparar respuestas. Y volver a empezar. 🔁
En Bug Bounty y Pentesting, esas pequeñas pruebas repetitivas consumen tiempo. En mi nueva nota cuento cómo estoy incorporando @PortSwigger Burp AT a mi workflow para delegar parte de ese trabajo.
Como @Burp_Suite Ambassador, me interesa compartir cómo podemos aprovechar estas herramientas en nuestra forma de investigar.
📝 Cómo uso Burp AT para automatizar tareas de testing manual 👉 lnkd.in/dwkmKuja
#BurpSuite #BugBounty #Pentesting

ALT Burp Suite AT
👾Moebius retweeted

La IA disparó una enorme cantidad de reportes y está alterando el ecosistema del bug bounty.
@AndresRiancho, de Vercel, y @soyel_mago, fundador de la BB Village, cuentan cómo es estar de los dos lados del mostrador (y un RCE en Linux 🐧)
En clarín 🗞️
clarin.com/informacion-gener…

👾Moebius retweeted

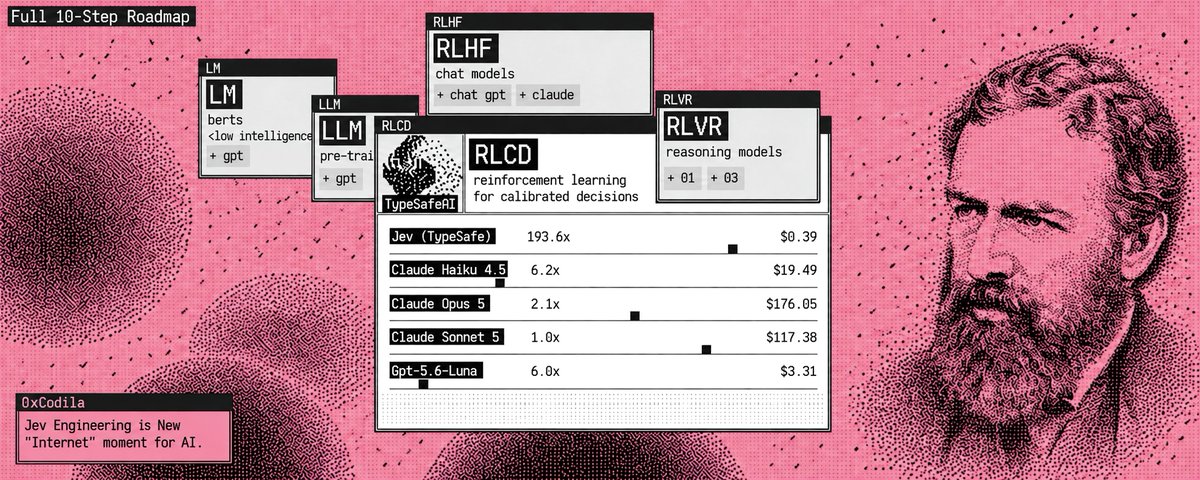
Jev is "Internet" moment for AI: up to 193x faster and 444x cheaper in tests with Claude Fable 5.1 and GPT-6 Astra
Whar is Jev, how to use and unlock its real 100х advantage in my 10-page research:
step 1 → meet Jev: LLM writes, agents act, Jev chooses the next move - split intelligence from execution
step 2 → turn every agent fork into three primitives: Choice selects one route, Score measures a defined scale, Noul returns the probability of yes
step 3 → build before getting access: use TypeSafe’s official adapter with OpenAI, Anthropic or xAI, then swap in Jev without rebuilding the graph
step 4 → setup first Jev: one state, three parallel decisions, risk-based thresholds and a real queue your agents can execute
step 5 → batch decisions instead of serializing them: 13 questions in one call ran 10x faster and 12.2x cheaper than 13 sequential calls
step 6 → place Jev at every bounded fork: choose the agent, model, tool, browser action or human escalation, then read fresh state
step 7 → benchmark the entire loop: Browser Use hit Google Flights in 7.1s, Every ran 777 checks in under 0.7s, Mobile Jev completed 9 actions in 21s
step 8 → rank wide, read narrow: Jev cut wrong Hermes skill loads from 16.8% to 7.3% and pushed legal Top-10 retrieval from 38% to 62%
step 9 → steal a system, not a prompt: Chief of Staff, model router, inbox firewall, research feed, browser controller and safety gate all use State → Questions → Action → Verify
step 10 → keep Jev out of math, writing and irreversible execution: code computes, LLMs create, Jev decides, fresh state proves the result
the result: one slow, expensive agent becomes an always-on decision machine that routes, scores and escalates in milliseconds
Copy the complete 10-page Jev blueprint - then read full 10-step roadmap below ↓


👾Moebius retweeted
Tenemos tremenda previa para la @ekoparty de este año 👀
Se viene el @metabugbounty Live Hacking Event 🔥
📅 5 de octubre
📍 Buenos Aires
📝 Pre-Inscripción:
docs.google.com/forms/d/e/1F…

👾Moebius retweeted
🎩 Hackers, magia y Las Vegas 💻🎰
Nuevo VLOG desde Vegas: Black Hat USA 2026, BSides Las Vegas y Magic Live.
Hacking, Bug Bounty, magia y mi paso por Black Hat junto a los amigos de @PortSwigger.
▶️ youtu.be/tBeZmMyyNG4


👾Moebius retweeted
“Certighost is an Active Directory Certificate Services (AD CS) vulnerability that allowed a low-privileged domain user to impersonate a Domain Controller and achieve domain compromise in the tested AD CS configuration. The issue was addressed in the July 2026 security updates.”

Happy to share a technical analysis by @h0j3n on our recent CVE-2026-54121 a.k.a Certighost. glhf🔥
Technical analysis: gist.github.com/H0j3n/a5ef26…
POC: github.com/aniqfakhrul/CVE-2…


👾Moebius retweeted

The @OWASP_AISVS 1.0 is now released and live!
github.com/OWASP/AISVS/blob/…
cc @ottosulin @ricokomenda Russ Memisyazici and Raza Sharif

👾Moebius retweeted
Bug Bounty Village @ @ekoparty 2026 is now looking for sponsors!
With the support of our sponsors, we're able to keep growing the Village year after year, bringing talks, challenges, networking opportunities, swag, prizes, and unforgettable experiences to the bug bounty community.
If your company wants to connect with hundreds of security researchers, bug bounty hunters, and offensive security professionals from across LATAM and beyond, we'd love to talk.
📩 [email protected]
#BugBounty #CyberSecurity #InfoSec #Ekoparty #BugBountyVillage #HackerCommunity

👾Moebius retweeted
Nos fuimos unos días a vivir la primer edición de @ekoparty Miami junto a @BugBountyArg y documenté todo en un VLOG. Espero que les guste :)
youtu.be/ZRFrmwk_0MU

👾Moebius retweeted
Just successfully exploited my first web race condition using the techniques described by @albino_wax in Smashing the State Machine. With a bit of AI, I identified a race in an authorization check where shared state between concurrent requests could be overwritten by a higher-privileged user. By triggering the race condition during authorization validation, I was able to bypass access controls and retrieve data belonging to users from other organizations.
A great reminder that sometimes the bug isn't in the authorization logic itself, but in when that logic executes. Thanks @albinowax for the excellent research and methodology.

I'm thrilled to announce "Smashing the State Machine: the True Potential of Web Race Conditions" will premiere at @BlackHatEvents' #BHUSA this August! Looking forward to sharing some exploits that blew my mind!
blackhat.com/us-23/briefings…


👾Moebius retweeted

Meet the Burp Ambassadors: @soyelmago 🇦🇷
Alan Levy is a Buenos Aires-based security consultant, content creator, and founder of @BugBountyArg.
He’s also behind LATAM’s first online bug bounty conference: BountyMagicCon.
#BurpAmbassador #BurpSuite

👾Moebius retweeted
Everything in the Proxmark3 Iceman firmware.
Every iCLASS, SEOS, Mifare, UL-AES, FeliCa update.
Every late night debugging session.
None of it is sponsored. All of it is open source.
If it has saved you time or taught you something, consider buying me a coffee.
Patreon this week: promo code 82409 for a discount.
patreon.com/iceman1001
#Proxmark3 #RFID #OpenSource #InfoSec

👾Moebius retweeted
When I started seriously getting into RFID security, the information landscape was a mess.
Forum threads from 2009 with broken links. Research papers behind paywalls. Knowledge sitting in private Slack channels and IRC rooms that you needed to already know someone to access. The people who knew things weren't being gatekeepers intentionally, the tooling just hadn't created a natural gathering point yet.
Then there was the Proxmark forum, the center of it all for a decade.
Not https, and overrun with spam. Haters flooded it with spam.
That's part of why the Discord server exists.
It's now the largest RFID hacking community online with members from 40+ countries, spanning everyone from published researchers presenting at DEF CON and Black Hat to people who received their first Proxmark3 last week and aren't sure which end to point at the card.
The mix is deliberate. Beginners ask the questions that experts stopped asking years ago. Those questions are often the most interesting ones. "Why does this card respond to `lf search` but not `hf search`?" leads to a surprisingly fun conversation about frequency, modulation, and why the protocol landscape is the way it is.
If you're into RFID, NFC, access control security, or hardware hacking in general, the door is open.
discord.gg/iceman
#RFID #NFC #CyberSecurity #InfoSec #HardwareSecurity #Community #Proxmark3
youtube.com/@iceman1001
github.com/RfidResearchGroup…

👾Moebius retweeted
"iClass is secure"
Sure. Until the firmware was extracted and master keys leaked.
Then: "use iClass SE"
Until the crypto was reversed, tear-off attacks published, and SAM support.
Then: "use SEOS"
Until the SAM got hacked and SAM support landed in Flipper
Every proprietary RFID system follows the same arc.
Obscurity. Breach. Patch. Repeat.
Open standards with real crypto exist.
Nobody wants to replace the hardware.
#iClass #HID #SEOS #RFID #Proxmark3 #PhysicalSecurity
github.com/RfidResearchGroup…
xitter.cf/herrmann1001


