




Pinned Tweet
𝗔𝗹𝗲𝗿𝘁𝗮 🚨 | Campaña de #Phishing para @BancoEstado 🇨🇱, solicitando credenciales, coordenadas, datos de tarjeta y clave de cajero 🤯. Llamativo lo "𝗽𝗲𝗿𝘀𝗼𝗻𝗮𝗹𝗶𝘇𝗮𝗱𝗼" al usar nombre del usuario asociado al RUT y lo interactiva de la interfaz. #PhishingChile

F retweeted

ShinyHunters hacks Clop leak site, threatens to extort ransomware gang
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…

F retweeted

‼️ More than 100,000 WordPress sites have been compromised after an attacker exploited a hardcoded Cloudflare API key in marketing company Brevo's source code. The sites are now serving a ClickFix scam.
The API key gave the attacker full account permissions, and they've used it to rewrite the JavaScript that the email-marketing firm's customers embed on their own sites.
Visitors got a fake Cloudflare captcha telling them to paste a command into the Windows Run box or a terminal, leading to malware infection.
Brevo says the key is now out of its source code, replaced by short-lived tokens with limited permissions, and that credentials are no longer kept in source or config files.
Site owners got something extra as well: if the admin happened to be logged into WordPress when the page loaded, the script quietly installed a plugin. Sansec couldn't obtain a copy and suspects a backdoor.
Brevo lists eBay, Louis Vuitton, Michelin and Amnesty International as its customers.


CVE-2026-87796: Multi Uploader for Gravity Forms, unauthenticated RCE .. aquí el write Up 🔥abraxaslabs.tech/research/cv…

fr3sh, h0t 0day s3rv3d!!! within 8 hours of CVE registration. no patch yet... CVE-2026-87796 - Multi Uploader for Gravity Forms <= 1.1.9 (CRITICAL 9.8) Unauthorized RCE
github.com/abraxas/CVE-2026-…
cve.org/CVERecord?id=CVE-202…

🚨 WordPress Security Alert | Click2Shell
Vulnerabilidad permite forzar la instalación silenciosa de un tema mediante un enlace manipulado, con un admin auth como objetivo. Podría derivar en RCE. 🔐
📌 Solucionado en: WP 7.1.1 [17/09/2026]
#WordPress #WordpressSecurity

‼️ WARNING - New WordPress "Click2Shell" vulnerability can force a silent theme install from a crafted link.
Researchers chained the flaw with a separate theme bug to execute code on the server.
Read details here → thehackernews.com/2026/09/ne…
F retweeted

🚨 Attackers are exploiting a critical WooCommerce Wholesale Lead Capture flaw to plant PHP web shells.
Wordfence has blocked over 100,000 exploit attempts since June against CVE-2026-27540, which affects versions through 2.0.3.1.
Read: thehackernews.com/2026/09/at…


Esto me hace recordar que yo tenía un amiguito que tenía su empresa de hosting. Y un día desapareció de la faz de la tierra, y con el hosting. Que será del buen litov ? 🤔 De eso ya han pasado 2 años.

ALV, menos mal. Yo pensé que ya habían desaparecido todos los sitios. 🫠
This quoted post is unavailable.
Lo de las skill en Claude es otra wea. Lo que me tomaba antes a máxima velocidad y concentración: 3 días. Hoy toma un par de horas uwu
F retweeted

Google is changing how some search results work.
Some results now route through google.com/goto?url= redirects, hiding the destination in an encoded URL.
Great for fighting scrapers. Less great for people checking where a link goes before clicking.
malwarebytes.com/blog/news/2…
Tenía una sola misión: editar una descripción antes de dar de alta un sitio en Google. Y no lo hice y ya se indexó 🫠
¿Que tan difícil será realmente cumplir para las pymes la ley de protección de datos en chile? 🤷 Será que todos tendrán invertir en un tercero para que puedan cumplirlo?
F retweeted

🔐 Cada 32 segundos, una web WordPress recibe un intento de ataque
La mayoría son ataques automatizados que van “probando suerte” hasta encontrar una puerta abierta.
Te contamos cómo proteger WordPress con medidas simples y que de verdad funcionan 😉👇🏽
f.mtr.cool/1ph6zojnkj

Mientras sigan vendiendo sitios creados en wordpress que después dejan abandonados: habrá trabajo en seguridad 🥹❤️
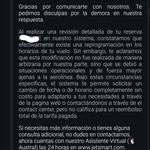
Compré un vuelvo en @VuelaJetSMART ANF-SCL para después hacer escala con otro. Cambiaron horario sin aviso, en la página sale como "no reprogramado o cancelado". No puedo reembolsar. Imposible contactar con agente, puros bots que no sirven. Levanto un reclamo y la respuesta:

Cambian el horario del vuelo, ya no me sirve, tuve que comprar otro en otra linea para no perder mi escala . Y no van a reembolsar la totalidad de la tarifa, siendo que cambiaron el itinerario, peor aún sin aviso. Que queda ahora? Reclamo en @SERNAC ? 🙃 Nefasto @VuelaJetSMART