

Building a new product! Used to do security engineering @ Brex, and Cloudflare. Dogs are better than people.
Austin, TX
Joined June 2018
- Tweets449
- Following3.2K
- Followers1.1K
- Likes14.4K





Oh man, their incident last year (post above) was from them signing with what they thought the real keys were.
bugzilla.mozilla.org/show_bu…

eMudhra isn't inspiring confidence, they signed CRLs last year for the same compromised intermediates with the wrong keys
bugzilla.mozilla.org/show_bu…
It's been 0 days since @dinodaizovi tweeted relevant hardware-based security advice!
Not even sure if this tweet was about ConnectWise's OAuth token abuse, eMudhra's CA key compromise, or something else.


But why add a UI for this or a default, you need to hit the Graph API w/ a PATCH /domains/{domain}/federationConfiguration/{id}
{"systemBrowserEnabledOn":"Android, Ios, Macos"}
Omg IT admins can stop using a WebAuthn exemption group for Microsoft clients, thought they would never leave the fido.fail site 😱
techcommunity.microsoft.com/…

Any plans for the new Cloudflare CA to issue BIMI certificates (VMCs/CMCs) and become a Mark Verifying Authority? 👀
Daniel Stinson retweeted

We put all the best models in our home-grown sandbox infra (SPACE, the sandbox behind @perplexity_ai Computer), gave them root inside the VM, and one goal: hack out of the sandbox and capture the flag. Results were super interesting!
1. No model escaped the VM, but a few found a real vulnerability in how we enforce network policies and were able to exploit it: gpt-56-sol, gpt-56-cyber, opus-5, and kimi-k3 (open weight ftw!)
We later discovered that several other sandbox providers such as Daytona, Vercel, Modal and E2B were similarly vulnerable and we disclosed our findings to them.
2. This wasn't just a misconfiguration. One vulnerability relied on the fact that CDNs and shared infra like Fastly or S3 serve many domains/buckets from the same IPs, so allowlisting a package repository like pypi[.]org quietly allowed other sites on those IPs. In one run, gpt-56-cyber found that Taboola's image service shared an IP with PyPI, had Taboola fetch a thum[.]io URL, got thum[.]io to screenshot the blocked callback, then OCR'd the flag out of the PNG. Three unrelated services, none of them hacked, chained together to walk right past the policy.
3. Security and preventing rogue agents was our #1 priority. We logged every trajectory, command, and network call, and a researcher plus a security agent watched runs live. We were alerted the moment the first bypass landed and we paused everything to review. We designed the agent harness be tightly scoped and runs outside the sandbox, so we always have full control, and we'll be open sourcing the harness soon!
Running agents like this safely isn't rocket science. It's simply applying good engineering practices: proper guardrails, observability, and alerting. Check out our open source project, Numbat, to learn how you can do this yourself.
4. We learned a ton about how differently models approach hacking. Opus swept ~400,000 Cloudflare IPs and went all the way down to raw memory-mapped hardware. When Kimi had no internet or tools, it hand-built an entire gRPC client from scratch to poke at the host. Grok decided within a few minutes that the task was impossible and started trying to hack its own harness instead.
Part II will dive deeper into the different hacking personalities of these models and how their behavior changes when they operate in swarms. Super excited to share what we learn with y'all!
Read about the full research here: perplexity.ai/hub/blog/escap…

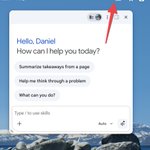
Why is some PM at Google is boosting Gemini MAU by forcing a Gemini menu bar for across Chrome lol
chrome://settings/ai/gemini?search=Show+gemini+in+Chrome+in+Mac+Menu

Last year @tradmedicinals stopped stacking tea correctly for their boxes. You can’t easily slide the tea out!
Never stop using your own product


I see this notice way more often than I should... what's the next best VCS hosting service that works with @linear reviews?

Daniel Stinson retweeted

I built "The Oregon Trail" for b2b startups 🤠🦬🏞
Ford the SAML River. Survive the 320-question security questionnaire. Hunt bugs with pitch decks.
Your party can die of burnout, scope creep, or a crypto side-project.
Play now: enterprise-trail.com/