

Secureframe is the automated compliance platform built by compliance experts. We're transforming how businesses and MSPs manage security & compliance programs.
San Francisco, CA
Joined January 2020
- Tweets1.7K
- Following150
- Followers2.2K
- Likes561

Pinned Tweet
On average, DIB contractors spend $100K–$250K+ and 6–18 months on CMMC prep. Most can't afford that.
Today, we launched Secureframe Defense to help any organization go from zero to CMMC ready in 4–8 weeks.
Learn how: secureframe.com/blog/announc…
The attacker behind Denmark’s national register breach (8.8M people) claims they got in through a vendor account with the password “123456.” Reportedly three accounts used it, admin included. Your policy is only as strong as your vendor’s: hubs.li/Q04B19y30

Attackers cranked up fridge temps at hundreds of French supermarkets and stretched defrost cycles to delay alarms. Not a DIB incident, but if a vendor can reach your plant equipment remotely, so can an attacker. Know what comes back first? hubs.li/Q04B19wJ0

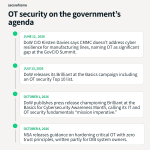
DoW opened October with a Brilliant at the Basics push covering IT and OT. Then NSA released zero trust guidance for OT, written partly for DIB owners. When the government keeps pointing at the plant floor, contractors should look too: hubs.li/Q04B19x30

Known vulns get mass-exploited in a median of five days (Verizon DBIR). Most compliance programs still check controls once a year. My colleague Marc Rubbinaccio told @uctodaynews why that won't last: hubs.li/Q04zX1l30
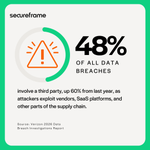
Third parties were involved in 48% of breaches this year, up 60% (Verizon). What surprised us more: only 23% of them fully fixed missing or weak MFA on their cloud accounts. Vendor risk is a remediation problem now: hubs.li/Q04z6lHs0

Cybersecurity Awareness Month exercise: run your top risk through the ALE math. A $12K/yr control that cuts expected ransomware loss from $20K to $4K a year pays for itself. Six methods to try: hubs.li/Q04z6lCY0

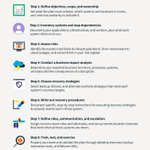
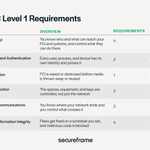
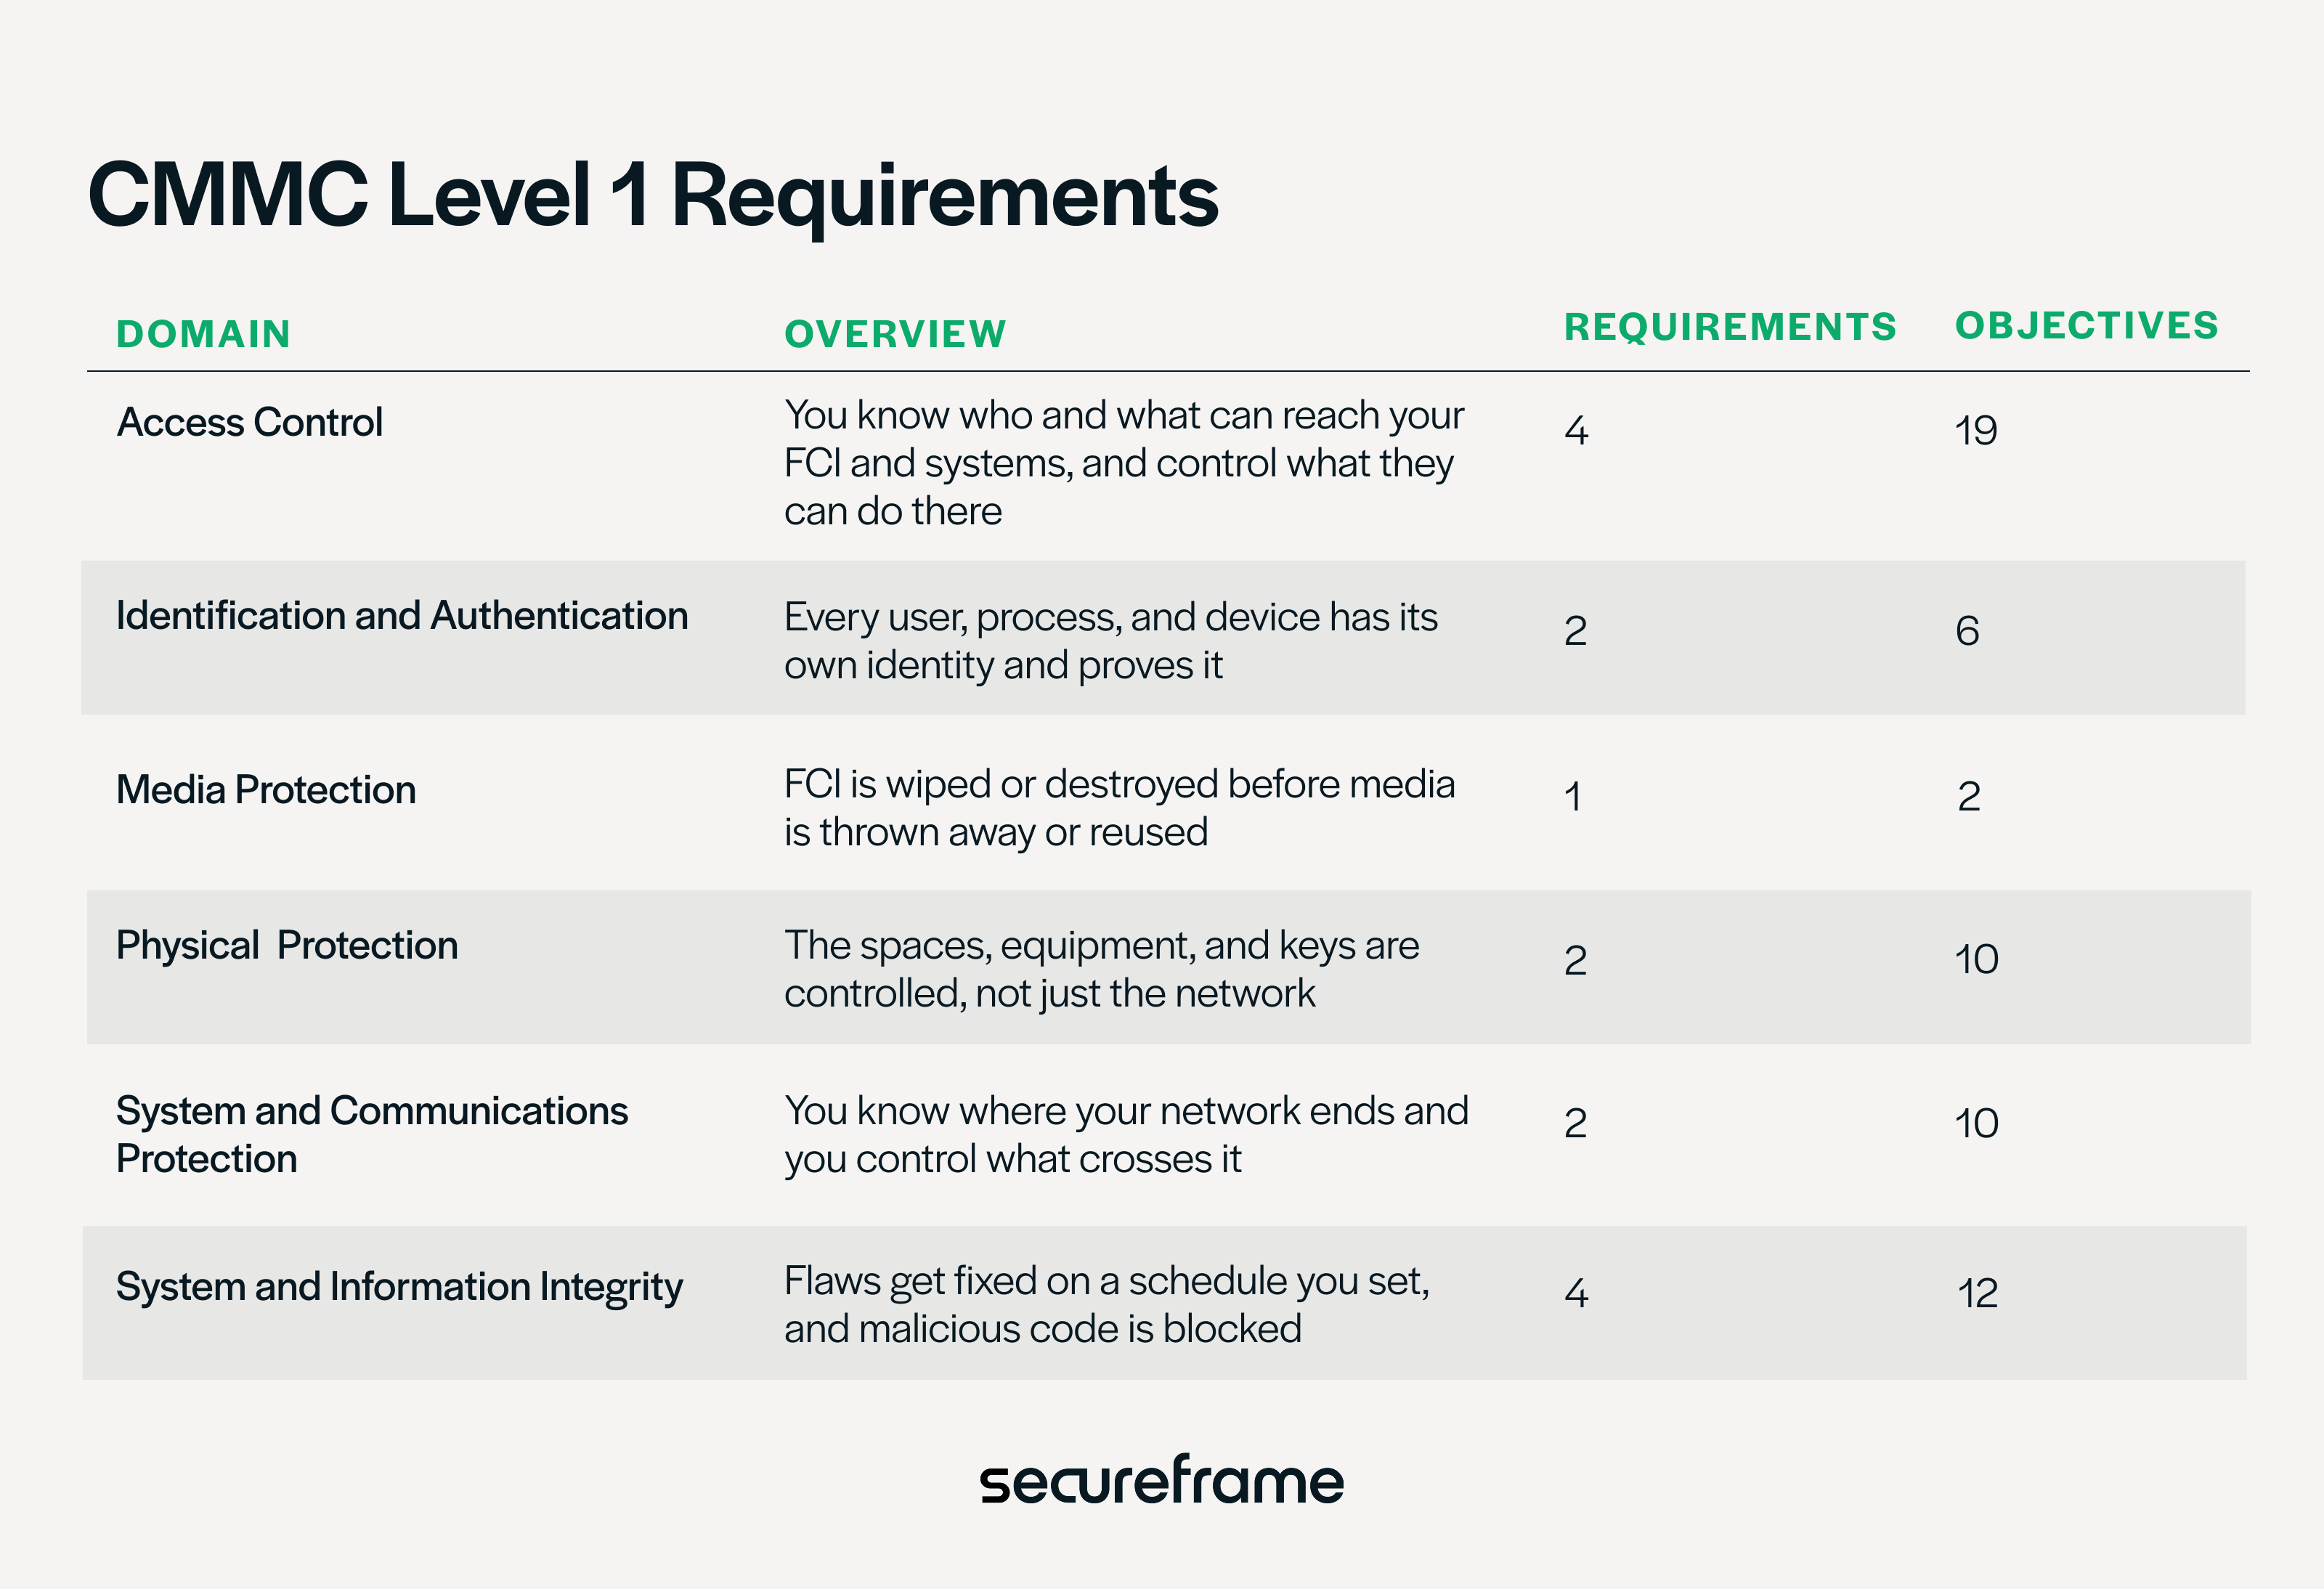
No CMMC task force report yet, but Level 1 self-assessments are still required. The catch: 15 requirements hide 59 objectives, with no partial credit and no POA&M. This guide says exactly what to do for each: hubs.li/Q04z6lGP0
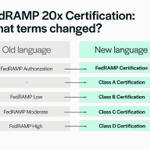
FedRAMP 20x Phase 4 comments close Friday, and the Class D pilot requirements are expected Oct 14. If the Class A to D naming still trips you up, this is the clearest breakdown I know of: hubs.li/Q04z6lKr0

Still no CMMC Reform Task Force report, but the DoW CIO keeps pointing at OT: "nowhere in CMMC was there even a mention of how to build cyber resilience for a manufacturing line." Worth getting ahead of now: hubs.li/Q04z6lJp0

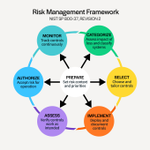
Only 30% of execs describe their risk oversight as mature (NC State and AICPA). Part of the problem is choosing from dozens of overlapping frameworks. Handy side-by-side of 10, from NIST CSF to COSO to FAIR: hubs.li/Q04yDNlH0

Cybersecurity Awareness Month stat that stuck with us: voice and SMS phishing now carry the highest average breach cost of any entry point ($5.29M, IBM). What this means for your cybersecurity program: hubs.li/Q04yXv4D0

Cyber AB's Matt Travis at last night's Town Hall: don't expect CMMC task force recommendations until the back half of October at the earliest. The reform ideas floated (clearly labeled speculative) are worth a read: hubs.li/Q04yMzGk0

DFARS 7012 and CMMC don't formally require an SBOM. Primes are writing them into SOWs and flowdowns anyway, and "we don't have one" is a rough answer in a vendor review. What to include: hubs.li/Q04yD0LJ0

A fintech's AI assistant got talked into full account takeover over one conversation. Just one example of how AI is changing attack surfaces & what a pentest should cover. Breakdown by @softwaresecured: hubs.li/Q04yrthN0

CISA, NSA, and FBI recently warned U.S. AI companies about industrial-scale model distillation. For DIB contractors the nearer issue is still CUI in a commercial tool. Requirements and templates: hubs.li/Q04y3jmt0

90% of AI-adopting leaders think longer retention improves models. Most frameworks still say keep it only as long as you need it, then dispose of it. Here's how to meet requirements while balancing business goals: hubs.li/Q04y3jl20

The FedRAMP 20x Class D (High) pilot RFC proposes one hard gate: a CR26-compliant Class C certification before Dec 1, 2026. So if Class D is on your roadmap, Class C is the work in front of you. Read our guide: hubs.li/Q04y3j590

CMMC reform feedback isn't just about who assesses you. Industry and the DoW CIO flagged inconsistent CUI designation as a major challenge reform is tackling. Guide to categories and where it shows up: hubs.li/Q04y2Sfl0

Some orgs are still running on NIST's outdated password rules. The latest guidelines formally recognize passkeys and expand phishing-resistant MFA, which DoW also named its #1 IT fundamental for DIB contractors. Read the guide: hubs.li/Q04xyZtC0

FedRAMP stops taking new Rev 5 applications June 11, 2027. 20x isn't a lighter Rev 5: 46 KSIs instead of a prescriptive ~400-control baseline, no agency sponsor, and a Class A path to the Marketplace via SOC 2 Type II. How they compare: hubs.li/Q04xyZvk0
