

ǝ̝̰̰̣̪̻͍͞s̀ɹ͙͇͕̻̘ǝ͖̗͚ʌ̳͖͘ͅǝ̯̰͎̯͎̺ᴚ̣̙ ̜̦̝͉̖͟e͍͎͚̺n̸͉͙̭̩ͅg̝͖̫i͈̗̱̖̰n̪̕e̬̼͢ȩr͚̯̤͈̞͇̰
Joined June 2015
- Tweets787
- Following568
- Followers2.2K
- Likes1.6K






ReWolf retweeted

I've recently been digging into Android security and found some interesting stuff, more details on the higher-impact findings will be published later but in the meantime, I'm kicking off the blog with some low-severity findings and will update over time.
lowlevel.fun/posts/low-sever…
ReWolf retweeted

I wrote-up how I used o3 to find CVE-2025-37899, a remote zeroday vulnerability in the Linux kernel’s SMB implementation. Link to the blog post below 👇
ReWolf retweeted
Want to support security researchers from Dragon Sector in covering legal costs piling up after they went public with logic bombs in train firmware?
IBAN for donations is available here:
ccc.de/en/updates/2024/das-i…
Talks for context:
media.ccc.de/v/37c3-12142-br…
streaming.media.ccc.de/38c3/…
ReWolf retweeted
Reverse engineering Mortal Kombat GRA file format by @rwfpl
blog.rewolf.pl/blog/?p=1837
blog.rewolf.pl/blog/?p=1982#…

ReWolf retweeted

Issue #4 is out – enjoy!
pagedout.institute/?page=iss…
Please RT and tell your friends :)

ReWolf retweeted

In the spirit of "this talk could've been a tweet", I just pushed a button:
#BinDiff is now open source.
- Snapshot release, no major new functionality
- Release binaries later today or tomorrow
- This is my 20% and I won't we able to act on PRs until end of Q4 (OOO traveling)

ReWolf retweeted
After 20 years BugChecker is back! A SoftICE-like kernel debugger for Windows 11 (and Windows XP as well). Check it out: github.com/vitoplantamura/Bu…

ReWolf retweeted

Linux is a modern operating system where getting info on the memory layout of another process involves parsing text files.

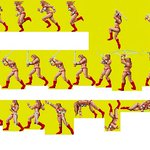
I never managed to finish a blog post about the Golden Axe file formats, so I figured I’ll just make the source code available github.com/rwfpl/rewolf-gold…
Enjoy 😎


ReWolf retweeted

A common strategy for cryptographic research is to take an old attack and see if you find vulnerable implementations. I took this to a new level with a 379 year old attack: Breaking RSA keys with Fermat's factorization algorithm fermatattack.secvuln.info/

ReWolf retweeted
My favorite typo story, "Street Fighter 2: The World Warrier"
(fabiensanglard.net/sf2_warri…)

I feel like this deserve a bit more visibility 👏

I don't recommend creating Kernel Mode drivers in C#, as it is highly experimental, but its possible.
github.com/VollRagm/KernelBy…
This is another example, a Driver with memory reading and writing capabilities communication over a hooked function.

ReWolf retweeted

friendly reminder that leaking KPROCESS from a MI process continue to hold strong even on the latest 21H1
blog.rewolf.pl/blog/?p=1683