

Self-taught malware analyst. Reversing #botnets | #IOC's collector | Fighting #threatactors.
Saint-Léonard, Montréal
Joined April 2018
- Tweets190
- Following15
- Followers523
- Likes562
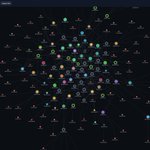



PanchanScope (formerly ChanGather) is out.
A tool to discover and map the Panchan botnet relay network from its 1919/tcp P2P socket:
- multi-threaded recursive crawler
- geolocation and ASN enrichment
- AS classification (relays grouped by operator)
- interactive live web map with discovery tree
- JSON and DOT exports
Research and educational use only.
github.com/redrabytes/changa…


Family #GoDDoSAgent
IP 94[.]154[.]43[.]117 (🇳🇱 AS219502 Storm Industries LLC)
Downloader hxxp[://]94[.]154[.]43[.]117/bins[.]sh
C2 94[.]154[.]43[.]117:2222
Listener 94[.]154[.]43[.]117:9111


Family: trojan.gafgyt/tsunami – still spreading the malware atm.
IP 213[.]232[.]114[.]14 (🇳🇱 AS3214 xTom GmbH)
Spreader 94[.]154[.]43[.]69 (🇳🇱 AS219502 Storm Industries LLC)
Downloader hxxp[://]213[.]232[.]114[.]14/handshakebins[.]sh + /nokillbins/handshakebins[.]sh
FTP ftp://anonymous@213[.]232[.]114[.]14:anonymous/
C2 64[.]89[.]160[.]222:5487
Listener 64[.]89[.]160[.]222:55487
cc/ @petikvx @500mk500


Kyorij — a native IRC/DDoS bot (Mirai/Gafgyt-style) smuggled inside an Android APK.
It poses as a system "System" app (com[.]chingusapk[.]juan) with a banking-RAT permission set as a decoy.
The real engine is native: lib/*/libbot.so.


It's salted with fake IOCs to waste analyst time: RFC 5737 documentation IPs, a literal decoy token, GitHub/Cloudflare IPs, a K8s-internal domain and a .onion in a plain DNS table.
Don't trust the strings — reverse the dispatcher.

IOCs
Package: com[.]chingusapk[.]juan ("System")
C2: 38[.]87[.]117[.]7:6767 (IRC)
DynDNS: bobbarnacle[.]duckdns[.]org
IRC channel: #op-cascade-2024
Bot build ID: b7f4a2e1-9c88-4d63-8f0e-2a91c4d5e6f7
HTTP beacon: /api/v1/beacon (7-domain rotation pool, see thread)
Cert: CN "Android Debug" (default debug key — not a pivot)
Hashes
APK: 251f6bb6a4273c411d0c23599fc5cc226e6483209045361dd005cc2cd0f91f9b
libbot.so (arm64): 6c820926fd58f297085481796d3590c267126e1ef0b5849defddb7927f33ea7d
libbot.so (armv7): 5afd442f76e1dfe138de0d0d936c50067c6038fb68fb0e1b3e282c7bba907bbd
libbot.so (x86): 90b17a29766c07170ac845ee1eea96a04f0e0f9dba92ab23da9230c206d017dc
#Android #Malware #DDoS #Botnet #ThreatIntel #DFIR


New malicious APK — two-stage native implant posing as a Huawei SDK.
Fake system "Logcat" app (com[.]huawei[.]qx): hidden from recents, boot persistence, overlay perms, native ARMv7 payload.
#Android #Malware #ThreatIntel #DFIR #Mirai #Botnet


Hashes (2/2)
ELF (UPX packed): 5ebb38c858a0b0202708649408ef7b79d02472fd61fd00d7f071f505388087f3
ELF (UPX unpacked): 8e3df94a5ee61add57686c5939b1173aefa8be5814b0e76aec69cbf133cbd53d
No C2 was found atm, feel free to reverse the APK (that's the only way to reverse the C2 — according to my analysis).
cc/ @500mk500 @skocherhan @petikvx @SaifuddinAmri__