Now part of HackerOne! Follow @Hacker0x01 for updates.
Joined June 2017
- Tweets793
- Following1.9K
- Followers1.2K
- Likes2K
Pinned Tweet
We’re excited to announce that we’re joining HackerOne!
We’ll work together to build developer-first security solutions that help organizations innovate faster while increasing resistance to attacks. Learn more: hackerone.com/press-release/…
PullRequest retweeted
How @Brose_Karriere uses a microservice architecture to scale horizontally and cost efficiently to handle data for 2M+ e-bikes.
raynigon.de/architecture/202…
#IoT #Cloud
PullRequest retweeted
Beta: @Hacker0x01 customers can now request code reviews for security fixes straight from H1 reports without having to connect their code repository! In a H1 report, select "Request code review" and paste the code patch you'd like reviewed.
PullRequest retweeted
Motorhead is a memory and information retrieval server for LLMs by @Metal_io written in #rustlang (e.g., build a CLI tool to talk to an LLM). I haven't messed with it yet but looks pretty slick👌
github.com/getmetal/motorhea…
PullRequest retweeted
.@Hacker0x01 has rolled out new AI that supports hackers finding the same vulnerability in other H1 customers! Today, we're announcing our first milestone: enabling hackers to find and validate CVEs (cve.mitre.org) at scale. 🧵
PullRequest retweeted
CISQ's 2022 report on cost of poor software quality highlights cybercrime as the top focus area for the year - with losses rising 64% in 2021.
Remember this when you hear folks on your eng team talk about readability, maintainability, and refactoring.
it-cisq.org/the-cost-of-poor…
go-gpt3 v1.1.9 has been released 🚀
go-gpt3 is an OpenAI GPT-3 API client enabling Go/Golang programs to interact with gpt3 APIs.
Thank you @dabdine for contributions 🙏
github.com/PullRequestInc/go…
#golang #GPT3 #openai
PullRequest retweeted
Today I'm thrilled and honored to transition @Moonlightwork to its new owners Jonathan Doyle, @damonjackman, and Dan Green. It's bittersweet to play a smaller role in the community, but this is amazing news for Moonlight's customers and developer community... 🧵 1/6
We're excited to announce that @moonlight_work has been acquired by its largest customer! There's no better home for this incredible community than with Jonathan Doyle, @damonjackman and Dan Green 🎉
Excited to announce that @moonlight_work has new owners! 🎉Thank you to @GitPushAll and all the @pullrequestcom team. Learn more about our plans to offer more to developers and customers here - moonlightwork.com/blog/moonl…. Onwards and upwards!
PullRequest retweeted
Exciting news. 🎉 StyleCI now supports Python 3.11. styleci.io/
PullRequest retweeted
I'm honored to be co-presenting at @Hacker0x01's 2022 Security@ livestream event Oct 13th with @Tranzito1's Head of Engineering, @willbarrettdev!
Come watch us talk about security + code review securityat.hackerone.events/…
PullRequest retweeted
PHP security releases landing tomorrow. If you are on a PHP version older than 7.4, get upgraded to 7.4. If you are on 7.4 or higher, upgrade to the latest patch when it comes out tomorrow. The new releases will be 7.4.32, 8.0.24, 8.1.11 and 8.2.0RC3.
PullRequest retweeted
Reminder that naming recommendations in pull request reviews are nitpicky until they’re not nitpicky. – at Austin, TX
PullRequest retweeted
Despite proving incredible value, and a near unanimous consensus that OSS warrants commercial support, “we as an industry have not figured out how to make open source financially sustainable for the vast majority of maintainers.” (@JoshuaKGoldberg)
blog.joshuakgoldberg.com/six… – at Austin, TX
PullRequest retweeted
Penetration tests are versatile and easy to launch. You can use them for source code review:
PullRequest retweeted
#SecurityAt2022 will be here before you know it! Get early-bird pricing now through 8/05! From networking and workshops to panel discussions and keynote speakers, you won’t want to miss our 2022 conference in San Diego!
securityat.hackerone.events/…
@Hacker0x01 #CyberSec #ARMyourteam
PullRequest retweeted
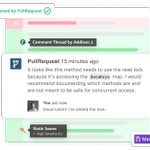
Secure code review is an extremely effective attack resistance management strategy. At @Hacker0x01 we're able to get proposed updates to the @pullrequestcom platform reviewed by vetted engineers in our reviewer community like @GrahamJCampbell in every PR.
#PHP #Security
![Graham Campbell, member of the HackerOne secure code review community, posts a comment to a GitHub pull request identifying a potential security issue. The comment reads:
"I think you probably want [REDACTED] as the 3rd parameter to [REDACTED] here. The PHP docs read like that's the default, but it depends on what version of the library you are linked against. Explicitly passing that arg makes sure you get a hard crash if you accidentally deployed to an environment linked against an old version of the lib, without support for the modern standard."](https://pbs.twimg.com/media/FYS0fZ6XEAADRhR.jpg?name=small&format=webp)
ALT Graham Campbell, member of the HackerOne secure code review community, posts a comment to a GitHub pull request identifying a potential security issue. The comment reads: "I think you probably want [REDACTED] as the 3rd parameter to [REDACTED] here. The PHP docs read like that's the default, but it depends on what version of the library you are linked against. Explicitly passing that arg makes sure you get a hard crash if you accidentally deployed to an environment linked against an old version of the lib, without support for the modern standard."
PullRequest retweeted
Learning TypeScript by @JoshuaKGoldberg is available on O'Reilly! Josh is maintainer of TypeScript ESLint and member of @Hacker0x01’s network of expert code review engineers helping teams catch issues before they reach production.
oreilly.com/library/view/lea…
PullRequest retweeted
How to Catch Injection Security Vulnerabilities in Code Review by @willbarrettdev - member of @Hacker0x01’s network of expert code review engineers helping teams catch security issues before they reach production.
hackerone.com/vulnerability-… – at Austin, TX
PullRequest retweeted
We just published the first security vulnerability fix for @pullrequestcom from our public bug bounty program on @Hacker0x01! The depth and thoroughness that went into its discovery, triage and escalation were very impressive.
Thank you @bugraeskici!
hackerone.com/reports/155801…