

doing onchain investigations better than your local law firm
Investigative Analyst
Joined January 2026
- Tweets933
- Following550
- Followers1.4K
- Likes1.9K





Peak laundering patience! 4,932 ETH was withdrawn from the mixer back in 2022, and over the next four and a half years all of it was deposited back in
In June 2022 this wallet withdrew 4,932 ETH from Tornado Cash
After that all of this ETH went back to Tornado Cash, from July 2022 to this week, the longest gap between transfers 15 months
All of this is probably done to complicate demixing and make it harder to identify who is behind the funds
0xFFD837984668002AA8AaE4A8839782293c91187e

CryptoBilis Ledger drainer continues sending funds to Tornado Cash
1 hour ago more than $1.1M in ETH was distributed to 4 wallets, and from those wallets all funds went to the mixer
Looks like many more millions will go the same way
Around $7.5M in ETH is sitting here right now, $2M has already gone to Tornado from this wallet in two rounds
0xfa4EaBB840A33C156E600311433AE261CBfCb0e2

‼️ Attacker returned $11M to 79thVault in less than 24 hours after the exploit
Yesterday 16,249 BNB was exploited from 79thVault infrastructure
After a round of onchain negotiations the exploiter sent 15,000 BNB back today
1,249 BNB stayed with him as a bounty, 7.7% of the exploited amount
Return address: 0x2BFcF0475e7B40cd68E91A7178Cf5E43262EB7b2

Scammer who extracted over $300M from Coinbase users continues laundering funds through Tornado Cash
$1.11M was moved from one of the consolidation wallets, swapped to ETH and sent to the mixer 3 days ago
8.3 ETH were sent to another wallet and bridged to Hyperliquid, where spot XMR1 was bought for that amount
Still holding $16M on this consolidation wallet, untouched for a year
0xC84C35f57CaEeB5Da8E31D1144c293Ae5851Ab84

More than $292,000 drained from hundreds of wallets
The drain happened in the last days of August, but I only confirmed it now, as multiple users pointed to the same drainer wallet
Stolen funds are still sitting on that wallet, everything swapped to $DAI, $ETH and $BNB
0x91CDAf83687ED670C4CC8C0c77f7F7b996e3329B


‼️ User withdrawals are back open, but it took $201M out of Bitget Protection Fund
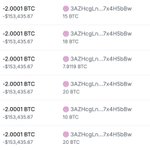
2,432 BTC moved to their hot wallets


Bitget started withdrawing from their Protection Fund
Around $1,000,000 in BTC was moved to their Hot Wallet earlier today
6 transactions of 2 BTC each and 1 tx of 0.1 BTC
There are 3 wallets in their Protection Fund with total holdings of 5,487 $BTC (~$464M)
3H6JnFoz5jcoATKQ83BuQ3cUUCHswqfgtG
3AZHcgLnJL5C5xKo33mspyHpQX7x4H5bBw
3KUwtHc5UhWQ76z6WrZRQHHVTZMuUWiZcU
$67,588 USDT lost due to an address poisoning attack
Victim thought he was sending to his usual address, but this time looks like the address was taken from transaction history
2 days earlier there was a $567,000 transfer to the usual address, so we can say he is lucky that it wasn't that amount
Attacker already converted everything to $ETH and funding wallet shows he had several victims over the last year
Fake address: 0xca166632D25Ea74BAa93A5303Aa73F61E80fD94b Real address: 0xca16B299700674dda6941BAA1BDEEFf6d90fD94b

Suspicious that since the incident was reported withdrawals from Duelbits have been stopped for 6 hours already, as we can see by the outflow amount of txs
But still some transactions passed
25 minutes ago a small amount was sent and later connected to one of the attacker wallets, confirming it belongs to them
0x92De344C23c5D5372A95ddd7dd06B8C3be22DDD4

‼️ Looks like Duelbits got exploited for more than $4.2M in different assets
A few hours ago suspicious outflows were detected from the casino wallets to a possible attacker on EVM and TRON
$USDT was swapped to $TRX and all TRON funds were bridged to EVM
Everything was converted to $ETH and is now sitting on the attacker wallet
No comments from the Duelbits team for now
Attacker wallets:
0xA77e24Fe29d16E051e487ef4Ea7b056cb05aef76
TAvraZZFCZbDSZoyqWWRRsBkFgZqKaCGbK
An individual wallet was likely compromised back in 2022 for more than $3.7M, and laundering of these funds started only now
In November 2022 an active Binance user's private wallet was suddenly emptied and all funds moved to another wallet
Everything was swapped from $USDT and $APE to $DAI
Almost 4 years later the funds started moving again, swapped to $ETH and sent to a mixer over the last week
A wallet compromise with years of patience from attacker?
0x85f6DEb0f2E1d5BC3bADEB7f7488206AF83D4623

More than $7.5M from a Hyperliquid whale sent to a mixer after a 3 month hold on an intermediate wallet
At the start of May this trader was actively trading high value positions
At the end of the same month all funds were moved to another wallet, either by him or by someone who compromised it
Most of the funds were in $DAI
Over the last weeks activity started on new wallets and funds went to Tornado Cash, a big part of it last week
No confirmation that the whale's wallet got compromised, so either he is using a mixer for privacy, or it was compromised, as the behaviour looks like it
Whale: 0x6572BC26eDF54a74bEf243EFf10D3Fbe6D461Eb7
Mixer depositor: 0xe1C6D86ebc25691FC91965e5768c78902540BB74

‼️ More than $230,000 drained from hundreds of wallets in the last 2 days
Attack vector is still unknown, probably session hijacking
Amounts from each victim are mostly small, but the total is already big
Most of the funds are sitting in $USDC
Attacker wallet: 0x7028174ED69A237DE0791101b5b85D1E6Db35887

‼️ Looks like Orion Protocol got exploited for ~$133,000
It happened more than a week ago, but became known only today because of an onchain message
Orion team sent an offer to return the funds for a 10% bounty
All funds were swapped to $USDT and transferred to another wallet, still sitting there in $WBTC and other assets
0x5d733aF67Db143893B8Db749F3cC71Be9dcF12C4
Interesting that attacker wallet was activated a year ago and had some activity before
0xCc19F449B862B9b30747C7d60a9d9feB01c18678

Not a single day without poisoning attacks
$30,668 lost even after a successful test transfer
Victim first sent 1 $USDT to his Bybit deposit address
As always, the poisoning bot spammed 2 txs right after
The rest, $30,668, went straight to the scammer
Attacker already moved everything to other wallets, swapped it all to $ETH and looks like split the funds to fund his future attacks
Fake wallet: 0x935dFD84E507Ce08E761C42c443f1A8B8727f120
Real wallet: 0x935D177913BE5755a652C27435e5862e1218F120

Duel whale who lost $7.9M was funding his account with funds swapped from Monero
Yesterday player 6qq6 wagered almost $375M on Duel and lost all of his initial funds
All his deposits came through bridging from Arbitrum from different wallets
Every one of those wallets used the same pattern, $XMR on Hyperliquid sold to $USDC and then bridged straight to his Duel deposit address
Here is the biggest one, 7,960 XMR went through it
0xB3c9b1945aB41C76615FaC141A66C08C3C0Bf025
Either he takes privacy seriously, which high rollers often do since they get looked at closely, or he was trying to hide where the funds came from


6/ Court documents don't contain wallet addresses, but they do list the withdrawal amounts
That was enough to run timing analysis and identify where the rest of the funds ended up
They were mixed with other money and are currently sitting on this address
The last movement was 2 months ago, which suggests nobody involved has been arrested and that threat actor went quiet after the Tether freeze
0x3CEA9A7d8c0D9ccd97DA2DEbF4502A8C368705cb

7/ This case only became known through public court decisions
Even with the redactions it was possible to track exactly what happened and which wallets were involved
Credit to whoever did the analysis for the victim, identifying the wallet that received 1M $USDT, and to Tether for freezing it after the request