

Namek
Joined August 2023
- Tweets4.1K
- Following1.4K
- Followers609
- Likes10K







Sangohan on Farcaster retweeted

AiFi meets DeFi.
@bankrbot has integrated Coinbase for Agents.
→ Onchain execution across EVM and Solana
→ Non-custodial wallets that swap, bridge, and trade
→ Now connected to your Coinbase account
Build responsibly.

your Coinbase account now has an agent 🤝
check your Coinbase portfolios, trade crypto, stocks, and futures, and move funds, all from one chat
get started at bankr.bot/coinbase
Sangohan on Farcaster retweeted

bankr is coming to @Enter_Elysium
bridge, launch and trade from day one, just by asking bankr
> november 9
> bankr.bot
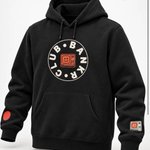
So happy 🥳🥳!!! Thank you @bankrbot 🙏! Can’t wait to wear it, it looks amazing 🤩!! base:0x22af33fe49fd1fa80c7149773dde5890d3c76f3b = Banger


we are giving away 40 bankr club hoodies to bankr club NFT holders in collaboration with @dimesonbase!
make sure you have your bankr club NFT in a wallet connected to your bankr account, or in your bankr wallet directly.
snapshot and raffle soon!
NFTs: opensea.io/collection/bankr-…
1
35

Built a paid risk gate for Base snipes.
x402 · $0.005 USDC
base-risk-momentum → riskScore + momentum + NO-GO/GO flags before any buy.
x402.bankr.bot/0xab09c3055f6…
Agents pay → call → decide. Built with @bankrbot.
2
67
Frontier intelligence: Great. I’m going to run a check to verify whether the verification of my test is valid.
Then I’ll create a test to test my test.
If you approve, we can verify that everything was verified correctly.
3
71
Sangohan on Farcaster retweeted

JPMORGAN CEO JAMIE DIMON ONCE SAID "IN 10 YEARS, #BITCOIN WILL BE CLOSED DOWN"
THIS WEEK, HIS BANK SAID BTC WILL OUTPERFORM GOLD 🤡

Sangohan on Farcaster retweeted

Screenshots of the Philip Morris website.
(reminder: they're a leading cigarette company)
It's a good calibration point for how good modern marketing is at dressing up pretty much any corporate (or, for that matter, government) behavior and making it sound responsible and safe.


Sangohan on Farcaster retweeted

@UniswapBuilders Bug report 🐛
This "v4 · 1%" pool is not a 1% pool. A hook takes another 1% on every swap, so traders actually pay 2%.
The pool list shows no hook, and the badge that used to flag custom-hook pools is gone.
Technical Details
👇🏻

Sangohan on Farcaster retweeted
Qwen 3.8 flash is truly impressive, and llama.cpp has been rapidly getting better and better at processing it
columns are: pre-existing prompt, new prompt, generated, input tok/s, output tok/s
This is on my laptop (strix halo). I think we're very close to the point where you can just use local models for a large share of tasks, and for anything more advanced, workflows like "use your local model to orchestrate queries to powerful models so your queries don't leak your personal information" actually become viable.


😂

1 billion Muse tokens for you. 1 billion for your friend.
Referrals are now live in Muse! Invite up to 20 friends and you'll each get 1 billion tokens when they onboard and redeem your code. That's up to 20 billion Muse tokens for you. muse.ai/join

52
Sangohan on Farcaster retweeted
It's an increasingly common take that AI hacking means cybersecurity is doomed.
I disagree. I think cybersecurity is naturally defense-favoring once people get their shit together. And anyone who continues to hold cryptocurrency (including me, ~90% of my net worth) is implicitly making that bet.
Here's why I am making that bet.
First, the oversimplified punchy one-line statement:
If AI can prove Navier-Stokes and FLT, then AI can prove the statement "this program is secure" as a mathematical theorem. Even if the program is very complicated.
Now, the nuance:
(See also: vitalik.eth.limo/general/202… )
The word "secure" is hiding all kinds of skeletons in the closet in terms of what it actually means. What does it mean for Signal (the encrypted messenger) to be "secure"?
The most basic definition you might think of is: no one who doesn't hold the recipient's secret key can read the contents of the message.
But:
* Did you remember to include _other_ critical forms of security? Can the adversary forge messages? Can the attacker prevent messages from reaching the recipient? Can they cause your client to crash by sending malformed messages?
* Have you made sure that your model of the adversary includes attackers that interfere with the protocol actively and not just passively? And attackers that interfere by replaying messages to you or the recipient that either of you sent over the wire at any point earlier?
* What if the adversary hacked (or _is_) the Signal server?
* How did you learn which public key belongs to the recipient in the first place? What if that process was tampered with?
* What if your device gets hacked at some point in the past or future - is your message still safe then?
* What if your key leaks because of a bug in your operating system? Or because you got a bugged version of the Signal client? Or what if the database is corrupted?
* Or the libraries, interpreter or compiler of the programming language you wrote it in?
* What if your key leaks because tiny perturbations in perceptible signals generated by the hardware leak mathematical relationships that can extract the key a few hundredths of a bit at a time?
* Are you hiding the *size* of the payload? Does that matter?
* You're definitely not hiding the identity of the sender and the recipient, and the exact time each message was sent (think: not just time-of-day, but also time deltas between one message and the next). Is that not enough to deduce a lot of important facts about what relationships you have, and what *kinds* of conversations you are having?
So ... even definitions can be over a thousand lines of code, and need deep careful thought to figure them out.
Working on making definitions more human-readable is of extreme importance - it's perhaps the only "high-level language" that matters right now.
But even still, even despite all of the above, for security-critical components, the definition is a much smaller attack surface than the implementation. Verifying that the definition is adequate is a much more tractable task than scanning over the code directly - and can become even more tractable with better tooling.
Definitions are also _additive_: if two groups have two different definitions A and B, then, well, you can just prove that the program satisfies both A and B. Code is not additive in this way: if a program is A + B, a bug in A _or_ B can sink the whole thing. Definitions are additive. And if you can't satisfy A and B at the same time, you've isolated the most important philosophical issue for your project to spend its next few weeks grappling with.
Sometimes, definitions are not much smaller than the implementation - UI components might be one example. But for many of the most critical components - message-passing protocols, sandboxes, cryptography like SNARKs and FHE - the asymmetry is real.
Historically, a large class of failures with this approach have come from people only verifying a small portion of their code, that they self-declared to be the security-critical portion, and ignoring the rest - and it turns out that something in the rest of the code is security-critical too.
This was reasonable back when verification was difficult and scarce. The solution today: sorry, you have to verify over literally your entire program, including database, networking, any caching layers, everything. Modern AI can do it.
So it's not about "the good guys find all the vulnerabilities before the bad guys do" - that could maybe work too, after all a finite program only has a finite number of vulns, but it's riskier - it's specifically an asymmetric strategy of making code that is much more resilient in the first place.
This is the kind of direction that Ethereum is going in for the next few years. There is no future for blockchains - especially blockchains with scalability and privacy - without doing this. We need to make software actually secure. And we have already made a lot of progress.
Lol


Last month I wrote about how we can build a positive and safe future for everyone: meta.com/thefutureisforevery…
Every lab has the responsibility and incentive to move at the pace required to train its models safely, and the ability to take its own actions to ensure that happens.
The reality is:
- People won't want to use agents that are misaligned with them and that don't do what they ask, so labs have a strong natural incentive to make their models more aligned.
There is a lot of debate about slowing progress on capabilities until alignment catches up. My view is that trust and alignment are quickly becoming the most important capabilities that will differentiate agents and models. Any lab that doesn't focus on alignment will fall behind.
- Labs face significant liability if their models cause harm, so they have a strong incentive to prevent this as well.
Meta delayed shipping Muse for several months to focus on safety and security. We didn't call for everyone else to do this before we would. We just did it as part of our day-to-day work because it was clearly the right thing for people and for us. I'm proud of the security foundations we've built.
- Engaging independent evaluators and advisors is industry best practice. MSL already does this today in several areas because it helps produce better work. Other labs can just do this too. In general, it would be helpful for there to be a larger and more diverse ecosystem of evaluators.
- Committing the significant majority of compute towards serving people rather than racing towards recursive self-improvement is one of the best ways to ensure we develop this technology safely. Meta has made this commitment and other labs can do this as well.
I believe the key to building a positive future for everyone is maintaining the right balance of power. This is within our power to do.
38
Sangohan on Farcaster retweeted

🚨 Attackers stole a METR API key and used it for three weeks, consuming credits worth about $600,000.
A fail-open bug disabled Google authentication on a public agent dashboard. The attacker prompted an agent to reveal the key and added SSH persistence.
How the exposed app was abused: thehackernews.com/2026/09/at…

“Hey Claude! Check my repo to make sure there aren't any keys lying around and that there's no sensitive information in it.”
“Okay, I'll check if gh is installed on your machine. All good ! I found it. I'll push the repo and then check to make sure there's nothing compromising in your repo.”
36
They have super-intelligence, and we don't even have an autocorrect that actually works. Gud tek.
1
54
Thanks 🤝

🚨: Nobel Prize physicist Roger Penrose claims there is no such thing as nothingness.
Your soul is eternal because matter cannot be destroyed.


Readers added context they thought people might want to know
Penrose has not claimed there is no such thing as nothingness or that souls are eternal. His conformal cyclic cosmology describes successive aeons without an absolute beginning, but he identifies as agnostic and makes no statements linking physics to souls or divinity.
en.wikipedia.org/wiki/Roger_Pen…
skymania.com/an-interview-w…
bbc.com/future/article…
1
68