

AI-powered continuous security audits for smart contracts on EVM, Solana, CosmWasm, & Move. Secure your code on every GitHub PR. Built by @jvr0x.
Blockchain
Joined March 2025
- Tweets81
- Following46
- Followers96
- Likes115






Pinned Tweet
Most "AI security scanners" never publish numbers.
So we did.
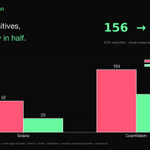
OdinBench v0.1: 38 contracts, 36 known vulns, full methodology open. False positives cut 45% by our verification pipeline.

ALT OdinScan cuts false positives in half.
Odin Scan 🔍 retweeted
Now Odin Scan runs on private inference 🎉🎉
To celebrate the migration of our inference infrastructure to @near_ai, get an 80% discount on any subscription you get using the code NEARAI!
Valid until the end of October ✌️
odinscan.ai

Now Odin Scan runs on private inference 🎉🎉
To celebrate the migration of our inference infrastructure to @near_ai, get an 80% discount on any subscription you get using the code NEARAI!
Valid until the end of October ✌️
odinscan.ai
Odin Scan 🔍 retweeted

Most security scanners run your private code through someone's black box. @odin_scan runs it in an Intel TDX enclave and hands you the attestation to prove it!
Odin Scan's AI analysis runs on @near_ai's private inference, inside a hardware-sealed Intel TDX enclave. Your code is decrypted only inside it, invisible to the host, the infrastructure operators, and the model provider alike!
So the report ships the proof: the raw Intel TDX quotes for the gateway and the model that served your scan, the nonce that binds them to that specific report, and a link to Intel's attestation roots.
Open the report, expand "Confidential inference verified" and check it yourself. The same evidence is included in the PDF as well.
Don't trust. Verify 🔥

ALT Odin Scan report details page with confidential inference verification!
Odin Scan 🔍 retweeted
Today @odin_scan moved all its inference to @near_ai private TEEs! 🔥
Your code and your prompts are now encrypted end to end. Not even NEAR can read them, and you can verify it with a cryptographic attestation.
There is no bigger upgrade for a security scanner than that. 👇

Odin Scan 🔍 retweeted
When I started building @odin_scan at first, I thought running 3 models in parallel was going to be better than running 1.
At that time it made sense, but it added a lot of complexity.
Today, that was the accuracy ceiling in @odin_scan, which is now fixed!
One agent that keeps full context and attacks its own findings beat it, on the same model:
F1 0.89 → 0.97
17/17 bugs found
3 false positives → 1
@odin_scan is very good at findings smart contract exploits today! Check it out 👇
odinscan.ai/blog/odinscan-ac…

Odin Scan 🔍 retweeted

The Mad Easy Hackathon on the Hub is officially concluded with all five winners announced. Congratulations to all the winners!
Shoutout to @madscientists_x for organizing the hackathon and @odin_scan for sponsoring
Details on the winning submissions: madscientists.io/hackathon/s…

Pleased to have sponsored this hackathon!
Winners, feel free to send DMs to either this account or @jvr0x for getting access to your odin scan credits!

MAD easy hackathon 1st & 2nd place 🧑🔬
1st - @temporalkaku for MAD votes
2nd - Subzero from @cosmosrescue for IBC-02
congrats to all the scientists that participated and thank you once again to our judges & sponsors @cosmoshub & @odin_scan 👏

Our GitHub action allows you to set up different levels of visibility based on the threat model.
• full
• counts
• private
Here's a matrix to help you choose 👇
Read more about them in the documentation
docs.odinscan.ai/github-acti…


Did I mention that you can run @odin_scan on CI?
There's a GitHub action which allows you to block buggy code so exploits don't reach production!
docs.odinscan.ai/github-acti…
Odin Scan 🔍 retweeted
Ran @MANTRA_Chain's mantra-dex through @odin_scan.
91! Zero Critical, zero High.
The three mediums are worth a look but the foundation
is clean 🚀

In spite of the recent incident with rsETH, @aave worked as intended. It is and has always been the benchmark for defi.
It's no surprise to us that aave v4 has scored high in @odin_scan!

We are glad to see protocols in crypto being secure! 😍
That's how it should be.
Congrats to @RujiraNetwork on the strong @odin_scan score for their contracts!
They keep their contracts safe 👏

Read the full methodology + reproduce the benchmark yourself 👇
odinscan.ai/blog/odinbench-v…
v0.2 in 60 days: side-by-side vs Slither, Aderyn, Mythril.

On EVM, every Critical-severity finding was a real bug 🔥
16 out of 16. Zero false positives at the Critical level.

Multi-agent → pre-filter → repository trust model → severity adjustment.
Solana: 52 → 23 false positives
CosmWasm: 104 → 63
Combined: 156 → 86 (45% reduction)
Recall preserved!
The dirty secret of LLM-powered code analysis: out of the box, it floods you with findings.
Most are wrong.
Engineers stop reading after the third "potential reentrancy" on a view function.
So we built a verification pipeline. And measured it.
🚨 2026 DeFi Hacks Wake-Up Call
In just the first 3 months of 2026, 16 smart contract exploits have drained $328 MILLION from protocols.
One single infrastructure attack alone took $285M.
The rest? Logic flaws, key compromises, oracle misconfigs… the usual suspects that could have been caught before launch.
Your project doesn’t have to be next.
Odin Scan’s AI-powered auditor runs 3 models in parallel, checks 38+ vulnerability rules, and supports EVM, Solana, CosmWasm & Cosmos SDK, all in ~3 minutes.
One scan = zero exploits
👉 Scan your smart contract now at odinscan.ai

ALT DeFi hacks in 2026
Did you know we have a blog?
We've been publishing deep dives on smart contract security, real exploit breakdowns, and practical guides for developers.
Some highlights 🌟
• Vibe Coding Smart Contracts: What Could Go Wrong?
• Reentrancy in 2026: The Bug That Refuses to Die
Check it out at odinscan.ai/blog
Did you know you can now display Odin Scan badges on your protocol's github or website?
There are both static and dynamic badges!
You can find snippets directly on the report details page,
as well as in the documentation.
To find more, check our docs 👇
docs.odinscan.ai/dashboard/b…

We have introduced a Pay-Per-Scan option to Odin Scan!
If you are in need of sporadic security audits for your smart contracts, you can use Odin Scan Credits for that.
Credits don't have an expiration date and give you access to the same features Pro users have.
Get your credits now at odinscan.ai/pricing 🚀
By popular demand, now you can buy Odin Scan Credits to use on the platform!
1 credit = 1 scan
No need to buy a subscription if your protocol is somewhat static and you don't need constant security audits.
Credits do not expire, and you get access to the same features that @odin_scan Pro users have!
Check it out 👇
odinscan.ai
