
🍎 🛡️ 🛠️ Open-Source Tools 📚 "The Art of Mac Malware" books 🫂 "Objective by the Sea" conference Support us on https://xitter.cf/t.co/tuGceSeyiC 🙏
Maui, Hawaii
Joined October 2011
- Tweets5.2K
- Following2
- Followers19.6K
- Likes2.6K



Pinned Tweet
Our Valentine's Day gift 💝
objectivebythesea.org/v9/ind…
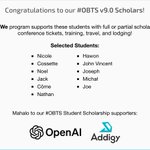
Announcing Objective by the Sea (#OBTS) v9.0:
👩🏻💼 Train: Nov 15-17
👩🏻🏫 Talks: Nov 18-20
📍 Maui, Hawaii, 2026
CFP (talks & trainings) and tickets are now officially open! Hope to see you by the sea 🏝️
Special 🙏🏽 to @andyrozen!!

Like all our tools, TaskExplorer is free & open-source! 🥰😇

TaskExplorer now natively integrates with Ollama 🤖
...so you can bring your favorite local LLM to the party!
Latest version available here:
objective-see.org/products/t…

Objective-See Foundation retweeted

TaskExplorer now natively integrates with Ollama 🤖
...so you can bring your favorite local LLM to the party!
Latest version available here:
objective-see.org/products/t…
I've just (re)written TaskExplorer
Think Process Monitor but for macOS, open source, & much more powerful 💪🏽
Highlights:
• CLI + JSON export
• On-device AI assistant
• Code signing + VirusTotal context
• Live process/file/dylib/network activity
objective-see.com/products/t…

Objective-See Foundation retweeted
security? privacy? 😬

Objective-See Foundation retweeted

A fake Zoom installer found by #JamfThreatLabs hides a stolen macOS password inside a config file using invisible Unicode characters.
CloudSyncD uses that password once to launch a backdoor with elevated access. okt.to/SHA3m2
#CybersecurityAwarenessMonth

Objective-See Foundation retweeted
Smart way to limit AI agents! 👏
But, @Apple, please don't make Full Disk Access changes harder for macOS Endpoint Security tools!
They (per your design) require FDA plus a special entitlement you only grant after vetting, so please keep them easy for users to install! 🙏
Last week, our @patrickwardle spoke with @ThomasClaburn at @TheRegister about this exact issue: AI apps "undoing" Apple's hard work on security & privacy.
Great to see @Apple jumping into action to protect the security & privacy of its users.
Read: theregister.com/ai-and-ml/20…

Objective-See Foundation retweeted
But its not secure 😩 Exhibit A: prompt injection (via local attack against ChatGPT)


Objective-See Foundation retweeted

⚠️ Potential scam / impersonation concern: this Mac App Store app uses an icon that closely resembles OpenAI’s official ChatGPT icon. @Apple is obsolete to fight with scams....
@OpenAI @AppleSupport
apps.apple.com/us/app/ai-cha…

Objective-See Foundation retweeted

Wild. I've written about clones like this multiple times and Apple sees it and pulls them no problem.
But I still have no idea how they keep getting through the review process.
This one is currently #2 in education on the Mac App Store 😖

⚠️ Potential scam / impersonation concern: this Mac App Store app uses an icon that closely resembles OpenAI’s official ChatGPT icon. @Apple is obsolete to fight with scams....
@OpenAI @AppleSupport
apps.apple.com/us/app/ai-cha…
Maybe Apple read about our research 🤭
Either way, happy to see them taking steps to limit the granting of Full Disk Access (FDA)!
techcrunch.com/2026/10/02/ap…


Mahalo to @WIRED for covering our initial research into ChatGPT (CVE-2026-100754)
Traditionally, protecting the privacy & security of Apple users meant focusing on malware & attackers...now, AI agents belong in that threat model too 🤖⚠️
More bugs reported, so stay tuned... 👀
Objective-See Foundation retweeted

If you are a Mac OSX user, check out @objective_see !! They are a non-profit foundation focused on macOS security, driven by the mission to create free tools, grow and support a global community and advance Apple security through education, research, collaboration, and opportunity!!
objective-see.org/tools.html

Objective-See Foundation retweeted

CVE-2026-86950: The Great Glyph Grift
calif.io/research/the-great-…

Objective-See Foundation retweeted

🍎🐛 I got Claude making this, maybe it's useful for others as well.
Every Apple security advisory since 2002 - parsed, indexed, charted. With links to writeups, POCs and presentations.
apple-cve.com/

Mahalo to @WIRED for covering our initial research into ChatGPT (CVE-2026-100754)
Traditionally, protecting the privacy & security of Apple users meant focusing on malware & attackers...now, AI agents belong in that threat model too 🤖⚠️
More bugs reported, so stay tuned... 👀

While the focus has been on AI agents’ hacking capabilities, a recently patched vulnerability in the macOS version of OpenAI’s ChatGPT shows that AI software is itself an inviting—and vulnerable—target. wired.com/story/a-flaw-in-ch…

0-day flaws in ChatGPT let a local unprivileged attacker bypass OpenAI's safeguards, subvert the agent on macOS, and take over your Dot.
Responsibly reported to (and ack'd by) OpenAI. Our research into the (in)security of AI agents continues... 🫠

Dots are here!
A new way to use AI that works 24/7 for you; get more of your time and attention back to work at a higher level.
openai.com/index/introducing…


Security & privacy used to mean fighting malware and hackers
...now, we have to add "AI agents" to that threat model 🤖 😅
Mahalo to the @nytimes for spotlighting some of our recent ChatGPT research & bugs!
nytimes.com/2026/09/29/techn…

#OBTS v9 schedule is LIVE! 🔥
objectivebythesea.org/v9/sch…
If you're into Apple security (yes, including securing those pesky AI agents 🤖), you seriously don't want to miss this one!
Hope to see you by the sea ☀️🌊

Objective-See Foundation retweeted
Just wrote up a lil threat landscape review January-September. TL;DR: ClickFix is basically the on-ramp for everything now, stealers evolving into something much worse.
Go read! 9to5mac.com/2026/09/28/secur…

Objective-See Foundation retweeted

MacOS credentials are under fire from PAMStealer (Wavel), a new infostealer using PAM-based credential validation. Jamf caught it using a server-side key exchange that prevents static payload recovery. jamf.com/blog/pamstealer-wav…
