

https://xitter.cf/t.co/PWPG5WoB1D
Switzerland
Joined June 2008
- Tweets6.8K
- Following396
- Followers1.9K
- Likes114K





Thank you @hack_lu and thank you @Ministraitor 🙏


Talk delivered. Here are the slides seriot.ch/computation/talks/… looking forward to the rest of the conference and tonight's social event 🍻🍻

What if Jira, Unicode, basic text utilities or even a printer can compute far beyond their intended role?
At @hack_lu 2026, I'll present UNINTENDED COMPUTATIONS: from unexpected computers to a security methodology for finding hidden execution surfaces.
2026.hack.lu/agenda/

Nicolas Seriot retweeted

CLAUDE FOUND THE SEEDS
anthropic.com/research/ecdsa…

« defenders have one advantage attackers never will: they can test their own code first »

For the second time in Google Chrome’s history, Google awarded a $250,000 bounty for a full-chain exploit… to @XBOW. Here’s the full story:
At an all-hands at the start of 2026 in Malta, I set the team a crazy challenge. A full-chain exploit of Chrome by the annual Black Hat cybersecurity conference in August.
I believed there were few better tests of whether @XBOW could move beyond web applications to desktop software, servers and devices.
Chrome is one of the most hardened pieces of software on the planet, used by more than half the world’s population.
A full-chain exploit lets an attacker take total control of a machine, where they can read every email, password and bank login the user types. You don’t need to download anything or click a phishing link. Visiting the wrong site is enough.
So @moyix, Andres Luksenberg, Baul Lee, and Willem Pinckaers took on the challenge along with a fifth teammate: OpenAI's GPT-5.6 Sol.
They built a chain they thought would win, but Google told us they already knew one of the bugs.
We were already in Las Vegas for Black Hat and DEF CON, and the team didn’t want to go home without the win.
So Brendan and the agents built a new exploit in just 6 days.
We submitted it to Google and waited.
The news came through that we'd done what should’ve been impossible. A full-chain bounty of $250,000, the first awarded under Google’s 2026 rules.
It took just 6 days and $40,000 of compute to construct an exploit that affects a billion users of Chrome on Windows. An intelligence-agency veteran told me his team used to spend 6 months on this kind of vulnerability.
My takeaway: the cost of finding truly critical vulnerabilities is collapsing, for attackers and defenders alike. Restricting powerful models is not the answer; GPT-5.6 Sol is already public.
But defenders have one advantage attackers never will: they can test their own code first.
Assume your software is exploitable. Whoever is hunting your bugs has the same building blocks we did.
This is cause for urgency but not panic.
XBOW is now developing an autonomous product for testing compiled software (desktop applications, servers, embedded devices), and partnering with the world’s top organizations to design that product.
If you’d like to be one of them, get in touch.
P.S. Restart Chrome whenever the Update button appears!

Nicolas Seriot retweeted

🍎🐛 I got Claude making this, maybe it's useful for others as well.
Every Apple security advisory since 2002 - parsed, indexed, charted. With links to writeups, POCs and presentations.
apple-cve.com/

New article! ncurses terminfo can simulate a two-counter Minsky machine, making repeated parameter expansion computationally universal seriot.ch/computation/termin… demo: a parasitic Fibonacci computation inside /usr/bin/top
That's clearer with a diagram. Give this post a like if you'd like more "anatomy of a bug" soon!

New "anatomy of a bug" write-up: why CFXMLParser crashes on a 7-byte input? seriot.ch/security/cfxmlpars…
New "anatomy of a bug" write-up: why CFXMLParser crashes on a 7-byte input? seriot.ch/security/cfxmlpars…
New short write-up! For years, four Mach calls could reboot macOS and iOS devices because two lines in XNU were in the wrong order. seriot.ch/security/ipc_panic…


What if Jira, Unicode, basic text utilities or even a printer can compute far beyond their intended role?
At @hack_lu 2026, I'll present UNINTENDED COMPUTATIONS: from unexpected computers to a security methodology for finding hidden execution surfaces.
2026.hack.lu/agenda/
🤖 Made with AI


Paged Out! #9 features two or my articles:
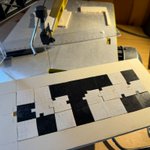
🧩 Computiles: 10 tiles, designed with my son Émilien, that enforce binary arithmetic through geometry.
💻 An Unexpected Computer: universal computation from echo, ed, test and exec.
Free PDF: pagedout.institute/ @PagedOutZine


I built Cartopolis. Today's Switzerland rendered as 1999-style GIFs. seriot.ch/cartopolis/
No filters. Client-side rasterization from vector packs. Fully static architecture. seriot.ch/drawing/cartopolis…
Bake your own region using github.com/nst/Cartopolis
@openstreetmap @SwissOSM

And now people are starting to program with ICU transliteration rules 🤦♂️ here's a Sudoku solver

「Unicode標準UTS#35で定義される文字変換ルールは
#チューリング完全」との研究報告があった🥸
seriot.ch/computation/uts35/
これにインスパイアされて
UTS#35変換ルールだけで「#数独 を解く」実装を作ってみた😎
アルゴリズムは変換ルールだけで実装。
補助的に変換の連続実行と可視化のみPython使用

I've been wondering for a while if anything in Unicode could accidentally compute. I've just shown that
@unicode UTS#35 transliteration rules are universal, computing Collatz with just 3 rewrite rules running on stock ICU, shipped with every major OS. seriot.ch/computation/uts35/

Engineering folklore holds that @Jira is Turing-complete.
I've built a proof: a working Minsky register machine using Jira Automation rules. 2 bugs + 3 tasks = 5.
seriot.ch/computation/jira.h…
If your complex Jira automations feel like programs, it's because they literally are.
Nicolas Seriot retweeted

Palestra "Jogos em PostSript - Jogue Xadrez Contra a Sua Impressora" por @nst021 está publicada!
Escreva jogos em PostScript, a linguagem de impressora dos anos 80. Sokoban & Tetris rodando nos desktop, Jogos da Velha e Xadrez na impressora, humanos vs. impressoras.
🇧🇷 Legendo!
