

cipher security labs https://xitter.cf/t.co/IZByfO2Dr4
🇪🇺🇮🇱
Joined October 2016
- Tweets8.5K
- Following692
- Followers1.1K
- Likes4K




Nir Yehoshua retweeted

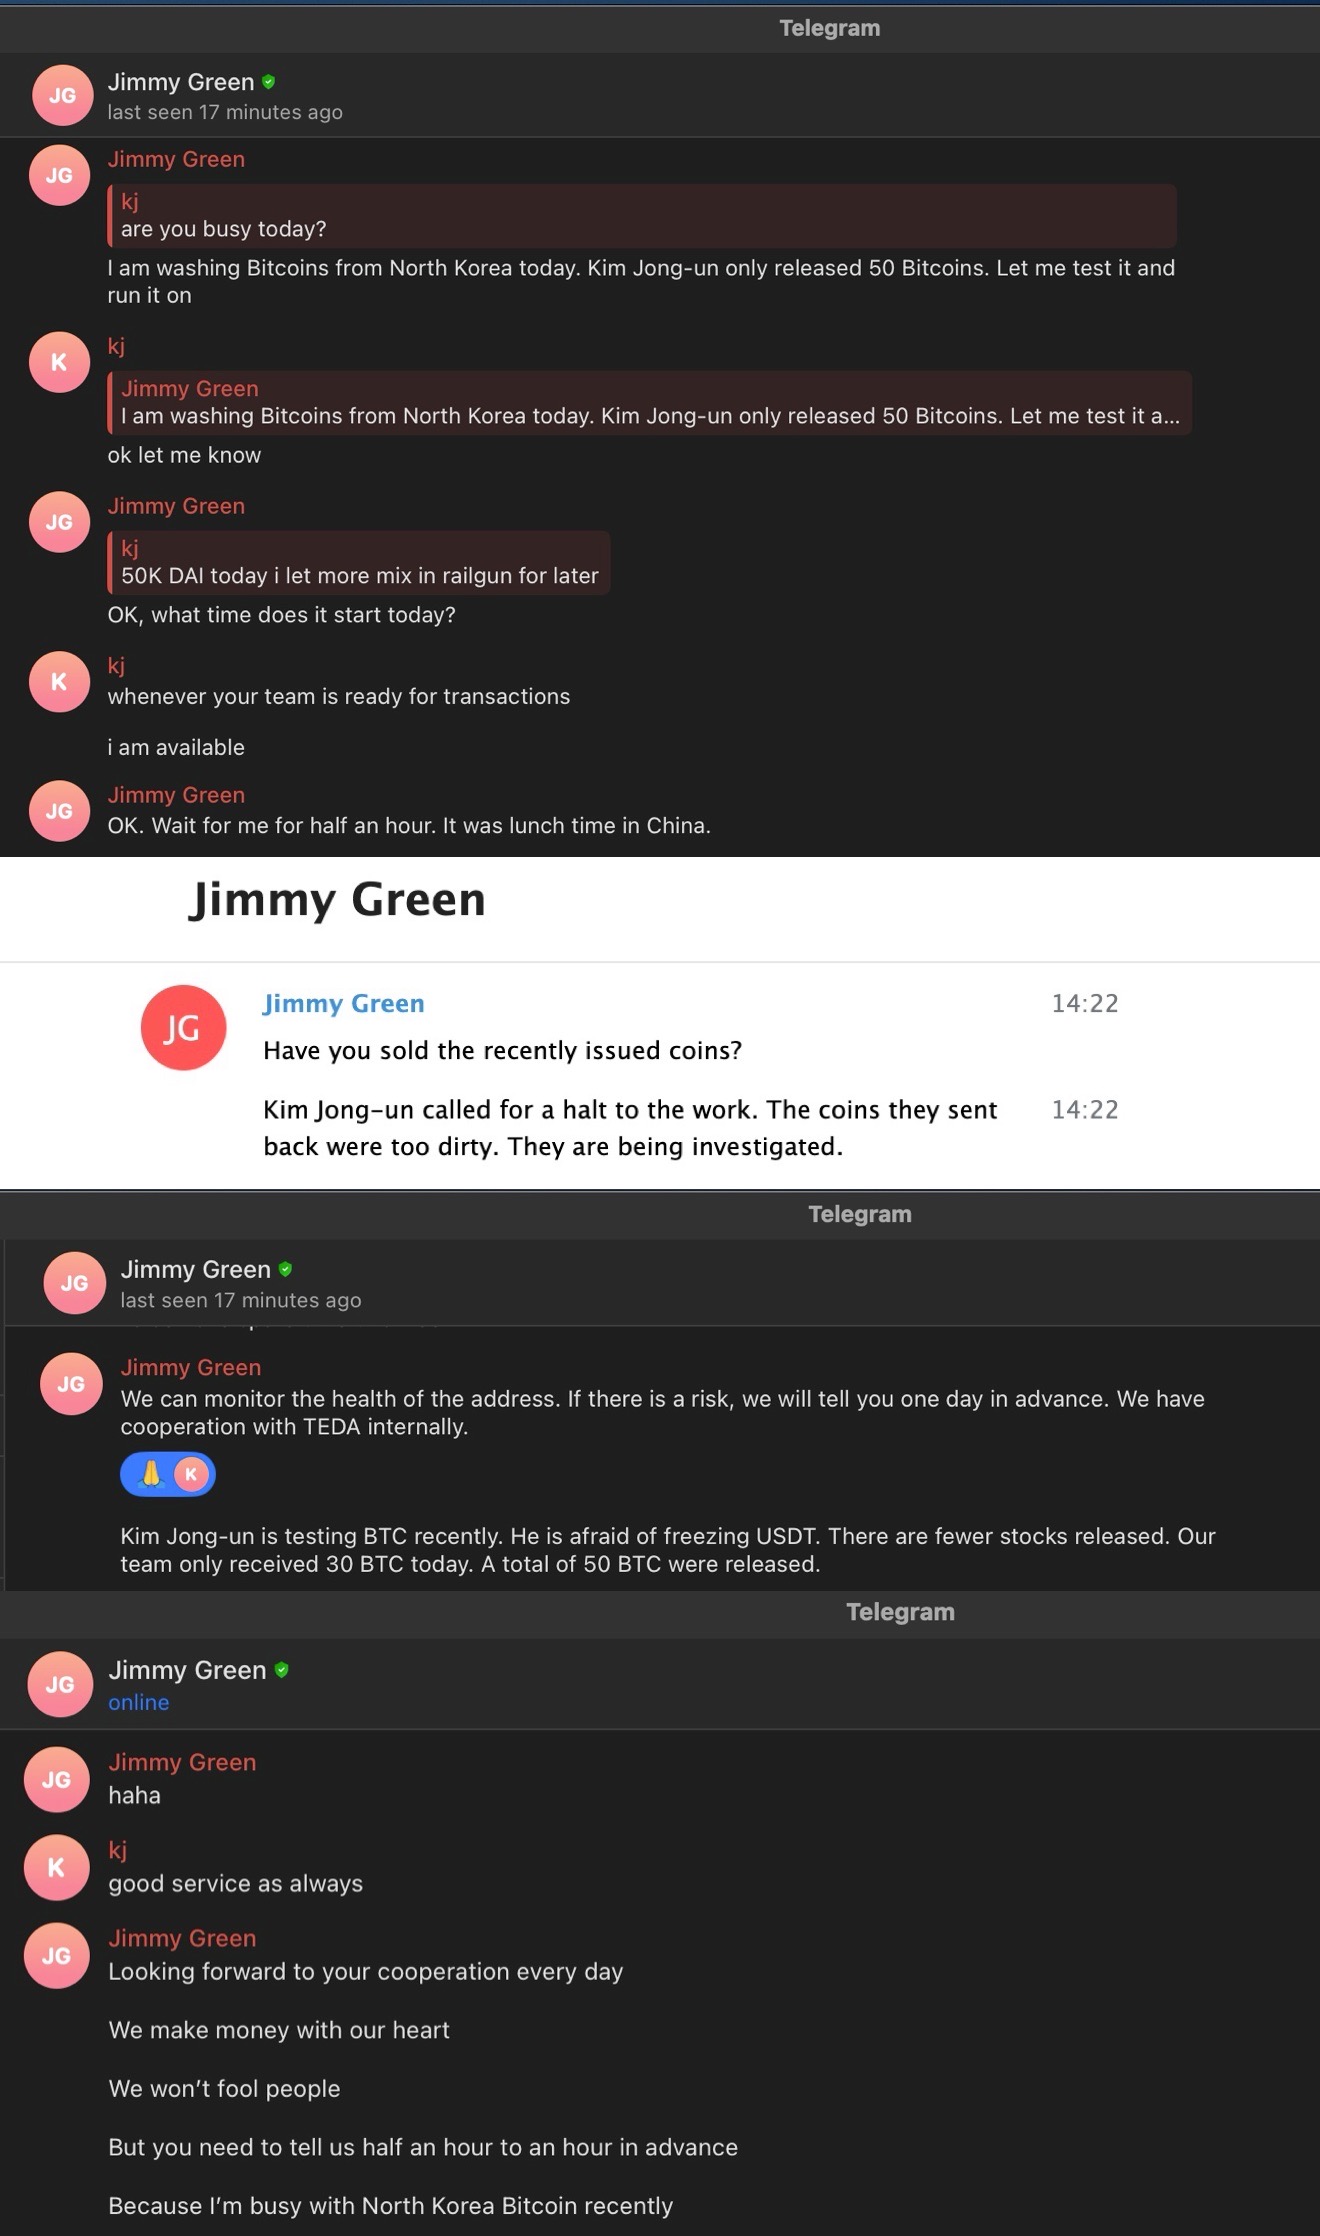
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.



Nir Yehoshua retweeted

Claude has discovered a previously unknown enzyme system hidden in the DNA of bacteriophages. Beside the enzyme’s gene sits a long array of repeating DNA—a structure that looks somewhat similar to CRISPR.
We don’t yet understand what this system does, but only a handful of known systems share its features, and all of them are able to cut, copy, and paste DNA. Historically, the discovery of such programmable systems has helped revolutionize medicine. CRISPR, for instance, is now the foundation of genetic medicines. But it will take much more work to learn what this system does, and whether it can be put to similar use.
Read more: anthropic.com/news/claude-di…


Nir Yehoshua retweeted

🚨 BGP Hijack at 2026-09-20 10:04 UTC
🇮🇷AS197207 (MCCI-AS) announced 190 prefixes, creating 10,865 conflicts with 1,524 ASNs in 100🌏.
🌏Max propagation: 100%
⏱️Duration: 8 min (first part) and 15 min (second part)


Nir Yehoshua retweeted

636606729769440499166579950236036751749912014371509557713570027508971809534551913252252094954941974952859310861988904737359709200557919
is a factor of RSA-896
saweis.net/posts/rsa-896.htm…
Nir Yehoshua retweeted

BREAKING: 🇺🇸 Warren Buffett steps down as Berkshire Hathaway Chairman after more than 60 years at the company.
Berkshire has returned 6,642,000% since 1964, nearly 120x the S&P 500 returns.


Nir Yehoshua retweeted

BREAKING: OpenAI reveals a 10,000-agent AI swarm solved the Navier–Stokes problem in 88 hours, using 130 billion output tokens to crack one of mathematics’ most famous unsolved problems.
Nir Yehoshua retweeted

We’re sharing a solution to the Navier-Stokes Millennium Prize Problem, one of the deepest problems at the frontier of mathematics.
The proof was produced by a group of agents, using an OpenAI next-generation model significantly more capable than GPT-6 Astra.
The problem concerns whether the description of smooth three-dimensional fluid motion modeled by the Navier-Stokes equations can break down. It has remained unresolved for roughly 90 years.

Nir Yehoshua retweeted

We at RefineSec already do it - Adaptive Mutated Attacks while producing behavioral detection rules natively for EDR / XDR solutions for attacks that were not prevented.
Feel free to visit our website and schedule a demo: refinesec.com

Nir Yehoshua retweeted
SOC Analyst Professional - Attack & Defense is officially LIVE. 🔥
I built this course around one rule:
Do not just learn the attack. Execute it. Investigate it. Detect it. Tune the detection. Then try to bypass your own rule and write a better one.
Every technique follows the same hands-on workflow:
ATTACK → TELEMETRY → INVESTIGATION → DETECTION → TUNING → VALIDATION → BYPASS → BETTER DETECTION!
We go hands-on with:
RDP
PsExec
WinRM
Active Directory discovery
PowerShell and LoLBins
WMI
Registry persistence
Scheduled Tasks
Services
Credential dumping
LSASS access
Privilege escalation
Process injection
Ransomware-style activity
and much more.
Then you investigate the evidence across Windows Event Logs, Sysmon and Elastic Security EDR, and build the Elastic Security KQL detection rules yourself.
I do not want you to finish a PsExec lab knowing only that PsExec.exe exists.
I want you to understand what it drops on the target, what service it creates, what executes, what telemetry Elastic Defend collects, how to detect the behavior, and how that detection could be bypassed.
Because a rule that only catches the exact command you used in the lab is not a detection I would trust.
🔥 SOC Analyst Professional - Attack & Defense is live now:
trainsec.net/courses/soc-ana…
Stop memorizing attacks. Start owning the detections that catch them.

Nir Yehoshua retweeted
🚨 Two CVEs. One router. One complete chain to ROOT.
Last week, we disclosed two vulnerabilities affecting the Cudy WR3000 2.0:
🔴 CVE-2026-71960 - Authentication Bypass
CVSS v4.0: 9.3 Critical
🟠 CVE-2026-71961 - OS Command Injection
CVSS v4.0: 8.7 High
Individually, they are serious.
Chained together, the story changes completely.
1/ During our firmware research, we recovered signing material that could be used to forge a valid JWT.
That means bypassing the authentication boundary, accessing the MQTT interface, and reaching a vulnerable command path.
The end result?
Operating system command execution as root.
2/ This is exactly why I keep saying:
Stop looking at vulnerabilities only as isolated CVEs.
Attackers don't think in CVSS tables.
They look for chains.
One weakness opens the door.
Another one gives you the keys.
And suddenly, something that looked "limited" becomes a complete compromise.
3/ Then things became even more interesting.
Shortly after our disclosure, Hunt & Benito independently released public exploit tooling reproducing the attack chain.
Important clarification:
We did NOT create, commission, or contribute to that exploit.
But once public tooling exists, the barrier to reproducing the attack drops dramatically.
And the research entered a second wave of international coverage.
4/ Our findings were covered by:
SecurityBrief - original disclosure
lnkd.in/de6YFUF7
SecurityBrief - public exploit follow-up
lnkd.in/d6hx8c-h
HackRead
lnkd.in/eUBGwjzZ
SecNews
lnkd.in/d3xpfPiv
BugsToday
lnkd.in/dbend8WA
5/ For me, the most important takeaway isn't the headlines.
It's the technical lesson:
Security boundaries rarely fail in isolation.
Authentication bypass alone tells one story.
Command injection alone tells another.
But connect them together and you get:
Firmware -> signing material -> forged JWT -> MQTT access -> command injection -> ROOT
That is the attack path that actually matters.
6/ This is the kind of research we want to push at Cipher Security Labs:
Deep vulnerability research
Full attack-chain analysis
Understanding how weaknesses interact
Product security
Coordinated vulnerability disclosure
Not just:
"Here is a CVE."
But:
"Here is what an attacker can actually do with it."
More research coming.
Our CVE Tracker:
ciphersecuritylabs.com/CVE-T…
#CyberSecurity #VulnerabilityResearch #CVE #IoTSecurity #ProductSecurity #FirmwareSecurity #SecurityResearch #InfoSec
Nir Yehoshua retweeted

Public exploit code can chain two #Cudy WR3000 v2 flaws to bypass login checks and allow full control when the router’s control service is reachable. Update to firmware 2.5.24 or later.
Listen to the article or read: hackread.com/cudy-wr3000-rou…
#CyberSecurity #Router #Vulnerability

By Cipher Security Labs @UrielKosayev

Public exploit code can chain two #Cudy WR3000 v2 flaws to bypass login checks and allow full control when the router’s control service is reachable. Update to firmware 2.5.24 or later.
Listen to the article or read: hackread.com/cudy-wr3000-rou…
#CyberSecurity #Router #Vulnerability
New vulnerability disclosure from Cipher Security Labs.
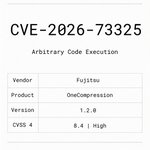
CVE-2026-73325 affects Fujitsu OneCompression 1.2.0 and can lead to arbitrary code execution.
Severity: CVSS 4.0 - 8.4 High
Looking for security research that goes beyond standard testing? We help organizations uncover high-impact vulnerabilities before attackers do.
Track our CVEs: ciphersecuritylabs.com/CVE-T…

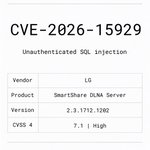
New CVE from Cipher Security Labs: CVE-2026-15929, an unauthenticated SQL injection in LG SmartShare DLNA Server v2.3.1712.1202. CVSS v4.0: 7.1 (High).
Track our CVEs: ciphersecuritylabs.com/CVE-T…

Respect @MaorShlomo

TLDR: I’ve started a small fund from my Base44 money that’s focused on cancer research and breakthrough therapies.
I’ve invested in 7 incredible companies in the past 4 months and plan to do more as my liquidity allows. Listing my investment thesis below
I welcome anyone like me who has been blessed financially to join me and find ways to finally manage or even end this disease.
Longer -
I honestly believe cancer is humanity's worst enemy.
~40% will be diagnosed with it, and out of which a ~third won’t make it. And numbers are currently not getting dramatically better.
For many it might sound like a statistic
But for some of us who have been there ourselves or had to go through it with a person we love, it’s one of the worst things you can imagine.
I had to go through it with my mom - who passed away 4 months ago and whom I miss and think about every single day since.
This field needs a dramatic push.
The current wave of technology and AI is doing a lot of good in the world,
But cancer therapy is one of those things that are not moving nearly fast enough.
And there’s no good reason for that - AI is creating so much opportunity right now.
Here's my thesis on how things will play out:
For drug development, the bottleneck will shift to
1. Manufacturing
2. Real world testing
"In silico" is going to accelerate incredibly fast. AI is identifying new target proteins and designing new molecules, drastically shortening timelines.
AI will create an abundance / inflation of ideas. It will help design molecules faster than anything historically possible.
This is already happening.
Play with Claude Science or Codex and you'll be surprised at how far you can get with just a few prompts.
We need a better way to *manufacture and test* the 1000s of ideas coming from AI models spitting out potential drug candidates
1. Manufacturing: i.e. how fast can we synthesize a potential drug
Not too far into the future, companies with manufacturing excellence will win over companies with the smartest scientists.
Being able to synthesize a drug candidate fast - together with efficient methods to test efficacy (more on that below), basically means you get more shots at a target hence more chances at succeeding.
This is the same exact lesson the software industry learned about the importance of fast iterations.
Companies like Starget Pharma are leveraging AI heavily to iterate on drug candidates + figured out in-house manufacturing in a way that lets them iterate on drugs almost as fast as if they were a software company iterating on features.
2. Real world testing: i.e. how fast can we get a call on a drug's efficacy.
We need better real-world indicators for drug efficacy than mouse / animal models.
The success rate of animal models -> human clinical trials is less than 8%.
Breaking down this bottleneck will change the entire industry.
Developing an oncology drug and taking it through all clinical trials usually cost >> $ 100m
Thus taking the wrong bet is devastating (but still, happens a lot).
Giving drug development companies the ability to better understand the efficacy and mechanisms of their drugs will change a lot. Esp in the age of abundant drug candidates.
Furthermore - and once those methods proved efficient - Joining forces with regulators to shorten (or even skip) some clinical trials altogether will cut years from the process and save many lives by bringing new drugs to market faster.
CuResponse is pioneering functional testing - taking real cancer biopsies and showing drug efficacy with very high precision. Can be used for precision oncology as well as testing new drugs.
Cellint is providing a fully automated cell-culture R&D platform for companies and researchers.
----
I’d love to see a future where there are “cloud services” for drug development companies.
A company should eventually be able to submit a drug candidate programmatically and receive:
1. The synthesized drug.
2. Testing across cells, tissues, organoids, and tumoroids.
3. Structured results showing what worked, what failed, and why.
4. A recommended next iteration derived from the biological reactions.
I’ve invested in all of the above companies and am searching for additional companies to bring this “cloud services for drug dev” vision to life.
----
Alongside it, I am also investing in direct therapeutic moonshots.
I invested in Baccine, which is developing a bacteria-based cancer immunotherapy platform and deserves an entire separate post.
I’m also a proud LP in Even One Ventures - @sytses ’s fund to fight cancer. Sid and Jacob Stern are an inspiration to me as I’m making my first steps in the field, and I bet their companies will make a massive impact.
And 3 other incredible companies focused on how therapies are delivered - where I’ll elaborate in future posts.
----
I’m still obviously spending most of my time on Base44. Which is a plus for the companies - as we’re able to support them with tools, software, AI agents, etc.
I’m looking for people to join me - invest side by side or help one of the companies.
I don’t have a name for the fund yet, nor an email or a website
I will get to it this weekend and will post it in the comments.
Redis CVE-2026-23479 is not just a Stream issue.
At Cipher Security Labs, we reconstructed the unblockClientOnKey() UAF and measured additional trigger surfaces.
Key finding: stream-only ACL hardening is incomplete.
Full research:
ciphersecuritylabs.com/resea…
New research from Cipher Security Labs.
WordPress Plugin Profile Builder <= 3.16.1
Unauthenticated Media Upload
We responsibly disclosed the issue to Cozmoslabs, and it was fixed in Profile Builder 3.16.2.
Write-up:
ciphersecuritylabs.com/resea…
PoC:
youtube.com/watch?v=fTGOfsUo…