
Next Generation of Network Access and Security. https://xitter.cf/t.co/PQqsYm58Op
Berlin
Joined January 2021
- Tweets438
- Following69
- Followers2.8K
- Likes358




NetBird v0.81.0 is out.
Here's what's new:
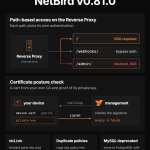
𝗣𝗮𝘁𝗵-𝗯𝗮𝘀𝗲𝗱 𝗮𝗰𝗰𝗲𝘀𝘀 𝗰𝗼𝗻𝘁𝗿𝗼𝗹 𝗳𝗼𝗿 𝗥𝗲𝘃𝗲𝗿𝘀𝗲 𝗣𝗿𝗼𝘅𝘆 𝘀𝗲𝗿𝘃𝗶𝗰𝗲𝘀
Each HTTP target can now use the service's authentication, bypass it, or block the path with a 403. So you can require SSO on /, let webhooks through on /webhooks/, and keep /admin/ off the public domain entirely.
𝗡𝗲𝘄 𝗰𝗲𝗿𝘁𝗶𝗳𝗶𝗰𝗮𝘁𝗲 𝗽𝗼𝘀𝘁𝘂𝗿𝗲 𝗰𝗵𝗲𝗰𝗸
Peers need a device certificate from your own CA and have to prove they still hold the private key. Management repeats the check every 4 hours, so a removed key or expired certificate closes access within that window.
𝗔𝗹𝘀𝗼 𝗶𝗻 𝘁𝗵𝗶𝘀 𝗿𝗲𝗹𝗲𝗮𝘀𝗲:
• 𝚗𝚋𝚕𝚒𝚗𝚔: forward local ports into your NetBird network without root, a TUN device or an installer
• Duplicate policies: copy an existing policy into the create wizard with pre-filled settings
• MySQL store deprecated: move to PostgreSQL with the new 𝚗𝚎𝚝𝚋𝚒𝚛𝚍-𝚖𝚢𝚜𝚚𝚕-𝚖𝚒𝚐𝚛𝚊𝚝𝚎 tool
𝗦𝗲𝗹𝗳-𝗵𝗼𝘀𝘁𝗶𝗻𝗴? Make sure you're on the latest Traefik with the right headers when you upgrade!
Full release notes: github.com/netbirdio/netbird…
Knowledge Hub: netbird.io/knowledge-hub/net…

What does 𝗭𝗲𝗿𝗼 𝗧𝗿𝘂𝘀𝘁 mean?
(and how do you implement it?)
Zero trust drops the trust that used to come free with being on the same network. Every request is authenticated and authorized, so no user, device or workload gets access just because it sits "inside".
Here are six terms you should know:
1. 𝗭𝗧𝗡𝗔 (𝗭𝗲𝗿𝗼 𝗧𝗿𝘂𝘀𝘁 𝗡𝗲𝘁𝘄𝗼𝗿𝗸 𝗔𝗰𝗰𝗲𝘀𝘀): no device, user or agent is trusted by default. Every request is checked, whether it comes from inside the network or not.
2. 𝗗𝗲𝗳𝗮𝘂𝗹𝘁 𝗱𝗲𝗻𝘆: nothing is allowed. Every connection needs an explicit policy.
3. 𝗟𝗲𝗮𝘀𝘁 𝗽𝗿𝗶𝘃𝗶𝗹𝗲𝗴𝗲: each identity reaches only what it needs. A contractor gets the couple of hosts running the tool they work on, not the whole subnet.
4. 𝗣𝗼𝘀𝘁𝘂𝗿𝗲 𝗰𝗵𝗲𝗰𝗸: access depends on device state. A policy can require a minimum NetBird client or OS version, an allowed country or network range (EU-only, for example), or a specific process running on the device.
5. 𝗟𝗮𝘁𝗲𝗿𝗮𝗹 𝗺𝗼𝘃𝗲𝗺𝗲𝗻𝘁: what attackers do after getting in. One phished laptop hops to a jump host, then to the prod database.
6. 𝗠𝗶𝗰𝗿𝗼𝘀𝗲𝗴𝗺𝗲𝗻𝘁𝗮𝘁𝗶𝗼𝗻: the network is split into small, separately governed zones, so a compromised machine stays contained. In NetBird, groups and access policies do this instead of VLANs and firewall rules.
How to implement zero trust with Netbird: netbird.io/knowledge-hub/imp…

NetBird is on the most installed list in Community Scripts.
4,093 installs in the last 30 days 🥳
Community Scripts is a community-run library of install scripts for Proxmox VE and Incus. Our neighbors include Docker, Immich, Pi-hole, Home Assistant OS and WireGuard 🧡
To try it, run this in your Proxmox VE or Incus host shell:
𝚋𝚊𝚜𝚑 -𝚌 "$(𝚌𝚞𝚛𝚕 -𝚏𝚜𝚂𝙻 𝚑𝚝𝚝𝚙𝚜://𝚛𝚊𝚠.𝚐𝚒𝚝𝚑𝚞𝚋𝚞𝚜𝚎𝚛𝚌𝚘𝚗𝚝𝚎𝚗𝚝.𝚌𝚘𝚖/𝚌𝚘𝚖𝚖𝚞𝚗𝚒𝚝𝚢-𝚜𝚌𝚛𝚒𝚙𝚝𝚜/𝙿𝚛𝚘𝚡𝚖𝚘𝚡𝚅𝙴/𝚖𝚊𝚒𝚗/𝚌𝚝/𝚗𝚎𝚝𝚋𝚒𝚛𝚍.𝚜𝚑)"
It installs the NetBird client in a small Debian 13 container (1 CPU, 512 MB RAM, 4 GB disk), on x86-64 or ARM64. Join it to your network with a setup key or SSO, then check it with 𝚗𝚎𝚝𝚋𝚒𝚛𝚍 𝚜𝚝𝚊𝚝𝚞𝚜.
Read more here: community-scripts.org/script…

My Grok Bot's computer got an upgrade! It runs NetBird on it and can connect to my internal @metabase 🤯 github.com/netbirdio/netbird


Your Plex library, Home Assistant, and the NAS shouldn't need a port forward just so you can reach them from the road. NetBird drops all your devices into a private WireGuard network, so everything at home is reachable from anywhere without exposing a single service to the internet. This is a must-have for a homelab.
If you've got an old PC sitting around, Proxmox is probably the best thing you can put on it. It's free, it's open source, and it turns that machine into a proper hypervisor running VMs and LXC containers. We actually use Proxmox almost daily here for testing. On our site we have a full beginners guide covering the install, spinning up an LXC with NetBird in it for remote access, plus ZFS pools and IOMMU for GPU passthrough once you're ready for the fun stuff.


If you're juggling a work network, your homelab, and a self-hosted setup on the same laptop, this one's for you. NetBird Profiles let you switch between cloud and self-hosted accounts with a single click. No swapping config files, no logging out and back in. Work, home, and lab all living in the same app. 👏
docs.netbird.io/client/profi…

ALT Settings panel showing a Profiles screen listing multiple NetBird identities.
Need to SSH or RDP into a machine but you're on a device where you can't install anything?
The NetBird Browser Client runs a full peer as WebAssembly right in the browser. Still end-to-end encrypted with WireGuard, nothing to download. Open a terminal or a remote desktop from any modern browser and just like that, you're in.

