
Joy Lee 🐱 Making (*losing) money channel https://xitter.cf/t.co/IE3rKzJ4js
Joined August 2020
- Tweets7.5K
- Following2.2K
- Followers5K
- Likes3.7K




moneygrid (theo/acc) retweeted
BREAKING: Robinhood CEO Vlad Tenev highlights Ondo's integration with Robinhood Chain during the company's earnings call.
“We want our chain to be the best home of tokenized products. They don't need to be our own.”
This is the right playbook
Robinhood Chain isn't trying to own every product, it wants to be where tokenized assets live
Ondo is a strong first proof point. It says a lot
An open platform beats a walled garden, and Ondo + Robinhood Chain could be a big step for tokenized RWAs

BREAKING: Robinhood CEO Vlad Tenev highlights Ondo's integration with Robinhood Chain during the company's earnings call.
“We want our chain to be the best home of tokenized products. They don't need to be our own.”
1
2
72
moneygrid (theo/acc) retweeted

🔔11/6(금) 치이카와마켓 신상🔔
여러분 지금 역대급 신상 리스트야.. 다들 엔화 장전해 ㅈㅂ
매지컬 치이카와 강해진 마스코트(2종) 2,090円
매지컬 봉봉드롭(4종) 660円
돼지라멘 마스코트(8종 中 5종) 1,870円
크리스마스 키라메코(3종) 2,420円
트리 우사기 1,650円
🔗 chiikawamarket.jp/collection…


moneygrid (theo/acc) retweeted

Withdrawals restored for:
- Ethereum: USDC, USDT, ETH
- BNB Smart Chain (BSC): USDC, USDT, BNB

Withdrawal Update
Withdrawals have now been restored for the following assets and networks:
- Ethereum Network: USDC, USDT, ETH
- BNB Smart Chain (BSC): USDC, USDT, BNB
We will continue to restore additional assets and networks in phases following the completion of our security checks. Further updates will be shared through official Binance channels.
moneygrid (theo/acc) retweeted

Pudgy Penguins reached out and said "brother we see your takes and appreciate them, what do you think we can do better?"
COMPENSATE THE USERS THAT SPENT YEARS OF THEIR LIFE AND MANY THEIR LIFE SAVINGS EARNING ABSTRACT XP
I thought it was pretty clear. This is the only solution.
moneygrid (theo/acc) retweeted
4 data leaks reported today:
1. Coinbase's vendor Amplitude exposed some users’ contact data (funds unaffected).
2. Bithumb (Korea) had user data leaks.
In TradFi, two securities firms in Korea leaked data:
3. Mirae Asset
4. Daishin Securities
You can't prevent a leak, but you can protect yourself.
Leaked exchange data (names, emails, phone numbers, addresses, ID documents, transaction history) is mostly used for phishing, SIM swapping, and social engineering.
Reduce info you share
- Use a unique email alias for each exchange (SimpleLogin, Apple Hide My Email, etc). A leak then can't be linked to your other accounts, and you can spot which service leaked.
- Share only what's required. Don't add optional profile details.
- Use a dedicated phone number (a VoIP or secondary SIM) for exchange accounts if you can, since leaked numbers are the main route to SIM swaps.
Lock down the account
- Use a unique, long password from a password manager.
- Turn on hardware security keys (YubiKey) or passkeys, or at least an authenticator app.
- Avoid SMS 2FA.
- Enable withdrawal address whitelisting and a withdrawal time lock if the exchange offers them.
- Set up an anti-phishing code, which puts a code you choose in every legitimate email from the exchange.
- Review active sessions and API keys regularly. Delete any API keys you don't use.
- Restrict API keys to withdraw-disabled and IP-whitelisted.
Defend against
- SIM swapping: Ask your carrier to add a port-out PIN or number lock.
- Phishing and impersonation: Assume anyone who contacts you about your account, "security issues," or "refund recovery" is a scammer, even if they know your name, balance, or recent trades.
- Exchange support staff don't ask for your password, 2FA codes, or seed phrase.
- Never click links in emails or texts. Go to the site yourself.
- "Wrench attacks": Leaked addresses plus holdings data have led to real-world extortion and robberies. Don't publicize your holdings, and keep large balances out of anything tied to your home address if you can.
If a breach is announced
1. Change the exchange password and any other account that reused it.
2. Check haveibeenpwned.com for your email address.
3. Revoke API keys and active sessions.
4. Review recent withdrawals and security settings.
5. Watch for phishing emails and texts that reference the breach, because scammers move fast after one.
Stay SAFU! 🙏

moneygrid (theo/acc) retweeted

🇰🇷 CONFIRMED: South Korea’s presidential office has decided to delay the crypto tax that was set to start Jan 1, 2027.
Korea is heating up again. Time to watch the Korean market 🔥
official : n.news.naver.com/article/011…

moneygrid (theo/acc) retweeted
⚠️ Beware if you use a Ledger hardware wallet, especially if you bought one recently.
Based on information so far, it seems to be localized to a supply chain attack with one vendor. A small number of people probably bought fake (or tampered) Ledgers.
Ledger is one of the most secure and oldest hardware wallets in the industry. Stood the test of time. But these things happen.
I expect and know all BNB ecosystem players (and all industry) to help trace and recover the funds.

Ledger is investigating reports of loss of funds from users in South East Asia who purchased products from a reseller named CryptoBillis. As a precaution, and pending the results of our investigation, we have asked CryptoBilis to pause all sales and shipments of Ledger devices. We recommend Ledger users who purchased from this reseller in the last 90 days to not initiate set up if you have not done so yet. If you have set up your Ledger device, consider moving assets to a new Ledger signer (with new seed). We will continue to inform customers of updates as the investigation progresses.
Reach out to Ledger customer support through official channels with any questions: support.ledger.com/
moneygrid (theo/acc) retweeted

[@Ledger]
Ledger 사용자 관련 Exploit 이슈가 있는 듯.
총 $86M의 자산이
7시간 전 소유주 미상의 지갑으로 이동.
정확한 원인은 모르겠지만,
공식 Ledger에서 구매한게 아니고,
다른 구매처에서 구매한 Ledger에
Exploit Kit이 심어져있던게 아닐까 추측. 🫥

If you were just drained to any of the following addresses, please can you reach out to @SEAL_911 asap. Total loss is >$72M+ and increasing.
TK6DWNpNe1w2iJRNFpU8aHdrPTATxvXT6C
TBkcUMYC7CkTK99tkTnaStQVBastfrs9d9
TCGE3xp6YGRKXxDZiLfysgJW3f22KfMNsW
TSDWtuZ2pARUVz4v3PkL2hi3iXPjowAr5a
bc1qjqgwejnp8dc0x2938x9n9954hj97t82unx49dl
0x83aeac166f6832ae3500000a24510a95a052a599
0x033636e45d519bebb7b5c2520ca6ce56fbdb4f7a
0x69c8f401cfc6cd40ac94691d6d7c48e3b7a47841
moneygrid (theo/acc) retweeted

Today I call upon the blockchain industry to calmly begin planning for "bunker mode". My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash.
Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase).
Don't rush. While I believe there is cause for action a rushed migration would do more harm than good. Don't panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets.
IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By "break" I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster).
Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture. In hindsight, May's unexpected disproof of the Erdős unit distance conjecture was our warning shot.
Yesterday's OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time?
Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.)
Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once.
Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I've witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case.
I urge large, sophisticated actors to lead by example. Project11's "risq list" (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I'll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026).
Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from "Satoshi's shield", i.e. his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS.
Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security.
The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I'll be pushing for maximum defensive acceleration.
moneygrid (theo/acc) retweeted

did you know that the terms you casually agreed to by checking that box to withdraw your money are packed with toxic clauses?
but you can’t even withdraw your money unless you agree, so it’s basically forced consent lol
🚨 summary of the major toxic clauses in abstract’s terms of service (tos)
1. the company isn’t responsible even if your assets disappear
no liability for asset losses caused by hacking, security vulnerabilities, or the company’s ordinary negligence.
if the service shuts down, any assets not transferred out by the deadline will be permanently lost.
2. extreme limits that make it hard to get compensation
even if the company is held liable for its negligence, compensation is capped at the fees you paid over the past year or $100, whichever is greater.
3. stripped of legal rights (no lawsuits)
disputes can only be resolved through u.s. arbitration (aaa), not domestic courts. class actions are prohibited.
you have just one year to bring a claim after the grounds for it arise.
4. all responsibility falls on the user
if a dispute arises from a violation of the terms or similar reasons, the user must fully reimburse the company for its defense costs, including attorney fees.
😂
this is after asking for it to be summarized twice
is an agreement this coercive even legally enforceable?
abstract, luca netz, and igloo. comedy in long shot.

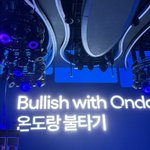
Bullish with Ondo 🔥🔥
@OndoPerps @Ondo
Rwa 섹터 붐 타고 온도 kbw 사이드파티에 다녀왔어요
레전드로 사람 많아서 다른분들 안나오게 사진찍기 불가능
오늘 세션중에 불개미님 @fireant_korea 대같투님 @Edward__Park 과 온도의 head of defi Matt 가 함께하는 세션도 있었어요 👀👀
이번에 온도에서 펍덱도 새로 런칭했는데 잘돼라… 그래야 내가 살아!!!


Join me on the Jumper waitlist. waitlist.jumper.xyz/r/JMP-D1…

moneygrid (theo/acc) retweeted
🇰🇷 코인과세 유예 활동을 위한 기부금 모집
안녕하세요 불개미입니다. 코인과세유예를 위해 행동에 나서겠습니다. 코인과세 행동을 위한 기부를 부탁드립니다.
✔️ 세가지를 하겠습니다.
1. 다시한번 국회의사당으로 직접 나가서 우리 의견을 전달하겠습니다.
2. 코인과세유예 시위트럭을 전국 주요도시에서 운행하겠습니다.
3. 코인과세유예를 위한 SNS 바이럴 캠페인을 진행하겠습니다.
🟩 기부금은 아래 항목으로 사용하겠습니다.
1. 코인과세유예 시위트럭 운행
2. 코인과세 유예 SNS 캠페인 진행
3. 코인과세유예를 위한 의원실 기부, 양당 본부 기부
4. 기타 비용으로 활용
5. 부족한 자금은 불개미 사비를 추가해서 코인과세유예활동 예정.
다들 너무 잘 아시겠지만 2024년에도 제 사비까지 넣어서 최선을 다해 코인과세유예 시위를 진행했습니다.
2024년도에 실제로 시위트럭도 돌리고 제가 한겨울에 직접 시위하러 나가면서 KBS, MBC, SBS 뉴스에도 노출되었습니다. 분명 과세유예결정에 영향을 미쳤을것이라고 생각합니다.
코인 투자자 여러분 다시한번 힘을 모아주세요. 단돈 1만원도 괜찮습니다. 1명이 내는 돈보다 1만명이 실제 후원까지 했음을 정치권이 알게된다면 절대로 코인과세유예를 쉽게 강행할 수 없습니다.
솔라나주소 : FQASshV6GR8ZGD7XTwsW7TQuz8Jou3GQcZ2HHwC5a8DW
EVM 주소 : 0x403b5240c372ba850233911854ccc5f6f250e2a1
* 저번과 동일하게 모금된 전액 + 제 사비까지 추가해서 코인과세 유예를 위한 시위차, 옥외광고에 활용하고 모든 소비내역을 공개하겠습니다.
* 코인과세 유예에 기부하고싶은 프로젝트나 기관 관계자들은 @fireantico 로 연락주세요. 기부자를 공개하지 않고 기부해주시면 불개미 커뮤니티에서 무료홍보 도와드리겠습니다.
* 기자님들도 연락주세요. 국회 앞으로 시위하러 갈 예정입니다.


moneygrid (theo/acc) retweeted

코인과세 유예 활동을 위한 기부금 650만원 전달 완료.
2029년까지 유예 2029년에 폐지 행운의 777 이라는 느낌으로 보내려고 했으나 수수료 $1 까먹어서 걍 돈 여러번 보낸 청년이 되었습니다.
저도 보내면서 사실 힝 내돈~ 했는데 코인 투자자들의 마음을 대신 담아 전한다고 생각하며 보냈습니다.
코인 투자자를 위해 직접 뛰며 행동하는 사람을 위해 힘을 보태줍시다.


🇰🇷 코인과세 유예 활동을 위한 기부금 모집
안녕하세요 불개미입니다. 코인과세유예를 위해 행동에 나서겠습니다. 코인과세 행동을 위한 기부를 부탁드립니다.
✔️ 세가지를 하겠습니다.
1. 다시한번 국회의사당으로 직접 나가서 우리 의견을 전달하겠습니다.
2. 코인과세유예 시위트럭을 전국 주요도시에서 운행하겠습니다.
3. 코인과세유예를 위한 SNS 바이럴 캠페인을 진행하겠습니다.
🟩 기부금은 아래 항목으로 사용하겠습니다.
1. 코인과세유예 시위트럭 운행
2. 코인과세 유예 SNS 캠페인 진행
3. 코인과세유예를 위한 의원실 기부, 양당 본부 기부
4. 기타 비용으로 활용
5. 부족한 자금은 불개미 사비를 추가해서 코인과세유예활동 예정.
다들 너무 잘 아시겠지만 2024년에도 제 사비까지 넣어서 최선을 다해 코인과세유예 시위를 진행했습니다.
2024년도에 실제로 시위트럭도 돌리고 제가 한겨울에 직접 시위하러 나가면서 KBS, MBC, SBS 뉴스에도 노출되었습니다. 분명 과세유예결정에 영향을 미쳤을것이라고 생각합니다.
코인 투자자 여러분 다시한번 힘을 모아주세요. 단돈 1만원도 괜찮습니다. 1명이 내는 돈보다 1만명이 실제 후원까지 했음을 정치권이 알게된다면 절대로 코인과세유예를 쉽게 강행할 수 없습니다.
솔라나주소 : FQASshV6GR8ZGD7XTwsW7TQuz8Jou3GQcZ2HHwC5a8DW
EVM 주소 : 0x403b5240c372ba850233911854ccc5f6f250e2a1
* 저번과 동일하게 모금된 전액 + 제 사비까지 추가해서 코인과세 유예를 위한 시위차, 옥외광고에 활용하고 모든 소비내역을 공개하겠습니다.
* 코인과세 유예에 기부하고싶은 프로젝트나 기관 관계자들은 @fireantico 로 연락주세요. 기부자를 공개하지 않고 기부해주시면 불개미 커뮤니티에서 무료홍보 도와드리겠습니다.
* 기자님들도 연락주세요. 국회 앞으로 시위하러 갈 예정입니다.
