



Its fun to audit Fairy with Mythos 5.1. The big surprise is, her container design holds, no critical vulnerabilities where found. Fairy should be back online tomorrow with all suggested hardenings.

Michael Niedermayer retweeted
FFmpeg 9.0.2 is out with bug fixes!
9.0-series highlights: animated WebP decoding, ProRes RAW VideoToolbox & APV Vulkan acceleration, Playdate encoding, new Vulkan/CUDA filters, ONNX Runtime GPU support, Dolby Vision and AMF improvements.
Download: ffmpeg.org/download.html#rel…
Michael Niedermayer retweeted
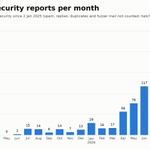
Over 100 security-report emails received in September already - and we’re only halfway through the month.
The chart is noisy, but the security workload has grown substantially.
If you’re a large company relying on FFmpeg please donate
ffmpeg.org/donations.html


The most retarded thing Ive read recently is people arguing as if someone could stop evolution
Agentic coding will keep improving, anime girls will keep looking more realistic, and ChatGPT will keep finding better ways to fill my screen with general text that doesnt answer my ?
Dont argue with claude. I did that and the result was that another agent spend 3h trying to remove bits of that argument that it put in random comments and commit messages. And after 3h i told it to use git filter

Comparing GPT-5.4 vs GPT-5.6-terra (both same price) for our review combiner GPT-5.6-terra wins, full analysis: code.ffmpeg.org/michaelni/Fa…

Michael Niedermayer retweeted
New FFmpeg point releases: 8.1.2, 8.0.3, 7.1.5, 6.1.6, 5.1.10 and 4.4.8 are now available.
ffmpeg.org/download.html
Includes fixes for issues reported to ffmpeg-security
Making point releases in 2026 – the real process:
1️⃣ Backport everything "manually"
2️⃣ Test manually
3️⃣ Run 2 passes with multiple AI sub-agents scanning for missed backports
🧵
4️⃣ Adapt and test the non trivial backports
5️⃣ Deal with all the weird and wonderful unexpected things that show up
6️⃣ Try really hard not to look at the security reports that accumulated in the meantime
Spent too much of yesterday fighting persistent 500 errors on vector_stores.files.list.
Took way longer than it should have because there's a ton of misleading info online. Here's the actual workaround that worked for me 🧵
You can bisect in a few different ways.
One is
Take the poisoned vector store → split it into two new vector stores, each with roughly half the files → repeat recursively until you isolate the single problematic file.
🥁 Drumroll… @OpenAI
The file that poisioned the vector store was fontawesome-webfont.svg. (its part of ffmpeg web git)
Interesting detail: older vector stores that already contain fontawesome-webfont.svg are completely fine.