
@mentality_aces
Account based inUnited States
About this account
- Account based in
- United States
- Connected via
- United States Android App
Account-level information from X, not a live location or the device used for a specific post.
Joined July 2009
- Tweets3.1K
- Following2.8K
- Followers450
- Likes776




Mentality_aces retweeted

Here's our plan for quantum-safe, unlinkable, rotating taddrs. Possible with Zcash, today.
While others are worrying about the viability of rotating transparent addresses, we're already solving linkability.
zakura.com/engineering/trans…

Mentality_aces retweeted

They labeled Orchard "Shielded Legacy."
We agree. Ironwood is the shielded pool now, and Brave Wallet desktop stable can move the notes. Update and cross the turnstile. $ZEC

Zcash Ironwood support is now enabled by default in Brave Wallet on desktop (Stable channel) 🛡️
In Brave Wallet you can now:
- Send $ZEC to, from, and between Ironwood shielded addresses
- Move your Orchard funds into Ironwood
- See your balances separately: Orchard shows as "Shielded Legacy," Ironwood as "Shielded"
Everyone using @Brave on desktop: please update to the latest version and give it a try.
Report bugs: github.com/brave/brave-brows…
@Zcash @ShieldedLabs @zooko

Zcash mentioned.
$ZEC

I don't recommend anyone scramble to move their funds to new wallets today. But we should take the risks to cryptography from AI-accelerated math seriously, and minimize our exposure to not just quantum-vulnerable cryptography, but also potentially AI-vulnerable cryptography.
The core new area of risk from this viewpoint is, unfortunately, ML-DSA / FHE / lattices.
(and it's also another reason, along with quantum, why ECDSA might fall even faster than expected, hence the "fresh address" recommendation)
So far most people have been in the mode of thinking "elliptic curves broken, hashes safe, lattices safe". But there is a good chance that the concrete security of lattices will take serious hits from the next two years of AI math.
The basic threat model is: factoring is something that naively takes 2^(n/2) time, but over decades smart people have found and optimized number field sieves, and degraded that to 2^O(n^(1/3)), which is why RSA keys and signatures need to be ~400 bytes (and not 64 bytes). What if there are skeletons in the closet like that, both for elliptic curves and lattices, that we are simply not smart enough to discover - but bots soon will be?
This is a major part of the reason why for the past year ethereum's lean roadmap has been going in the "hash-only" direction: no lattices, no ML-DSA, no Falcon, no lattice-based commitments inside ZK proofs, etc. Signatures in lean ethereum are all hash-based, either WOTS or SPHINCS-.
For signatures and proofs, we already know how to go hash-only. The bigger challenge is for *public-key encryption* - and this goes far beyond blockchains. Secure communication, anonymizing protocols, lots of things need public-key encryption.
And unfortunately there are long-standing mathematical theorems showing why public-key encryption cannot be done with hashes alone. You have to have some kind of trapdoor object that has at least one form of usable "structure" - either group theory (incl. isogenies) or lattices or code-based or potentially in the future even more newfangled and spooky things (local mixing?). But for anything that has structure, you should assume that AI will make at least some progress in breaking that structure. Here, one reasonable inference is that if you want to make something plausibly long-term secure, multiply the key sizes by 10.
To me that's a very plausible world and something not at all extreme to predict. If AI will bring us 50 years of math in 2 years, then that 50 years of math may very plausibly include a "naive factoring -> GNFS" level of improvement to our ability to break lattices. In that world, lattices will still exist, but they will have to be significantly bigger to guarantee the same level of safety.
And at those new larger sizes, hash-based constructions will beat lattice-based constructions on concrete efficiency in every use case where hash-based constructions are possible at all.
Theoretically, of course it's possible that hashes are broken too (eg. P = NP would imply that). But I think P = NP is very unlikely. And intuitively, it's much more likely that a mathematical object has exactly no exploitable structure (like hashes are intended to), than that a mathematical object has exactly ~3 forms of exploitable structure (for elliptic curves: associativity, Schoof, pairings) and not some secret fourth form of structure we have not yet discovered that greatly degrades its security (for elliptic curves, ECDLP and pairing security). Similar for LWE, SVP, RLWE and the zoo of lattice problems.
For this reason, we do not yet see any reason to worry and start padding the byte size of hashes (if we start to worry more, we would pad the round count first before doing anything to the byte size).
Concrete TLDR, my own personal views:
* Hash-based > lattice-based, in those situations where hash-based is possible at all
* For anything lattice-based, be much more paranoid on param sizes. Remember that blockchains are only a small portion of the cryptography story; this point goes far beyond blockchains and applies to eg. access to websites, secure messaging, Tor / VPNs ...
* For privacy protocols, strongly favor NOT putting encrypted notes onchain. Instead, send them offchain through some third-party mechanism.
* If it's not difficult for you, keeping your funds in addresses which have not yet been used to make a transaction is a good idea. If it's easy for you, do it. **But be careful about migrations; I personally have lost more money in botched migrations than I have lost in all hacks combined**.
* For multisig wallets, doing confirmations offchain is better than onchain, because this way the signatures of signer wallets do not get exposed to the public, so if ECDSA falls to AI much faster than expected, at least the multisig "gracefully degrades" to a 1-of-1 where the 1 is whoever was gathering the signatures - a much better place to be than "anyone can take the money"
firefly.social/post/x/210783…

Mentality_aces retweeted

🚨JUST IN: Winklevoss group files for a spot Zcash ETF under the ticker WINK.
The proposed Nasdaq fund would hold $ZEC directly, use Gemini as custodian and charge a 0.25% fee.
Winklevoss Capital has also indicated interest in buying up to $100 MILLION of shares.
That makes Winklevoss the third issuer chasing the US Zcash ETF market after Grayscale and Bitwise.
Grayscale’s ZEC ETF already holds nearly $890 MILLION in assets after launching in August.
The Zcash ETF race is getting crowded fast.


Mentality_aces retweeted
NU7 activated on Zcash's Testnet early.
zakura.com/nu7/

Mentality_aces retweeted

🥹 Gerson Rodrigues’ heartfelt post on IG:
“From a human to an extraterrestrial:
I faced you 7 times, Cristiano Ronaldo. Seven times I looked across the pitch and saw something that wasn’t human. You moved like an extraterrestrial, a being of pure intention and unstoppable power. You don’t belong to this world.
Every collision with you taught me what’s possible when you transcend human limits.
But here’s what breaks my heart: an extraterrestrial who put Portugal on the map, who made the world know our flag, who was the heartbeat of our nation — your country should respect you differently, even as the end draws near. You deserve that honor.
When I tell people I’m from Portugal, they ask about Ronaldo. And now? It hurts. Because you were more than a player. You were Portugal’s voice to the world.
That’s what saddens me most.”

Mentality_aces retweeted

Real Madrid to completely uproot major transfer policy to satisfy Jose Mourinho after mixed start to second spell
thesun.co.uk/sport/40494611/…

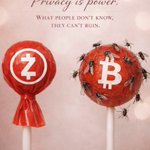
thats the movement we are all experiencing lately... Bitcoin into zcash. Rotation. bitcoin:native zcash:native

You dont need bitcoin dominance in order to prove zcash value.
Iphone hadn't needed Nokia dominance in order to prove it has been the best phone
$ZEC $BTC

I’m of the mind that if BTC does poorly, ever, or “gets flipped” or anything like that, the industry is permanently cooked forever. No matter what coin you’re in, you want BTC dominance. Even if you don’t hold BTC.
That being said:
Even as someone that doesn’t have a TON of ZEC exposure, the way BTC maxis are attacking it amidst nascent yet undeniably durable strength.. it reminds me a *lot* of the way eth maxis had solana living rent free in their heads all of 2023 (even when sol was at its rock bottom lows)
Study the behavior of people that feel threatened and insecure.




Mentality_aces retweeted

If I was doing anything seriously privacy-demanding I'd probably go for Zcash first.
Mentality_aces retweeted

One morning you wake up. Your agent on phone give you alert: “hello gay white man. Last night 500 agent look through your tax record. They be find 1,200 error in your tax filing. Tax workers now come take you jail.”
For me morning be so different. My phone give me alert: “ Hello great wisdom great honor Wei Wu. Your money in zcash:native . So no one can see anything so no problem at all.”
You understand my parable?
Be wisdom. Invest in your future. Be a man. Do right thing.


