



Marc Dov retweeted

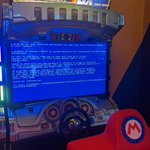
CrowdStrike accepting the @PwnieAwards for “most epic fail” at @defcon. Class act.
Marc Dov retweeted

My talk at the FIRSTCON24 is online
Unveiling Active Directory Secrets: Uncommon Tricks for Enhanced Security
Slides:
raw.githubusercontent.com/vl…
Videos:
youtube.com/watch?v=UE7c8IvU…

Marc Dov retweeted

un très intéressant travail de visualisation pour découvrir quels sont les codes PIN les plus et les moins courants
informationisbeautiful.net/v…

Marc Dov retweeted

I've been reverse engineering the xz backdoor this weekend and have documented the payload format and written a proof-of-concept exploit for the RCE. The payloads are signed with an ED448 key, so I patched my own key into the backdoor for testing. :-)
github.com/amlweems/xzbot



Marc Dov retweeted

Il y a 40 ans, le 24 janvier 1984, fut présenté le MacIntosh 128k par Steeve Jobs devant un public de 3000 personnes. Cet ordinateur représentera le premier succès commercial pour un appareil disposant d'une souris et d'une interface graphique #LaPetiteInfoDuJour


Marc Dov retweeted
David Mills, professeur et ingénieur informatique, est mort le 17 janvier dernier. On lui doit notamment le protocole NTP, la première implémentation du protocole FTP ainsi que le protocole EGP qui précéda le BGP

Marc Dov retweeted

FAI: Quelles solutions mettre en place pour partager l'#IPv4 entre plusieurs clients ?
François Bouju explique le choix de @bouyguestelecom d'utiliser MAP-T (v6 only) et non du Carrier-grade NAT.
Les clients qui ont besoin d'IPv4 dédiée ne sont pas migrés.
youtube.com/watch?v=6RFsA1vs…
Marc Dov retweeted

Is remote code execution in UEFI firmware possible?
Yes it is.
Meet #PixieFAIL: 9 vulnerabilities in the IPv6 stack of EDK II, the open source UEFI implementation used by billions of computers.
Full details by @fdfalcon and @4Dgifts in our new blog post:
blog.quarkslab.com/pixiefail…

ALT Pixies are said to reward consideration and punish neglect of server maintenance on the part of larger humans, they bring blessings to those who are fond of timely patching.

Marc Dov retweeted

Very cool > Mewz: a WASI-compatible unikernel github.com/mewz-project/mewz #webassembly

Marc Dov retweeted

Je n'allais quand même pas terminer l'année avec un article sur ma Livebox...
Parlons de Firecracker, un outil développé par AWS pour gérer Lambda et Fargate à l'aide de MicroVMs.
Bonne lecture, et bonnes fêtes de fin d'année
une-tasse-de.cafe/blog/firec…

Très bon article !

Des années que j'utilise Docker sans jamais connaître les mécanismes derrières.
Dans cet article, je vous montre que les conteneurs ne sont pas créés par les petites fées.
J'en profite aussi pour vous rappeler que nous sommes en LIVE ce soir 😄
une-tasse-de.cafe/blog/conte…


Marc Dov retweeted

Trippy : un outil combinant traceroute et ping, conçu pour aider les adminsys à résoudre les problèmes de réseau.
Il prend en charge les protocoles ICMP, UDP, TCP et les versions IPv4 et IPv6.
github.com/fujiapple852/trip…
Marc Dov retweeted

You all know this had to happen 😜 Doom on the @kalilinux NetHunter TicWatch Pro 3 @Mobvoi_Official @kimocoder @timinbrum
Marc Dov retweeted

🔍Question of the day: Where to find SSRF Issues?
Many overlook testing for SSRF vulnerabilities, thinking they're complex and beyond their capabilities. 💻💔 However, these issues can lead to bounties ranging from $1000 to $15000, depending on the Impact.
These are the top 5 obvious features I look for in a target app to find SSRF Issues:
1️⃣ Export to PDF - Does your target app support generating PDFs? 📄 Try injecting HTML into the content that is used for generating that PDF. If vulnerable to HTML injection, you might strike gold by injecting HTML/JS.💰
2️⃣ Integrations - If your target app supports web hook Integration feature, replace the URL with your Burp Collab and wait for a hit. 🔄
3️⃣ Import via link Feature - Does your target app support importing files or websites via a link? 📥 Specify your attacker Burp Collab and check for a hit, especially when uploading profile pictures or media through a library.
4️⃣ Host Header - Test for Routing-based SSRF by supplying your Collaborator server domain in the Host header. If you receive a DNS lookup from the target server, you might be able to route requests to arbitrary domains🌐
5️⃣ File Upload - Does your target app support uploading files? 📂 Try uploading an HTML file; if rendered and executed on the server-side, you might strike gold. No luck? Try an SVG with SSRF payload. If that fails, move on to the next!
None of the above methods worked? Don't worry; we have more tricks up our sleeves, and we'll be sharing them soon! 🧙♂️
Takeaways: Note these features, and if you encounter them in your target app, don't forget to test for SSRF Issues. Who doesn't love some free money while securing the planet? Stay tuned for more! 💸🌍
#cybersecurity #bugbountytips #securitytips #bugcrowd #hackerone #tips #bounty

Marc Dov retweeted

Kaspersky discovered that a very stealthy malware infected dozens of their Apple devices 😱
After months of work, they managed to get the infection vector, four 0-days and the implant itself. Congrats!! 🍾
securelist.com/operation-tri…