Maltrail got a fairly brutal rewrite this summer.
Reporting UI rewritten from scratch, server heavily reworked/hardened, and the packet sensor rewritten from Python to Rust.
Substantially lower packet-processing cost, much better testing/deployment, and lots of bugs fixed.
Maltrail retweeted
Miroslav Stampar shares insights to Maltrail system that’s designed to detect malicious traffic by identifying potential threats and monitors network traffic. A great case study from Croatia! #CyberWeek2024
Maltrail retweeted
The SIE Europe pDNS system is now getting active feed with extended malware feeds per 15/min.
Thanks @maltrail for the feeds (nice work)
You can find our Wiki pages at github.com/stamparm/maltrail… with FAQs, trail classes, UI tips and tricks, etc.
With the latest version (0.29.24), we added a new feed "statics" that will keep your sensor's static trails up to date, even if you don't frequently update the codebase
Challenge. Try (free and open-source) Maltrail and compare malware detection results with any commercial network product you use in your corporate network. Pass results to your management and your colleagues.
p.s. we already know the results, but have to play neutral :D
Protip for UI: press left and/or right keyboard button for easier and faster changing of a current page
Maltrail retweeted
If you are a CERT member, I would like to point you to the maltrail.github.io/ and its demo site located at maltraildemo.github.io/. @maltrail is free and open-source network sensor system, where we spend tons of time filling it with latest network IoCs
With latest revision, once logged in into the UI, you can use "?refresh=N" to force refresh of data every N seconds (e.g. ?refresh=60)
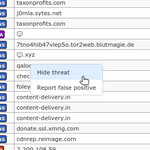
Two new UI features: A) "Hide threat" - threat details will be hidden in future browser reports and B) "Report false positive" - threat details will be sent to us for additional analysis
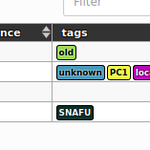
Tags are patched now. So, you can add searchable tags (i.e. attributes) for each recognized threat, which will be stored inside your local web browser storage for future usage
If you want to integrate Maltrail events into your existing SIEM platform, from this moment you can choose between CEF (option SYSLOG_SERVER) and JSON (option LOGSTASH_SERVER) formats
How to get condensed one-line report for each network threat instead of thousands of non-coherent events inside a SIEM? Use Maltrail