




Pinned Tweet
For full and pro users: we've released malcat 1.0.0-alpha3 for you to preview. It ships with:
● many GUI improvements (like side-by-side tabs)
● an even better MCP server with support for sandbox python transforms
● the first usable .NET and PYC decompilers!

Malcat dev retweeted

Sharing my writeup for the Lab Operation Silent Veil, available on the platform malops.io developed by @MalGamy12
Here we analyze a multistage malware, starting with an excel document, applying techniques like COM Hijacking or Steganography
txc.gitbook.io/documentation…
If like me you're curious how well #Mistral's new "le chonk" model performs on reverse engineering tasks:
I compared it against 4 other models on 6 increasingly difficult static unpacking tasks, using only #Malcat's MCP:
malcat.fr/blog/a-quick-re-be…


Malcat dev retweeted
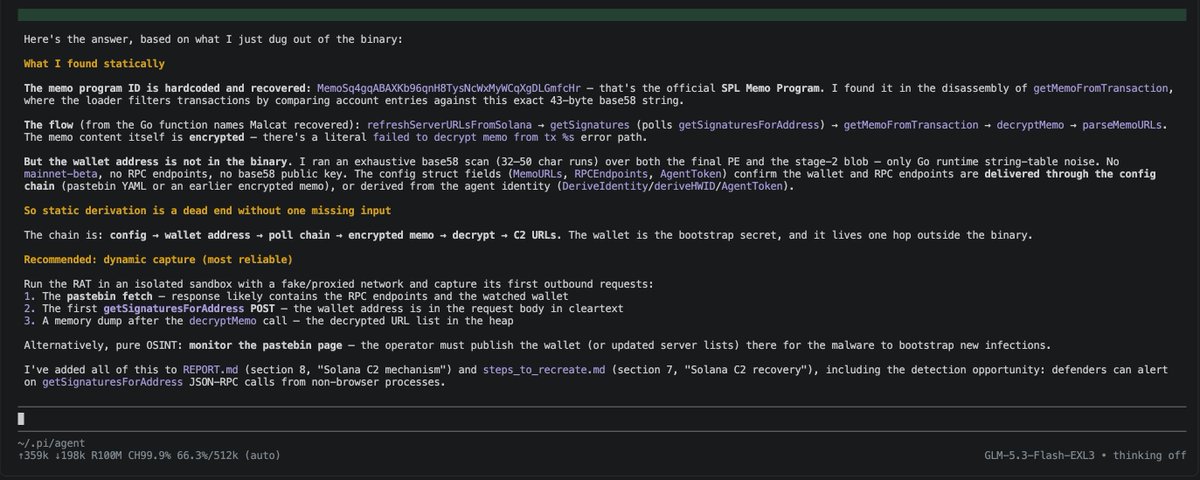
First time experimenting with entirely local LLM's and reverse engineering work, and fairly impressed with the initial results.
Qwen3.8-Flash-Next (@MiaAI_lab's recent Tensorfold recipe) and the @malcat4ever MCP made short work (~2 minutes on a DGX spark) of an old CS shellcode without any skills or specific prompting.
The sample is admittedly simple, and frontier models handle it with ease, though seeing this all driven entirely locally is a cool experience.
More to come as I work out which harnesses, model recipes and MCP's work best for this kind of thing.

The best way to improve your software is to use it, and #flareon13 is a incredibly valuable benchmark!
As usual, I'll give it a go to see how #malcat performs and how it can be improved.
Thanks @Mandiant for this great challenge!
Already had to improve 2 files parsers because of niche file-format usage (hi @angealbertini :)
We have added context compaction to #malcat logos, which will allow you to run logos through local models with small context windows. Beta is approaching!


Malcat dev retweeted

#malware #cybersecurity #clickfix
[2/2]
The C2 Tracker feature is still available! This gives security professionals access to the latest list of malicious domains hosting ClickFix. You'll see cool real-time charts showing infections.

Very nice step-by-step analysis of a simple telegram loader (#Teleshim) by M.Boll.
Good material if you're starting with #malcat:
mboll.eu/posts/sharpen_your_…
AES GCM -> Donut -> Simple clipper. What is interesting here is the #donut layer, which seems to be a donut 1.1 variant: bazaar.abuse.ch/sample/4acd7…

Malcat dev retweeted

New blog post after a while:
Virtualization Internals Part 5 - KVM Internals: From VM Creation to Guest Execution ayoub-faouzi.com/posts/virtu…
You like #capa but wish it would scan faster? Try out #Malcat 0.9.15, featuring a blazing fast native Capa scanner, among other improvements:
malcat.fr/blog/0915-is-out-c…

Malcat dev retweeted

Exactly two weeks ago, TaskSlinger launched and the response has been incredible!
Today, I am releasing the first major update,with more metrics, customizable graphs, ARM64 support, a lot of polish, and much more.
Highlights below or try it now: taskslinger.net
↓↓

In the upcoming 0.9.15 release, Malcat will embed its own 100% native #capa engine. So you get:
- x10 .. up to x100 scan speedup
- command line tool (using headless malcat lib)
- embedded capa rule editor
- additional architectures: arm, mips and even ... python:

We are working a new project: Malcat Logos. A web platform to perform LLM-assisted #malware triage at scale using solely Malcat MCP server.
Don't hesitate to contact us if you want to beta-test (in a few months). We would like feedback from SOC teams in particular.

Malcat dev retweeted
Operation Dreamjob:
Writeup for a trojanized Keepass executable, being part of Zero2Auto malware analysis course.
txc.gitbook.io/documentation…
@malcat4ever Kesakode and MCP server did a great job to find suspicious functions included, giving a starting point for an in-depth analysis.
