

Building worlds where hackers play. 🏴 Head of CTFs @hackthebox_eu | Global cyber competitions + enterprise training | he/him
Thessaloniki, Greece
Joined July 2016
- Tweets5.1K
- Following2.6K
- Followers1.2K
- Likes5.4K


Pinned Tweet
Who knew you could suffer eternal damnation by eating some space shrimps? 🦐 20 hours and counting ⏰.
You still have time to hack your way in at hackthebox.eu/#join and claim the first🩸for my #Web challenge #ImageTok.
#HackTheBox #CyberSecurity #CyberSecurityTraining

makelaris retweeted

Spent a week testing AI for vulnerability research. 14 confirmed bugs in 20 min on one target. 5% hit rate on a hardened one. Same AI, same setup. 4 approaches, what worked, what failed, why target selection matters more than model sophistication. xclow3n.github.io/post/7

makelaris retweeted

I am releasing a new toolkit I built for IIS-based lateral movement and code execution within IIS worker pool process's memory.
Phantom ASPX Loader & PhantomLink -- a two-part toolkit for reflectively loading native DLLs into IIS w3wp.exe worker processes via ASPX.
github.com/zux0x3a/Phantom/t…
makelaris retweeted
Discovered 3 HTTP request smuggling vulnerabilities and 1 cache poisoning vulnerability in Cloudflare’s Pingora reverse proxy, all exploitable under the default configuration. These issues resulted in 2 Critical CVEs and 1 High-severity CVE.
xclow3n.github.io/post/6
makelaris retweeted
🚨Ethereum Developers: you can now install your first AI Auditor in 1 minute - fully autonomous, available 24/7, with multiple sub-agent helpers. Open Source.
FREE to use (with your AI model) and already finding vulnerabilities in smart contracts. Link below🫡

makelaris retweeted

New blog: Hooked on Linux — Rootkit Taxonomy, Hooking Techniques and Tradecraft
Part 1 of our Linux rootkit series exploring kernel & userland rootkits and the hooking techniques they use (syscall/function hooks, ftrace, eBPF, inline patching).
🔗elastic.co/security-labs/lin…

makelaris retweeted

Turning Almost Nothing into a Supply Chain Compromise of Angular with GitHub Actions Cache Poisoning
adnanthekhan.com/posts/angul…
#BugBounty

makelaris retweeted
Recently my RE workflow moved into sandboxed VMs where agents have full control over the environment. I needed an MCP server that runs headless in the same sandbox and exposes way more of the #BinaryNinja API than others.
Here's the release: github.com/mrphrazer/binary-…

makelaris retweeted
WebSockets are not yet affected by Local Network Access permission in Chrome.
Check out this blog post from my colleague @GrumpinouT!
aikido.dev/blog/storybooks-w…

makelaris retweeted

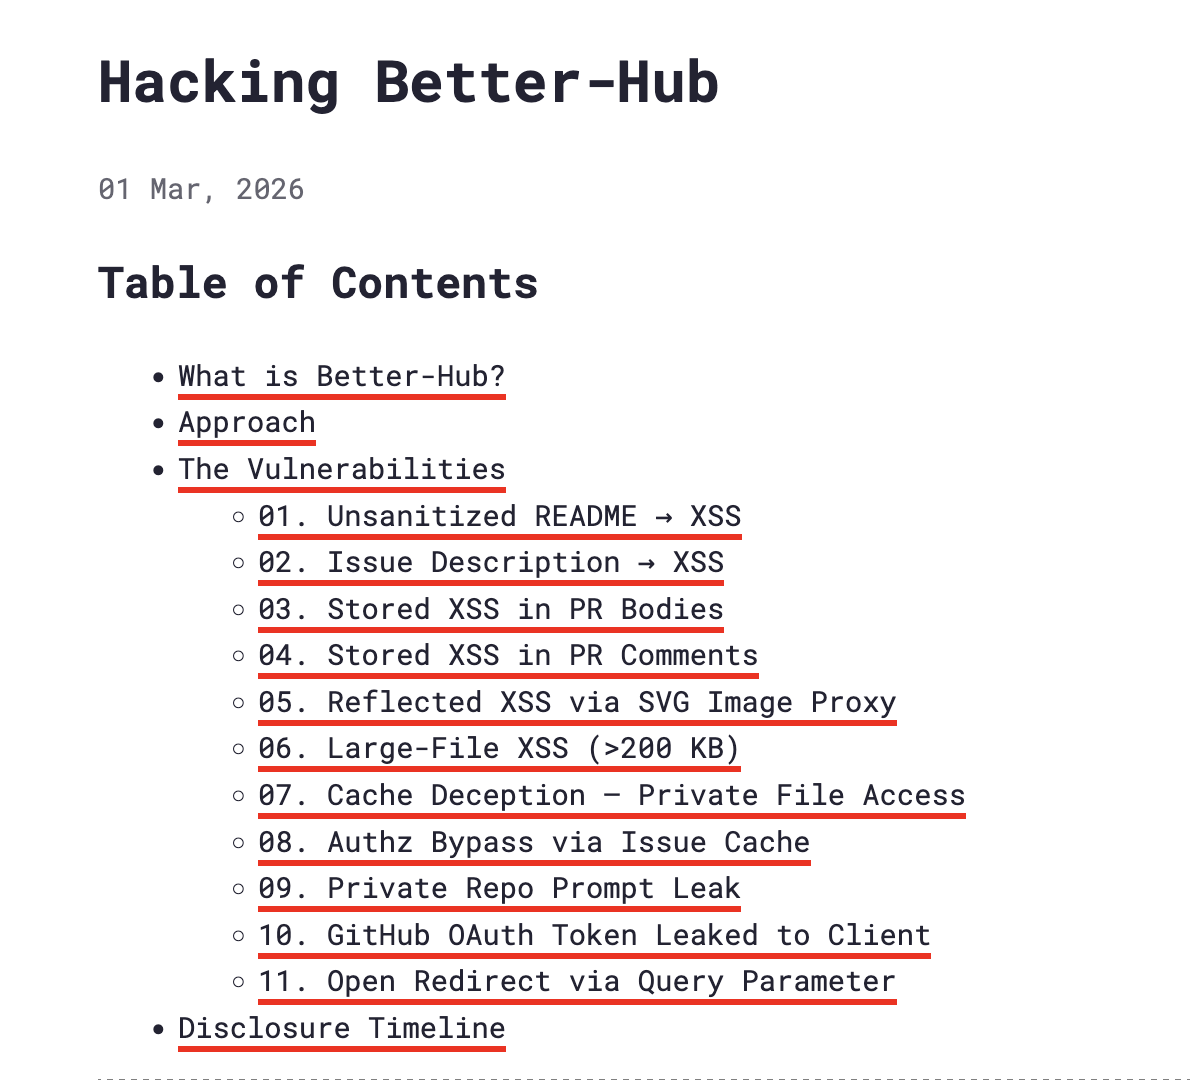
A bunch of security issues I reported to better-hub. Disclosing as these should have been fixed now.
Thanks for quick fixes @bekacru
makelaris retweeted

Apache FOP + Ghostscript = 💥
Bypassed PostScript escaping using non-breaking spaces (\xa0) to inject commands. Chained with CVE-2025-46646 for Windows RCE. @truffzor
Apache won't fix it - just updating the docs 🤷
Full technical details @sigabrt9 offsec.almond.consulting/byp…
makelaris retweeted
New write-up!
Bypassing egress filtering in BullFrog GitHub Action (using query pipelining feature of DNS over TCP)
(link in comment)

makelaris retweeted

We disclosed a critical unauthenticated RCE chain in mcp-atlassian (4M+ downloads).
CVE-2026-27826 - SSRF via Atlassian URL headers
CVE-2026-27825 - Arbitrary file write → RCE
Fixed in 0.17.0.
Full breakdown 👇
blog.pluto.security/p/mcpwnf…

makelaris retweeted
Second write-up of the day!
sudo restriction bypass via Docker Group in BullFrog GitHub Action
devansh.bearblog.dev/sudo-by…

makelaris retweeted

Why macOS AVs shouldn’t trust PIDs 😄🍏 - new post by @Coiffeur0x90 Intego X9: XPC validation falls back to PID → PID reuse + posix_spawn() shenanigans 😏 ⇒ confused deputy / privileged methods abused 🤡🧨 Lesson: PID ≠ identity. blog.quarkslab.com/intego_lp…

makelaris retweeted
Just a few days later, there's the next blog post for @AikidoSecurity! Another framework-level vulnerability this time affecting Astro, resulting in SSRF if an unvalidated connection can be made to the webserver.
Read the details here:
aikido.dev/blog/astro-full-r…

makelaris retweeted

Sometimes you spot a sink and know it's vulnerable, but proving it is a challenge. @SLCyberSec's team broke through layers of crypto to reach a pre-auth deserialization sink in OpenText Directory Services. Breaking the encryption was a journey. slcyber.io/research-center/a…

makelaris retweeted

Pwning TRUfusion Enterprise again: chaining a pre-auth SSRF (CVE-2025-32355), a default password, and a path traversal (CVE-2025-59793) to gain RCE.
#security
rcesecurity.com/2026/02/when…


makelaris retweeted

I was looking a bit onto why OPENROWSET is able to read privileged files (like the root flag on Signed @hackthebox_eu) when using Silver tickets on MSSQL. Turns out you can get SYSTEM access without potatoes by recovering the full token. vuln.dev/silver-ticket-mssql…