

Vulnerability Research & Exploit Development
Joined September 2022
- Tweets166
- Following413
- Followers1.4K
- Likes1K




VsockDrop: unprivileged Linux kernel LPE in the io_uring/vsock zerocopy path, no user namespaces needed. Bug affects Linux 6.7 -> 7.0.10, fixed in 7.0.11.
PoC video: Ubuntu 26.04 LTS on bare metal.
Exploit + mini write-up here:
github.com/MaherAzzouzi/vsoc…

Me: here is a stable OOB read/write vulnerability.
: duplicate of CVE-2026-XXXX.
Me: I reported CVE-2026-XXXX too. These are different bugs: different root causes and different vulnerability classes (UAF vs OOB r/w). I don’t think this is a duplicate.
: this ticket was closed because it was not reproducible on the latest branch used in our products.
Me: I can reliably reproduce it on the latest public iOS 26.5 beta. I also provided a video PoC.
: thank you for the additional info.
A few weeks later: we reproduced the issue and are planning to address it in Summer 2026... ¯\_(ツ)_/¯

Qualcomm mishandled my last report at first, but in the end they acknowledged the issue and paid the bounty. I reported a FastRPC UAF. Qualcomm said that they know about it but due to some internal tooling problems, the fix didn't reach all release branches for over a year.

Another AMDGPU bug I reported last year has been fixed: CVE-2025-54517 (CVSS 8.5).
One ioctl -> kernel compromise on AMD Instinct / Radeon PRO virtualization stacks.
May 2026 security bulletin:
amd.com/en/resources/product…
Apple fixed two vulnerabilities I reported affecting Safari/WebKit: CVE-2026-28953 and CVE-2026-28901. Sometimes mitigations can create new attack surfaces.
support.apple.com/en-us/1271…

Technical details for a kernel UAF vulnerability I reported earlier (analysis + PoC).
kernel.googlesource.com/pub/…
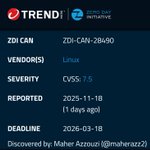
Reported ZDI-CAN-28490 (CVSS 7.5). A Linux kernel bug in the ETS qdisc within the packet scheduler subsystem.
A logic flaw + race can leave a freed qdisc on an internal list, letting an unprivileged user trigger a UAF and gain kernel-level privilege escalation.


No more POC tickets? @POC_Crew. Wanted to visit this year’s edition, it seems im a bit late
AMD August 2025 Security Bulletins (AMD-SB-6018 and AMD-SB-5007) feature my discovery CVE-2024-36342, a heap overflow in the @AMD GPU driver, rated with the highest severity in AMD-SB-5007 and listed among the most severe vulnerabilities in AMD-SB-6018.
amd.com/en/resources/product…

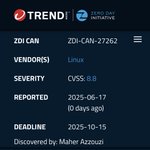
ZDI-CAN-27262 is a Linux kernel 0-day I reported recently that allows unprivileged users to escalate privileges to root.
The vulnerability is a race condition leading to a UAF in the kmalloc-196 cache. It was introduced in v4.2-rc1 and has been present in the kernel for 10 years.

Maher Azzouzi retweeted

I wrote an LPE for CVE-2014-3153 AKA Towelroot, a bug in the Linux Kernel that was used to root Android devices earlier. The original exploit is closed source and protected against reverse engineering.
PoC + mini write-up here:
git.io/Jnazk
Maher Azzouzi retweeted
I wrote an LPE exploit for CVE-2017-11176 for Linux Kernel version 4.8.11, I managed to bypass SMEP and SMAP (by stack pivoting inside the kernel and ROP).
The vulnerability is a UAF, and the patch is only 1 line of code.
Exploit and Write-up + Refs here:
git.io/J0p8v
- Heap overflow in the latest AMDGPU drivers. CVSS score: 8.8, bounty: $5k.
- 7 Android kernel vulnerabilities.
It wasn’t a good idea to keep these bugs documented without reporting them for three months — one of them turned out to be a duplicate.


CVE-2024-26926 Binder n-day analysis.
It is labeled EoP in Android Security Bulletin (Is it really exploitable?)
github.com/MaherAzzouzi/Linu…

