
@AlmondOffSec but mostly shilling for #pywerview
Joined March 2022
- Tweets272
- Following93
- Followers798
- Likes382





Pinned Tweet
Choose your poison
🦋 bsky.app/profile/lowercasedr…
🐘 mastodon.social/@drm
(still posting here too)
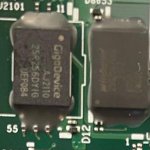
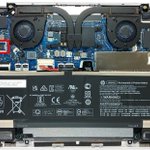
It’s the first time I see some resin (epoxy?) on flash pins that prevents SPI sniffing (and thus VMK dumping too) 😮. Can it be removed easily? Model: Lenovo X1 Gen 9 @en4rab @NoobieDog @ghidraninja @pascal_gujer


drm retweeted

None of this exists without the original research and tooling. 🙏 Massive thanks to @lowercase_drm and @AlmondOffSec for PassTheCert, this Rust port stands entirely on their work: github.com/AlmondOffSec/Pass…

drm retweeted

NetNTLMv1 is dead. Long live NetNTLMv1. 🌈
Today we're releasing NTLMRain: recovering NT hashes from NetNTLMv1 responses.
🌐 Browser-based cracking
⌨️ Cross-platform CLI with GPU/CPU support
💾 Searchable tables that fit on a 4 TB disk
Read the blog: outflank.nl/blog/2026/09/08/…

You can know dump TDO with secretsdump dot py, thanks to Goultarde 🥳


Are one-way trusts really one way? @lowercase_drm sums up how the TDO password lets you turn a one-way AD forest trust into bidirectional access, and releases a new tool to remotely extract these secrets.
offsec.almond.consulting/tru…

drm retweeted
I have suspected the klist.exe could be used to dump local tickets but never had time to check that out correctly. This guy did and explains it very well! Only requires local admin rights, no system, to dump all TGT's on the computer
jakeotte.com/posts/klist-rev…

10 years ago, my colleague Yannick published pywerview. I was an early adopter and later became an official co-maintainer. I still use it on every pentest. Nowadays, a project like that could probably be vibe-coded in no time by burning tokens, but it was a f* great adventure!


(near) Instant dumping of the Bitlocker VMK using @SipeedIO #SLogic16U3 and #ngscopeclient 🥰. Full disclosure: i know nothing about C++, filter was fully vibe coded (with a Claude free plan)

drm retweeted
Padding Oracle in MS-BKRP (BackuprKey RPC)
“decrypt DPAPI v2/v3 domain backup
blobs via distinguishable error codes on the DC's BackuprKey endpoint.”
You need the masterkey in users roaming dir: Roaming\Microsoft\Protect\<SID>\<GUID>
Creds: Bad-Jubies
github.com/Bad-Jubies/Exploi…

drm retweeted

github.com/NoobieDog/TPM-Sni… Continues to grow!
Loads more laptops added to the repo that are extractable!
Dell Lattitude 5430 and 5440!
@lowercase_drm @en4rab

Please, be advised that someone is using a forked repo of my KingCastle python script to spread LUA malware. What a time to be alive.
User: Ramdhankola Repo: KingCastle
🌻


Asked Claude to code a small site for the @NoobieDog repo about TPM sniffing. It was a fun exercice (even with a free tier claude account haha).
vmk.lol

drm retweeted

In our latest post, researcher @craigsblackie documents attacks against the Dell UEFI firmware that enable DMA attacks against TPM-only bitlockered devices mdsec.co.uk/2026/03/disablin…
