





Pinned Tweet
I began looking into browser security issues again in 2026 and while reviewing extension permission APIs, I noticed that the default declarativeNetRequest API (which only requires permission to block content on all pages) can be leveraged into a side-channel attack.
This permission ends up allowing an extension to infer the full URL of open tabs without requesting the chrome.tabs permission, and it can also leak the full URL of cross-origin redirects.
Unfortunately, fixing this issue has been deemed unrealistic by Chrome, and the risk has been accepted, so it is worth keeping this in mind when granting content-blocking permissions to browser extensions.
The complete public report can be found at issues.chromium.org/issues/4….
Luan Herrera retweeted

‿⊱⊱༒༻༻༻༻⛧༺༺༺༺༒⊰⊰
‿︵‧˚⊹ CHAMADA DE ARTIGOS ⊹˚‧︵‿
‿⊱⊱༒༻༻༻༻⛧༺༺༺༺༒⊰⊰
༺༻༺༻ DATA FINAL ༺༻༺༻
༺༻༺༻ 13/11 ༺༻༺༻
༺༻༺ [email protected] ༻༺༻
‿⊱⊱༒༻༻༻༻⛧༺༺༺༺༒⊰⊰

Luan Herrera retweeted

On July 25, we hacked OpenAI.
Two bugs let us take over ChatGPT/Codex accounts of OpenAI employees (+some unaffiliated users) and reach connected services: Outlook, Slack, GitHub, etc.
We proved it with a PR in OpenAI’s internal codebase . It took us <72h. 🧵

Luan Herrera retweeted

🚨🚨🚨🚨🚨🚨
From Padding Oracle to Shell: Unauthenticated RCE in Telerik UI for ASP[.]NET AJAX
tantosec.com/blog/2026/09/te…
The vulnerabilities described in this post were discovered, analysed, and exploited with some AI assistance, and a lot of old-fashioned human persistence.

Luan Herrera retweeted

Watch on YouTube: youtube.com/watch?v=nuJRZZV7…

Just published a union-based PoC for wp2shell :)
github.com/lbherrera/wp2shel…

Luan Herrera retweeted

I reported a pre auth RCE in Wordpress - it can be exploited with no preconditions, patch your instances!
slcyber.io/research-center/w…

Luan Herrera retweeted
[475265304][reward: $3000] NetError's page AutoReloader leads to multi-download blocker bypass
crbug.com/475265304
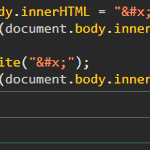
document.body.innerHTML = "&#x;"; console.log(document.body.innerHTML.length);
document.write("&#x;");
console.log(document.body.innerHTML.length);
🤔


Luan Herrera retweeted

Here we go. my DEF CON CTF writeup, a little different from the others. Also, thanks to Pwn de Queijo for letting me play with you guys.
davi1337.gitbook.io/public/d…


Luan Herrera retweeted
Posting a mini XSS challenge! Goal is to pop an alert. I believe this trick is not well known. Intended solution is chrome only. Thanks to @kevin_mizu for beta testing! Don't post solutions in the thread; DM only!
xss.hashkitten.io/xss1.html
Luan Herrera retweeted

I wrote a blog post about the recent copy(dot)fail bug, trying to explain some general concepts that I think were glossed over in the official article by @theori_io.
retr0.zip/blog/cve-2026-3143…

Luan Herrera retweeted

Introducing Hacktron Review: an AI security reviewer for your pull requests.
It understands your whole codebase, builds a threat model, takes your feedback, and catches exploitable vulnerabilities before they reach production.
Try for free: app.hacktron.ai
Luan Herrera retweeted
[422531206][reward: $5000] Intersection Observer v2 API fails to correctly determine target's visibility for dynamically changed z-indexes, enabling clickjacking against Google One Tap
crbug.com/422531206
Luan Herrera retweeted
I pointed claude opus at chrome and told it to build a full v8 exploit for discord.
A week of back-and-forth pulling it out of dead ends. 2.3B tokens. $2,283 in API costs, and it popped a shell.
hacktron.ai/blog/i-let-claud…

Luan Herrera retweeted
new tool
PEGA-PEGA
Multi-protocol request logger and catcher. Listens on 14 protocols, logs every incoming request, and displays them in a web dashboard and terminal UI.
github.com/caioluders/pega-p…

