




Pinned Tweet
Kovrr launches the AI Risk Governance Suite, empowering enterprises to unlock GenAI value by managing risk across the full lifecycle.
A connected platform for discovery, compliance, quantification & oversight.
🔗 kovrr.com/ai-governance
#AI #GenAI #RiskManagement #Governance

Never got around to reading the AIDF series? Now you can watch the scenarios play out instead.
First up is AIDF-001, where a finance-team analyst pastes classified numbers into a personal ChatGPT account to get through month-end close faster.
Watch four telemetry sources fire on it in under three seconds, then see what each one missed.
Network clocked a 41 kilobyte upload and none of its contents. Identity had the who, not the what. The extension saw the paste, nothing past the browser. The catalog knew the vendor, not who reached it.
See where the four of them overlap and month-end close turns into a regulatory obligation.
Watch the four signals fire >> kovrr.com/ai-interaction-dat…
#shadowai #aisecurity #aigovernance #ciso #cyberrisk
The hardest question in agentic security is three words long.
Who did this?
Network tools can confirm that an API call happened. They can't tie it to the agent behind it, or the human behind the agent. Not when agents run on ephemeral credentials that outnumber human identities by wide margins.
So the shadow agent stays an anonymous session, and the investigation stops there.
The AI Interaction Data Fabric establishes a behavioral baseline for every monitored agent, and ties each agent to the human who deployed it and the systems it touches. Attribution draws on volume, cadence and destination, read across sources instead of a single log.
Just 2 minutes on what that looks like, and what it takes to see it ⬇️
A filesystem tool was called with a path resolving to a credentials file. Fifty-three milliseconds later, four live credentials came back through the same boundary.
The network logged an already-open connection. The endpoint logged a program it had watched all day. The agent's own telemetry logged a successful 61-millisecond call.
Every system recorded the moment accurately. Every system recorded it as normal.
That is the shape of most AI exposure we see. Not a control that failed, but several controls that each reported the truth and none of which held the whole of it.
So we started a series about it.
𝙏𝙝𝙚 𝘼𝙄 𝙏𝙧𝙞𝙖𝙣𝙜𝙪𝙡𝙖𝙩𝙞𝙤𝙣 𝙎𝙚𝙧𝙞𝙚𝙨 takes one event apart per issue, follows it from start to finish, and shows how our AI Interaction Data Fabric reads across every connected source to catch what no source could alone.
hubs.li/Q04z-tqY0

How long does it take your team to turn a cyber risk quantification into a board-ready report?
With Report Builder in the Kovrr Reports Hub, it takes minutes, not days.
Pick a role based template (CEO, CFO, CISO and more), add live charts from your quantification, edit the data, match the colors to your brand, and export to PDF or PowerPoint.
Same quantification, a different report for every reader.
See it work on your own exposure in a live demo of the CRQ Platform >> kovrr.com/demo
#Dapper, the 2010 Google paper that gave the industry traces and spans, sampled one trace in 1,024.
Ample for catching a latency regression, because a regression recurs and the next sample catches it. As a record of who authorized a privileged action, the same rate leaves 99.9% missing, and the missing part is where the one event that mattered lives.
That gap is the subject of new Kovrr Research. Five production coding agents, instrumented and captured against a live OpenTelemetry collector on an identical task.
Part 1 covers the half that works. Four questions agent telemetry answers well today, including one that nothing else in your stack can touch.
The action boundary. The moment an agent stops reasoning and runs a command.
Network inspection sees TLS to a model endpoint, whether the agent went on to summarize a README or read a credentials file.
Endpoint detection sees a process that spawned a shell, which is what developer tools do all day. Identity sees a token that was already issued.
The distinguishing information is in the tool call, and the tool call exists in exactly one place.
Read Part 1 of 3: lnkd.in/dj6wpyTf
#AISecurity #OpenTelemetry #AIGovernance

Thousands of AI signals move through your company every day. A prompt here. An upload there. On their own, almost all of them look harmless. Mostly they are.
The risk lives in how they line up.
Kovrr is launching a new detection series. Every issue follows a single incident from start to finish and shows how our AI Interaction Data Fabric reads across every connected source to catch what no source could alone.
𝐈𝐬𝐬𝐮𝐞 𝐎𝐧𝐞 𝐢𝐬 𝐥𝐢𝐯𝐞: 𝘜𝘯𝘢𝘶𝘵𝘩𝘰𝘳𝘪𝘻𝘦𝘥 𝘊𝘩𝘢𝘵𝘎𝘗𝘛 𝘋𝘦𝘵𝘦𝘤𝘵𝘪𝘰𝘯, 𝘍𝘪𝘯𝘢𝘯𝘤𝘪𝘢𝘭 𝘋𝘢𝘵𝘢 𝘜𝘱𝘭𝘰𝘢𝘥 𝘗𝘳𝘦𝘷𝘦𝘯𝘵𝘪𝘰𝘯.
What each source saw on its own:
* Identity: a known user on a managed device
* Network: a small encrypted upload it couldn't read
* Browser: a paste in one tab
* Vendor catalog: a tool that trains on whatever it receives
Four fragments. One exposure. Not one of them worth an alert alone.
See how the fabric connected them 👇
kovrr.com/ai-interaction-dat…
𝐖𝐡𝐚𝐭 𝐢𝐭 𝐚𝐜𝐭𝐮𝐚𝐥𝐥𝐲 𝐭𝐚𝐤𝐞𝐬 𝐭𝐨 𝐛𝐮𝐢𝐥𝐝 𝐚 𝐝𝐮𝐫𝐚𝐛𝐥𝐞 𝐀𝐈 𝐠𝐨𝐯𝐞𝐫𝐧𝐚𝐧𝐜𝐞 𝐩𝐫𝐨𝐠𝐫𝐚𝐦, 𝐢𝐧 𝐜𝐚𝐬𝐞 𝐲𝐨𝐮 𝐦𝐢𝐬𝐬𝐞𝐝 𝐢𝐭:
✅ Only 36% of organizations have visibility into where their data is processed, trained, or inferred. AI governance starts with data governance, and data governance starts with knowing what you actually have.
✅ Most AI inventories are incomplete. Shadow AI is more widespread than leadership realizes, and surfacing it once doesn't solve it.
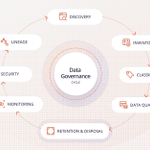
✅ Governance splits into two dimensions. Data-centric covers what goes into the model. System-centric covers how it behaves. Covering one leaves the other exposed.
✅ Integrity sits inside the CISO's mandate. Data quality sits with the business. That handoff is rarely documented.
✅ When the CISO, CIO, and COO all share ownership, no one owns it. The programs that work name a single coordinating owner with real authority.
✅ The most consequential failures happen in the seam between the two dimensions, because that's the one place no one is evaluating.
And the argument that moves a board isn't compliance. It's financial exposure.
📄 The one-pager >> lnkd.in/dabA7QeW
#AIGovernance #DataGovernance #CyberSecurity #CISO #GRC

Shadow AI showed up in 43% of security incidents last year, roughly double the year before. 68% of the companies that got breached had no policy governing AI use at all.
A new Forbes piece by Guney Yildiz digs into why, and it leans heavily on a point our co-founder and CEO Yakir Golan has been making for a while: most AI risk isn't the model, it's how people and agents actually use these tools.
Data leakage, over-broad permissions, third-party vendor exposure. His read is that usage risk accounts for 70 to 75% of the exposure, and that companies should probably manage as if it's even more.
The reason it goes unmanaged is simple. You can't price or govern what you can't see. Visibility of the full AI estate, approved and shadow, has to come before the risk number that reaches the board.
Read the full piece here >> forbes.com/sites/guneyyildiz…

By now (hopefully), most organizations have begun creating an AI inventory.
However, it’s far from complete.
Shadow AI, tools provisioned by individual teams or employees outside of any formal oversight, is far more prevalent than leadership even realizes.
It's the AI equivalent of shadow IT, except the risk compounds faster because these tools are often ingesting sensitive data with no record of what they're accessing or what decisions they're informing.
The kicker is that the governance challenge isn't just a matter of surfacing all shadow AI once.
It's more so building an approval process functional enough that teams have no incentive to work around it in the first place.
If the sanctioned path is too slow or too restrictive, people will find another one. They always do.
Discovery is the precondition, but sustained control should be the goal.
📄 More on how to build an AI inventory that accounts for sanctioned, shadow, and blocked AI: lnkd.in/d6UaNwEr
#AIGovernance #ShadowAI #CISO #GRC #EnterpriseAI

A survey conducted earlier this year found that only 36% of organizations have visibility into where their data is processed, trained, or inferred.
In other words, the vast majority of enterprise data environments are operating with governance that covers a single platform, maybe two, while the rest run without oversight.
Now layer AI on top of that.
Training data, inference data, retrieval data, etc.
All of it is flowing from an ecosystem that has only been partially mapped.
When the underlying data is of poor quality or inadequately traced, the consequences show up directly in model behavior.
You get drift, hallucinations, outputs that no one can explain.
AI governance starts with data governance, and data governance starts with knowing what you actually have.
📄 Full breakdown in the practitioner's guide we co-authored with CISO Christiane (Chrisi) Baetz, CISSP, CISA of the Financial Conduct Authority >> lnkd.in/d6UaNwEr

AI governance is starting to come up more often in boardroom conversations. But most organizations are still figuring out what it means to build a program that holds.
The starting point is always data.
Most organizations significantly underestimate how much of their data environment is ungoverned, and that blind spot follows them.
From there, governing the AI systems built on top of that data, and securing them against a threat surface that traditional frameworks were never designed to cover, requires a level of cross-functional coordination that most programs haven't achieved yet.
CISO Christiane (Chrisi) Baetz, CISSP, CISA, partnered with our CEO Yakir Golan and the experts at Kovrr to put together a practitioner's guide built around three interconnected pillars:
1. Data governance
2. AI governance
3. Security
If you're building an AI governance program or wondering why the one you have isn't holding up, this is worth reading.
lnkd.in/d6UaNwEr

Two more capabilities added to Kovrr's CRQ platform! 🚀🚀🚀
Scenario Intelligence is a new dedicated section of the platform that surfaces the latest cyber incidents and lets you filter for what's hitting organizations like yours then add them directly to your risk register.
Scenario templates in the cyber risk register let teams build new scenarios faster, starting from real-world events like SolarWinds or MOVEit, or from common pre-defined scenario types.
Both capabilities deepen the connection between Kovrr's real-world incident intelligence and the day-to-day work of managing cyber risk.
The threat landscape is always moving, and now your risk register can keep up.
Read the blog and dive into the details >> lnkd.in/dk7-4qxN
hashtag#cyberrisk hashtag#cyberriskquantification hashtag#CRQ hashtag#riskregister hashtag#GRC hashtag#scenarioplanning hashtag#CISO

Two more capabilities added to Kovrr's CRQ platform! 🚀🚀🚀
Scenario Intelligence is a new dedicated section of the platform that surfaces the latest cyber incidents and lets you filter for what's hitting organizations like yours — then add them directly to your risk register.
Scenario templates in the cyber risk register let teams build new scenarios faster, starting from real-world events like SolarWinds or MOVEit, or from common pre-defined scenario types.
Both capabilities deepen the connection between Kovrr's real-world incident intelligence and the day-to-day work of managing cyber risk.
The threat landscape is always moving, and now your risk register can keep up.
Read the blog and dive into the details >> kovrr.com/blog-post/bringing…

📣 We’re introducing a new way for organizations to approach 🇪🇺 EU AI Act compliance. Start automating the process today!
lnkd.in/dWDyz9gD
As the regulation moves toward full enforcement, teams are under increasing pressure to demonstrate that AI systems are governed in a structured and traceable way.
The problem is that documentation is fragmented, and evidence, if it exists at all, is spread far and wide across enterprise systems.
Consolidating all of that information is going to take a lot of work, and approaching it manually is not a viable option to maintain a consistent and reliable view of compliance.
Kovrr’s updated AI Compliance Readiness module now includes automated EU AI Act compliance capabilities designed to bring that process together
The platform automatically collects documentation from enterprise applications, maps evidence to #EU AI Act Articles, and provides visibility into which requirements are already supported and where gaps remain.
As documentation is reviewed, everything is organized into a structured EU AI Act Auditor Pack, including mapped evidence, requirement alignment, and a full audit trail.
From there, organizations can work with Kovrr’s audit partners to complete certification and obtain an official EU AI Act compliance certificate.
Explore how the 🆕 AI Compliance Assurance module supports EU AI Act readiness: lnkd.in/dWDyz9gD
#EUAIAct #AICompliance #AIGovernance #AIRegulation #Compliance #RiskManagement #GRC #AIRisk

How can cyber risk management support broader business resilience?
By being integrated into the enterprise risk strategy, quantified in business terms, and aligned with evolving regulatory expectations.
Organizations that treat cyber as a high-level enterprise exposure and prioritize it like any other are better equipped to make informed investment decisions and ensure operational continuity.
From using frameworks like NIST CSF to embedding CRQ into board-level reporting, strategic teams are turning cyber risk into a source of strength.
Resilience starts with communication clarity. And communication clarity starts by aligning cyber and ERM metrics.
Read more: lnkd.in/dVCh8q-x

The biggest hurdle to scaling GenAI isn't the technology, but it’s the inability to prove your risk posture. Without a clear way to quantify exposure, organizations are essentially paying for their insurer's guesswork, leading to unnecessarily high costs.
The best way to lower your costs? Prove you have a handle on the risk.
We’re excited to announce that by quantifying your enterprise’s GenAI financial exposure with Kovrr’s AI Risk Governance suite, you can now receive up to a 20% 𝑫𝑰𝑺𝑪𝑶𝑼𝑵𝑻 on your AI insurance premiums.*
How? We provide the high fidelity, insurer relevant data that carriers need to see to reward your governance efforts.
Kovrr's suite empowers your security teams to:
✅ Expose Shadow AI: Automate discovery of sanctioned and unsanctioned tools.
✅ Simplify Compliance: Auto-link data to regulations like the EU AI Act and NIST.
✅ Quantify Impact: Translate technical risks into clear financial terms (ALE).
✅ Be Audit Ready: Generate the evidence backed reports insurers demand.
Ready to see how your posture translates to direct savings? Check out the details here: lnkd.in/d5hp4QHt
*𝘐𝘯 𝘱𝘢𝘳𝘵𝘯𝘦𝘳𝘴𝘩𝘪𝘱 𝘸𝘪𝘵𝘩 𝘒𝘰𝘷𝘳𝘳'𝘴 𝘪𝘯𝘴𝘶𝘳𝘢𝘯𝘤𝘦 𝘯𝘦𝘵𝘸𝘰𝘳𝘬.
hashtag#AIGovernance hashtag#RiskManagement hashtag#AIInsurance hashtag#GenAI hashtag#CyberRisk hashtag#InsurTech hashtag#GRC

AI adoption is accelerating, but so is AI risk.
As insurers begin to evaluate GenAI exposure, organizations that can measure and prove their AI risk posture will have a clear advantage.
With Kovrr's 𝗔𝗜 𝗥𝗶𝘀𝗸 𝗚𝗼𝘃𝗲𝗿𝗻𝗮𝗻𝗰𝗲 𝗦𝘂𝗶𝘁𝗲, enterprises can assess and quantify their GenAI financial risk exposure, providing insurers with a comprehensive, data-driven view of AI risk in a market still adapting to AI.
Continuous monitoring of shadow AI, third-party dependencies, compliance posture, and modeled financial impact helps demonstrate stronger governance and risk control.
Receive up to a 𝟐𝟎% discount on your AI insurance premium by showing insurers a clearer picture of your AI risk.
Unlock your exclusive AI insurance discount today 👉 lnkd.in/d5hp4QHt
