
SAP security researcher and specialist
The Netherlands
Joined February 2009
- Tweets1.6K
- Following378
- Followers1.4K
- Likes605





Joris van de Vis retweeted

❗️ Linux is having a brutal week. Another local to root privilege escalation vulnerability just dropped: "Copy Fail 2: Electric Boogaloo."
This is the third Linux LPE in a row, after Copy Fail and Dirty Frag. The PoC is public on GitHub. There is still no coordinated patch.
openwall.com/lists/oss-secur…

🚨 BREAKING: New Linux zero-day "Dirty Frag" lets ANY local user become root on most major distros.
The PoC is already public, half of it isn't patched yet.
Discovered by researcher Hyunwoo Kim, the exploit chains two kernel bugs and sits in the same family as Dirty Pipe and Copy Fail.
▪️ CVE-2026-43284 (xfrm-ESP Page-Cache Write): patched in mainline Linux.
▪️ CVE-2026-43500 (RxRPC Page-Cache Write): NO PATCH yet.
The exploit is reliable by design. Attackers don't have to win a timing race, the system won't crash and alert anyone if it fails, and it succeeds nearly every run.
The embargo got broken before distros could ship fixes, so the working code is now sitting on GitHub.
Confirmed working on: Ubuntu 24.04.4, RHEL 10.1, openSUSE Tumbleweed, CentOS Stream 10, AlmaLinux 10, Fedora 44.


Joris van de Vis retweeted

"Scattered Lapsus$ Hunters (UNC3944)", have released an alleged SAP7 0day exploit onto Telegram.
I can't confirm or deny if it's an actual 0day, I have no way to test or confirm anything. However, it is fully weaponized.
I've uploaded it to VXUG
vx-underground.org/tmp
The premier SAP Security Customer events returns to Rotterdam! See here for details:
linkedin.com/posts/jorisvand…

Joris van de Vis retweeted

Super proud of the amazing work the team has done!

Our team has responsibly disclosed six new #zeroday vulnerabilities in #Enphase IQ Gateway devices. Thanks to the efforts of @Wietsman, Hidde Smit, Max van der Horst and @seccubus, the internet has become a bit safer this week. More info ➡️ divd.nl/newsroom/articles/di…
Joris van de Vis retweeted

Since 12/22, SAP is patching critical vulnerabilities as a result of a research project that I've been doing for some time. Today, my key finding was patched: CVE-2023-28761. An innocent 6.5 bug, that opens the door to abusing all those critical patched bugs through the Internet.


Joris van de Vis retweeted
Together with all the other volunteers of @divdnl we've made it in to the @ncsc_nl Wall of Fame 2022!
Congratulations, super proud of everyone for all the hard work that went in to making this happen.
ncsc.nl/contact/kwetsbaarhei…

Joris van de Vis retweeted
@PROTECT4S wishes our fellow Chinese friends a Happy Chinese New Year!
Secure your SAP systems for your year to be as lovely as the rabbit.Strengthen your SAP security to be as sensitive as a rabbit’s hearing.Detect threats to secure your SAP systems.
Contact us! Link below!

Wat een leuk @DIVDnl eindejaarsfeest! Met vuurspuwen en een lokaal kampioenschap server werpen 🤩
Joris van de Vis retweeted

🙌🏾
Since I left @SecureAuth, I was looking for new homes to the SAP security open source tools I've been maintaining for the last 10 years.
I got to share that we found new communities to host them! 😀
+ details: linkedin.com/feed/update/urn…
(cont)

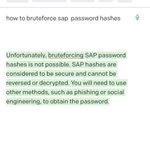
Beta.OpenAI.com is fun to play with. From marketing taglines to even Abap code snippets with great outcome. Yet this is just plain wrong 😂 ⬇️ #ibegtodiffer

Joris van de Vis retweeted

The SAP SSFS decryptor is ready!
#sapsecurity #penetrationtesting


Joris van de Vis retweeted
How does Protect4S incorporate the concept of risk into its SAP Vulnerability Management solution?
Read a previous blog by SAP Security researcher and co-founder of @PROTECT4S, @jvis, to find out the various methods Protect4S use to reduce risk.
protect4s.com/2020/06/04/sap…

Joris van de Vis retweeted

I am looking for the zone files or TLD lists of .cn, .ir, .iq, .kz, .kp, .ru, and .ykp. I think I have exhausted every publicly accessible resource in the last seven years, but I want to ensure a complete view despite some countries' internet filtering. Who should I ask for help?

ALT Internet world scan map: China, Iran, Iraq, Kazakhstan, Myanmar, North Korea, Russia, and Ukraine are not highlighted.
Joris van de Vis retweeted
Based on our customers' experiences, we found 6 main reasons why SAP Solution Manager is too limited for SAP Vulnerability Management.
Find out more in this previous blog written by @jvis, SAP Security researcher and co-founder at Protect4S.
protect4s.com/2022/05/04/6-r…
