



Recent Developments in SNARKs and Their Connection to FHE w/ Dan Boneh meetup.com/fhe-org/events/30… #Meetup via @Meetup

joost retweeted

Exciting news from @Yubico! You can now purchase the #YubiKey 5 Series and Security Key Series with new 5.7 firmware, featuring increased passkey storage and expanded security. Check out our latest blog to get your hands on them for yourself. sprou.tt/1ZV2S5ty51w

joost retweeted

Interested in learning Haskell? The full set of 16 videos from my introductory course based on the book "Programming in Haskell" is now freely available on YouTube. Happy Haskelling :-) tinyurl.com/haskell-notts

joost retweeted

Interested in the Wallet's code release? On 18 March, 16h CET by the @OpenWalletFdn — the EC's wallet team will present the wallet's Reference Implementation and answer questions.
Sign up below! ⬇
zoom.us/meeting/register/tJU…
joost retweeted
The open-source code of the EU Digital Identity Wallet has just been published on our #GitHub.
Are you a developer yourself? Give your two-cents on the code directly on our github:
github.com/eu-digital-identi…
joost retweeted

🔐 Dive into the FIDO Passkey experience with us! Yubico UX needs #YubiKey users for a study on Passkey use on desktop & mobile. Share your insights & get 50% off a YubiKey 5 Series! 🚀
👉 Join now: forms.gle/RiDV3spVJnznn4ta8
#UserExperience #UsabilityStudy #FIDOPasskey

Ooh, I just realised my Erdős number would be 5, through Lambert Meertens and @headinthebox (were it not that computer science probably doesn't count as a Mathematical Discipline)
en.wikipedia.org/wiki/List_o…
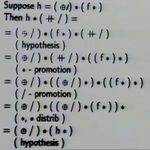
Stumbled upon this gem last night. A recording of a lecture by the late Richard Bird on programming algebra, given at my Alma Mater in 1986.
Also reminds me of the lectures by Lambert Meertens where he often ran out of Squiggol operator symbols. ⊗⊛⦿△
podcasts.ox.ac.uk/introducti…

Another fun holiday project from @smallsteplabs: authenticate to your Wifi network using certificates and enrol your Apple devices automatically using #ACME Device Attestation. You bring your access point, they bring their CA and RADIUS server.
smallstep.com/blog/home-netw…

joost retweeted

On November 29th, join us for the unique, free webinar where @PaulaCqure (@CQUREAcademy) and @joostd (@Yubico) will delve into the crucial aspects of secure credential storage.
🔗 Register here: cqureacademy.com/webinar/und…
#staycqure

joost retweeted

Did you know there are approximately 85 organizations authorized to issue TLS certificates for the web today? Or that seven of them issue 99% of all certificates currently in use? The presence of the others is largely intended to accommodate web openness and national sovereignty—an admirable goal, albeit one that introduces a significant attack surface for every web user.
But were you aware that the recent eIDAS legislation, that was just signed, will obligate browsers to trust all QWAC-approved CAs listed on the EU Trust List (esignature.ec.europa.eu/efda…)? To illustrate, Spain has 13 CAs approved to issue these certificates and there are 27 member states in the EU. Additionally, did you know the legislation will not permit browsers to remove of CA with a history of repeated incompetence without government approval?
The most famous of all CA distrust events was an EU CA known as DigiNotar, and those in the PKI space might say that 12 years ago and today, the Conformity Assessment Bodies would have caught that and dealt with it proactively. But is that true? Check out the history of Camerfirma (wiki.mozilla.org/CA/Camerfir…) and wonder why an organization with such poor operational practices that the internet isn't dependent on is still trusted by anyone? Then ask why the associated CAB still lets it be approved as a CA for issuance.
For those who say that the web doesn't need Browsers for such actions, consider this recent incident involving a Turkish CA (bugzilla.mozilla.org/show_bu…). And for those who doubt governments would use CAs to gain visibility into web traffic, take a look at this case where a French CA was doing just that: arstechnica.com/information-….
Supposedly the final text has a recital that was added to the language to suggest that the scope of these requirements is to be limited to trusting these CAs for identity information and not the domain but the document is still private so we don't know for sure. Even if true recitals are not binding and the bill has other issues, for example, it requires browsers to reinstate user interface that has been proven to be harmful and misleading to users. arstechnica.com/information-….
It also prevents the Browsers from establishing additional requirements for the CAs above and beyond what is included in the associated EU legislation, for example, they won't be subject to certificate.transparency.dev which has helped catch many many issues. All this means calcifying the web making it impossible to move forward without legislative change and leaving the web less secure at the same time. Change will now be governed by regulators, lobbyists, and standards boffins that either benefit from this weakening of the web or have no accountability for its consequences.
There are 195 sovereign nations in this world. each would love to be in a position to observe everything their citizens and everyone who interacts with them does. When the world's most liberal and democratic governments put into place the tools to enable mass surveillance and weaken internet security in this fashion what makes us think the rest won't as well.
The “just trust me, ok?” approach to internet security. @Scott_Helme quoting from the near-final text of the eIDAS 2.0 regulation

Government Mandated Root CA.
Yikes, that's a phrase that fills me with dread! Is it really where we're heading?..
scotthelme.co.uk/what-the-qw…

joost retweeted

Yubico joins EWC’s large-scale pilot for EU digital ID wallets ahead of #eIDAS 2.0
biometricupdate.com/202311/y…

Nice Root Causes podcast on Digitally Signing Images on Cameras by @TimCallan via #soundcloud soundcloud.com/tim-callan/ro…

Also see @danboneh's story on how to authenticate photo's that have been post-processed
medium.com/@boneh/using-zk-p…
joost retweeted

Future proof authentication with #passkeys - catch @Yubico's @joostd's session at #PlatformSummit2023: nordicapis.com/sessions/futu…


Nice! Okta adds support for OAuth DPoP as a more secure alternative to bearer tokens
okta.com/blog/2023/06/a-leap…
Interesting @smallsteplabs webinar coming up (and not just because of the free #YubiKey)! hopin.com/events/access-your…