





Jay Nilendu Vora retweeted

🚨Python friends, upgrade (or have your agent upgrade) every certifi package across all your projects and machines!
uv self update
uv lock --upgrade-package certifi
Private keys from 8 intermediate CA certs have been compromised!
xitter.cf/astuyve/status/2112559…
Some other things to upgrade:
* Go: 1.27.3 or 1.26.10, then rebuild your Go programs
* rustls-webpki: 0.103.16
* webpki-roots / webpki-root-certs: 1.0.10
* Electron: 44.9.1, 43.8.1 or 42.11.16
* NSS: 3.131.1
* Firefox: 158.0.1 (ESR: 153.5.1 or 115.43.1)
* Ubuntu ca-certificates: 20260816ubuntu0..1 (for 22.04, 24.04, 26.04 and 26.10)
* Homebrew ca-certificates: 2026-09-25_1
* Chrome, Apple, Windows: nothing to do, they’re blocked automatically
Still waiting for a fix:
* Debian ca-certificates: disable the two roots by hand
Node.js
* Composer ca-bundle
* macOS /usr/bin/curl: remove the two roots from /etc/ssl/cert.pem by hand

private keys from 8 intermediate CA certs have been compromised (eMudhra)
Happy "Update everything" day to all my pager-carrying friends
emudhra.we-have-a-problem.co…

Jay Nilendu Vora retweeted

If you are wondering whether your website is affected, we have packaged a Codex skill to help check.
Point your Codex at this repo to guide you through it: github.com/openai/php2shell-…


OpenAI models helped researchers—operating as part of our Patch the Planet initiative—discover critical security flaws in PHP, an open-source programming language used to run an estimated 70% of websites.
Over the past two months, we led a coalition of maintainers, researchers, and security providers to prepare fixes and protections ahead of disclosure. This duration was necessary because the fix was quite intricate and required a major change to the PHP engine. Every site using PHP can now safely upgrade their version to stay secure, in addition to applying mitigations from various security vendors.
Due to the severity of these flaws and PHP’s widespread use, we consider this bug to be one of the most impactful vulnerabilities in recent memory. It also marks a new phase, where AI can find security bugs with internet-scale impact.
This is an example of the Defender’s Window in action: to our knowledge, frontier AI was able to find this vulnerability ahead of attackers, giving defenders time to prepare.
openai.com/index/coordinated…

Readers added context they thought people might want to know
OpenAI may claim a role in the coordinated response and patching process. But the initial discovery and exploit development, however, occurred several months earlier by an independent researcher.
x.com/lcfr_hax/statu…
Jay Nilendu Vora retweeted

Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
Jay Nilendu Vora retweeted

Crazy 72 hours in security. Three major incidents dropped back-to-back: eMudhra, PingCAP (TiDB Cloud), and PHP.
Here is the short version of what happened and who got hit.
1. eMudhra (Trusted CA compromise)
eMudhra generated 8 intermediate CA certificates in April 2025 (cross-signed by Sectigo). A bug in their HSM key-wrapping test script created a second set of P-384 keys where the private keys were single-byte numbers under 256. Operators picked the wrong key labels and signed them into real CA certs.
One of the intermediate CA private keys was literally the number 4.
The other seven: 56, 66, 115, 155, 156, 230, 237.
Three weeks later (May 2025), their CRL signatures started failing because the CRL signer was using the real keys instead of the weak ones. Instead of asking why the keys didn't match, someone switched the CRL signer to the weak keys and closed the ticket.
• Browsers are safe: Chrome, Firefox, Apple, and Microsoft already blocked them, and zero rogue certs hit CT logs.
• Servers are not: curl, Python (certifi), Go binaries, and Docker base images don't check CRLs. Update ca-certificates, certifi, and Go (1.27.3 / 1.26.10).
• 10-second check on any server:
curl dv-g3b-emudhra.we-have-a-pro…
(TLS error = safe. 200 OK = still vulnerable.)
2. PingCAP / TiDB Cloud (10.6 TB breach)
Attackers found GCP and Azure credentials committed inside PingCAP's own repos. They set up a replication feed of TiDB Cloud's production control plane and exported the entire database every 6 hours for 22 straight days. 88 full exports, zero alerts. 200 GB is already out on torrents.
Beyond the 413 private repos and 20.6M customer SQL queries logged from their web SQL Editor, PingCAP engineers were pasting customer secrets into Jira tickets.
Who is affected in the leaked records:
• Live credentials exposed in support tickets:
- Pinterest: AWS keys for their pingcap-logs S3 bucket
- CardX / Silverlake (NPCI-linked env): AWS admin key in a backup log with full access to 258 external S3 buckets
- DeBank: 38 presigned S3 URLs
- An unnamed AI/dev platform: a 314 MB slow-query log attached to a ticket containing 8,027 live customer secrets (an AWS root key, a GitHub admin PAT over 1,701 repos, 7,485 AWS STS tokens, and 192 OpenAI/Anthropic/Gemini keys)
• Tenants with infra metadata, VPC CIDRs, app-server IPs, or contract pricing exposed:
- Tech: Atlassian, Databricks, Airbnb, Baidu, LINE, Nylas, Persona, PatSnap
- E-comm & Travel: Booking.com, Shopee, Flipkart, Mercari, ZOZO, AEON, Delhivery, Klook
- Gaming: Capcom, Square Enix, Konami, Bandai Namco, Cygames, Colopl, DMM
- Finance: PayPay, SoftBank, SBI, SB Payment Service, Fujitsu, TOPPAN, Bank of China, China Life
- Crypto: Bitget (said only public trade logs were on it and they already left), Pionex, DigiPlus, NFTscan, Chainbase
• Developer profiles leaked (from a purchased reo.dev table in PingCAP's BigQuery):
- 24,900 personal emails + GitHub/LinkedIn profiles of engineers at Tencent (3,327), Huawei (2,726), ByteDance (2,475), AIG (2,140), Mastercard, Flipkart, and bKash.
If you use TiDB Cloud: rotate your console API keys, DB passwords, and anything you ever pasted into a support ticket.
3. PHP "PHP2Shell" (CVE-2026-109618 & CVE-2026-109619)
Two CVSS 9.2 pre-auth RCEs leaked yesterday ahead of today's 14:00 UTC patch.
Public writeups trace it to a heap Use-After-Free in PHP's native C multipart/form-data session upload-progress handler (ext/session/session.c).
Because C-level multipart parsing runs before line 1 of index.php:
• App auth, Laravel/WordPress middleware, and file_uploads = Off do not stop it.
• Only PHP 8.2–8.5 get official patches today (59% of PHP servers on Shodan are on EOL <= 8.1).
• Until you patch php-fpm: lock php_admin_flag[session.upload_progress.enabled] = off and block unexpected multipart requests at Nginx/Apache/Cloudflare.
Attention all PHP engineers! @laravel

Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on php.net. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or ic3.gov. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on php.net, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.

ALT Critical vulnerability alert for PHP Core with CVE-2026-109618 and CVE-2026-109619, CVSS score 9.2, urging immediate patch and threat hunting.
Jay Nilendu Vora retweeted

We’re releasing the world’s best Indic voice AI model, fully open-weight. 🇮🇳🇮🇳
With over 1.5 billion people and 22 official languages, the future of AI for India is voice-first.
Maya-2 officially outperforms ElevenLabs v3, Cartesia Sonic 3.5, and Bulbul v3 across Indian languages.
It will be completely free for every builder very soon.

*યાદ મુકી જવાનો આ એક જ રસ્તો છે...*
*કા તો એવું લખો કે લોકો વાંચ્યા કરે*
*અને*
*કા તો એવું જીવો કે લોકો લખ્યાં કરે...*
🌹🌹 *સુપ્રભાત* 🌹🌹
Jay Nilendu Vora retweeted

Initially, when I started hearing about this, I did not want to write about it so as not to sensationalise it.
Now many people are coming forward with what is happening to them.
Being laid off is not in your control, but please do not quit your job in the software industry.
People with even 10 to 20 years of experience are not getting even a single call after literally hundreds of applications.
Except in certain domains and niches, it looks like no meaningful recruitment is happening in the software industry. I am not only talking about entry level jobs. It is jobs at any level.
Sridhar Vembu has posted today that Zoho cannot give the usual pay hikes this year. A person who has created so much rural employment is now saying he will work hard towards avoiding mass layoffs.
Zoho has not been able to meaningfully add to its employee count for the last 18 months. As an ultimate insider, Vembu says the outlook is becoming grim for software jobs.
There is no magic wand to offer immediate solutions for such serious problems.
The past has taught us that new industries and new opportunities keep emerging.
That is what the entire software industry may also go through in the next few years.
Vembu ends the note by asking everyone to pray for them.
Well said!

The business outlook for software is uncertain and AI has raised costs dramatically with a) massive 4-fold increase in server prices which we need for data centers b) AI usage increasing rapidly, leading to much higher expenses, which we are trying to control.
On top of that is the challenging geopolitical backdrop.
We have cut down on our marketing budget. We have also told our employees that we cannot have our usual pay increase this year. I have apolgized for not being able to avoid this.
We will work hard to avoid mass layoffs but the outlook for software jobs in general is grim. We have not been growing our employee count for 18 months now.
Most of our employees understand the situation. I am thankful to them.
We are in the middle of reinventing ourselves. The next 3-5 years will decide how our reinvention has worked. Please pray for us 🙏
Jay Nilendu Vora retweeted

@IRCTCofficial I have forgotten a bag on this PNR. Please help. PNR 6409812597.
Jay Nilendu Vora retweeted

I think people in India ahould now thank PM @narendramodi who despite pressure didn't allowed Pfizer vaccine in India
He faced all kind of political abuse

IT IS OFFICIAL. 💥
PFIZER HAS JUST PUBLISHED THE LIST OF POSSIBLE SIDE EFFECTS
OF ITS «COVID VACCINE». 💥
IT IS A CRIME!
1) Blood clots,
2) Acute kidney injury,
3) Acute flaccid myelitis,
4) Positive antibodies against sperm,
5) Brainstem embolism,
6) Brainstem thrombosis,
7) Cardiac arrest (hundreds of cases),
8) Heart failure,
9) Thrombosis of the heart chamber...
10) Cardiogenic shock,
11) Vasculitis of the central nervous system,
12) Death of newborns,
13) Deep vein thrombosis,
14) Brainstem encephalitis,
15) Hemorrhagic encephalitis,
16) Frontal lobe epilepsy,
17) Epileptic psychosis,
18) Facial neuropathy,
19) Fetal distress syndrome,
20) Gastrointestinal amyloidosis,
21) Generalized tonic-clonic seizures,
22) Hashimoto's encephalopathy,
23) Vascular thrombosis of the liver,
24) Reactivation of shingles,
25) *Reactivation of cancer...
26) "Turbo"-cancer,
27) Immune-mediated hepatitis,
28) Interstitial lung disease,
29) Embolism of the jugular veins,
30) Juvenile myoclonic epilepsy,
31) Liver damage,
32) Low birth weight,
34) Multisystem inflammatory syndrome in children,
35) Myocarditis,
36) Seizures in newborns,
37) Pancreatitis,
38) Pneumonia,
39) Stillbirth,
40) Tachycardia,
41) Temporal lobe epilepsy,
43) Autoimmune disease of the testes,
44) Thrombotic stroke,
45) Type-1 diabetes mellitus,
46) Venous thrombosis in newborns,
47) Thrombosis of the vertebral artery,
48) Pericarditis,
49) Sudden infant death syndrome.
SEVERE CONSEQUENCES of a so-called vaccine that neither protects against the disease, nor against its transmission or severe courses!

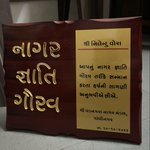
Reason your name should be full on profile! Extremely proud feeling being a #Son and known as ‘Son of Nilendu Vora’! Father was felicitated as ‘Pride of Society’ based on his selfless service of Humanity ! 111 times donated blood, Blood Centurion, Eye Donation, Body Donation, cremation of abandoned dead bodies!
A late Immigration counter at airport made me miss to witness this by merely 2 mins!
Extremely proud to share that the same event the stalwarts
@falgunivasavada @samirjoshipura also got the award!
Proud leader @dhwaniJayvora !

Jay Nilendu Vora retweeted

🚀 Ramco vs Odoo vs ERPNext—which ERP fits your service business?
Compare features, flexibility, project management, and scalability before making your choice.
👉 Read the full comparison with SerpentCS!
serpentcs.com/blog/ramco-vs-…
#Odoo #ERP #ERPNext #BusinessGrowth

Jay Nilendu Vora retweeted

आज जब telecom और digital technology का इतना महत्व है... तब इससे जुड़े security framework को भी... चाक-चौबंद करना आवश्यक है।
Phone की Security और Network की Security...
ये हम सभी की प्राथमिकता है: PM @narendramodi


Jay Nilendu Vora retweeted
AI IS MOVING FAST. ARE YOU READY? 🤖
A look back at AI Everything Abu Dhabi 2026 — great conversations, new connections, and exciting possibilities around #AI, #ERP & business transformation.
Thank you to everyone who connected with #SerpentCS! 🤝
#AIEverything2026 #Odoo


Had no idea if this was chase-able those days! The greatest chase and the match, I had witnessed live on TV!
Amazing commentary too!
@cricketwallah

Jay Nilendu Vora retweeted
🚀 Day 1 at AI Everything Abu Dhabi 2026!
AI meets ERP, and the future of smarter business starts here. 🤖⚡
Meet #SerpentCS and discover the power of #AI + #ERP.
#AIEverything #AbuDhabi #DigitalTransformation