

Reverse engineering, malware
Joined December 2016
- Tweets557
- Following472
- Followers2K
- Likes2.1K



Johann Aydinbas retweeted

⚰️We are back from the dead! And we brought some goods!
New loader, calls itself #SauronLoader, sold in underground forums to Russian-speaking criminals only - and already appeared in multiple incidents in Germany.
Keep an eye on this, link below 👇
medium.com/@DCSO_CyTec/sauro…

Johann Aydinbas retweeted
Heard about those zero days in Chrome and Windows? Well, @markkelly0x found them being used in the SAME exploit kit, proliferating across the APT ecosystem.
Meet BlueMoon exploit kit:
proofpoint.com/us/blog/threa…

Johann Aydinbas retweeted
I found a previously undocumented passive Windows backdoor I’m calling SLEEPWALKER. Its defining feature is a custom command language with 23 instructions. Instead of receiving conventional commands, it runs encrypted bytecode programs that can combine scheduling, nested programs, staged payload delivery with SHA-256 verification, decompression, network communication and in-memory shellcode execution.
The analyzed file is an unsigned DLL that masquerades as Microsoft's dpapi.dll, uses forged ESET metadata and activates only when side-loaded by ESET's Management Agent program ERAAgent.exe. SLEEPWALKER does not beacon or open an obvious listening port on its own. It monitors network traffic and stays dormant until it detects a specially crafted packet carrying an AES-256-CCM-protected task. It supports TCP, UDP, ICMP, SMB named pipes and VMware VMCI. VMCI can carry traffic directly between a VMware guest and host without using a conventional network interface. SLEEPWALKER also implements a DNS trigger that uses Base32 to carry encrypted tasks inside DNS labels, although the analyzed sample does not enable it.
The full analysis documents the bytecode format, all 23 instructions, encryption, DNS encoding, trigger logic and network transports. It also includes IOCs, a YARA rule and a PowerShell scanner.
If you believe you have been targeted by SLEEPWALKER or have found a related sample, please contact me. I created the SLEEPWALKER Analysis Toolkit to decode its bytecode, examine artifacts and safely reproduce its receiving pipeline without executing commands or transmitting data. If you suspect you've been infected, I am happy to share this toolkit with you, alongside a mitigation guide providing investigation steps and a remediation script for use after detection.
r136a1.dev/2026/08/24/sleepw…
Johann Aydinbas retweeted

👊 🇰🇵 🔥 Friends and Foes, Comrades and Competitors, Allies and IT Workers, today we put out the call for original research to be presented at BSides Pyongyang 2026. BSides Pyongyang is the oldest global BSides conference, but this is our second year offering a virtual option so that we may charitably expose the rest of the world to the glory of our cybersecurity prowess.
The CFP deadline is September 22.
Fill out the form and see if you have the Juche: forms.gle/x2LKBWYSddnmKNbu9

A sample matching that unknown "$Loading co" surfaced:
virustotal.com/gui/file/e67a…
Another confirmation Ansys LS-DYNA was the target of #fast16, as the sanity check matches on what looks like a component of LS-DYNA as well, so one less mystery!


Johann Aydinbas retweeted

Don’t Eat The #ChocoPoCs! How Vulnerability Researchers Were Repeatedly Targeted By Trojanised Exploits
sekoia.com/blog/dont-eat-the…
Discover our joint threat intelligence report with @YesWeHack.


Johann Aydinbas retweeted

We found a WHQL-signed kernel module that abuses Windows firmware table registration as a covert kernel↔user communication channel.
Instead of exposing a device object and IOCTL interface, it registers a custom firmware provider ("BSBS"), allowing userland interaction through standard Windows firmware table APIs.
The implementation is compact and stealthy, supporting memory allocation, memory copy operations, and indirect function dispatch from user mode into kernel context.
An unusual example of firmware table registration being repurposed as a hidden ring3↔ring0 communication mechanism.
Name: NewDriverMMM
SHA256:
1d9224a72e64bb2aad289edc81ea0720c764511c3e2b5beb5d0d5ce82a719abd
fdb3907ddda9ff9bd9ec4f8bd29aad823da77b5b3bf599813fecd034b0221189
SpcSpOpusInfo: 深圳市奥联信息安全技术有限公司
Telemetry: China 🇨🇳, Japan 🇯🇵


I hate logging in.
I HATE LOGGING IN.
I log in to my password manager so I can login to my SSO account so I can login to the service so I can enter a 2FA for which I login to my phone so I login to the authenticator so I can get a 2FA code so I can finally login. GOD DAMNIT.
Johann Aydinbas retweeted

We report certificates for revocation when they sign malware.
What about before they sign malware?
I've started adding certificates to Cert Graveyard that are being used to "warm" the certificate and improve it's score before being sign malware.
1/4

Johann Aydinbas retweeted

Download our 142-page #EasterBunny report (open access):
EasterBunny: advanced espionage artifacts attributed to APT29 lab52.io/blog/easterbunny/ #APT29
Johann Aydinbas retweeted

We investigated a CN #APT that targeted multiple governments and companies with government contracts in Asia. In half of the targets we found a second group with different malware toolkit but sharing the infection vector and some post-exploitation tools trendmicro.com/en_us/researc…

ALT Countries being targeted by SHADOW-EARTH-053 and SHADOW-EARTH-054

ALT Table comparing SHADOW-EARTH-053 and SHADOW-EARTH-054

ALT Links from SHADOW-EARTH-054 to other intrusion sets

ALT Dates of different campaigns by SHADOW-EARTH-053 and SHADOW-EARTH-054
Johann Aydinbas retweeted
We didn't know how an actor was using EV Certificates issued to Lenovo and others.
We now do.
From DigiCert's incident report:
"the threat actor used a compromised analyst endpoint to access DigiCert's internal support portal. The threat actor used a limited function within the customer-support portal which allows authenticated DigiCert support analysts to access customer accounts from the customer's perspective to facilitate support tasks. The threat actor was able to use this function to access initialization codes for orders that were approved but pending delivery for EV Code Signing certificate orders across a finite set of customer accounts."
"Possession of the initialization code, combined with an approved order, is functionally sufficient to generate and retrieve the corresponding certificate."
The full report can be found here and explains the incident in great detail: bugzilla.mozilla.org/show_bu…
The report mentions "Where we got lucky: A community member involved in security research reported the evolving pattern of misused certificates and engaged in dialogue with our support team. Without that report, the undetected compromise of ENDPOINT2 and the associated mis-issuance might have remained undiscovered for a longer period."
Special thanks goes to the regular contributors to the Cert Graveyard; @g0njxa , @malwrhunterteam , and others.
Also special thanks to DigiCert: this report has a high level of transparency, which is warranted, and also well executed.

What do Lenovo, Kingston, Shuttle Inc, and Palit Microsystems have in common?
EV Certificates from these companies were issued and used by a Chinese crime group, #GoldenEyeDog (#APT-Q-27)!
Thanks @malwrhunterteam and @g0njxa for your contributions
1/7


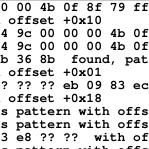
I converted the #fast16 patch engine instructions to human-readable to get a better understanding what exactly is being done
It's a pretty nifty engine:
- wildcards
- patterns can depend on other patterns
- scratch space
- fixup instruction
Full list:
gist.github.com/usualsuspect…

I couldn't find any further leads but I believe the 5966513a12a5601... (LS-DYNA related) is most promising:
- multiple pattern matches
- Intel check passes
- FPU stuff
Intel check makes a lot of sense here, as these early LS-DYNA solvers had to be compiled with Intel Fortran!

Johann Aydinbas retweeted

Europe is building stronger systems to report vulnerabilities, but it risks overlooking the people who discover the flaws first: independent security researchers, write @eubenincasa and Max van der Horst.
Read the article: bindinghook.com/europe-forge… #EUcybersecurity

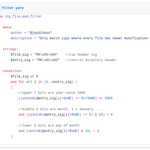
YARA rule to filter for zips in which all files are newer than some date
gist.github.com/usualsuspect…
