






Jay ツ 🇮🇳 retweeted

I want to be very clear about this.
just because we found one serious exploit on openai does not mean we know how to secure an organization that complex. openai has security people with far more experience and better qualified doing that than us, and i don’t want to pretend we have solutions.
note, i was saying "they are building manhattan project", it is not a belief i strongly hold, i don’t like making confident predictions about the future. it is the labs that make those comparisons.
what I know for a fact is that these models already have serious offensive cyber capabilities, what that does to the world, I don’t know, but my loosely held view is that it might lead to a period of turbulence because i think its offense dominant than defense
having said that, what i don’t understand is this, if the people building these systems truly believe they are powerful enough to create nuclear level risks, and they are talking about slowing down because of those risks, why is that work is done through ordinary saas products?
why is it happening through slack, managed github, employee browsers, and apps accessible from the public internet? every third party and library they use becomes part of the attack surface.
remember the jfrog registry in the hugging face agent swarm? it didn’t matter that it was a third party, it was in the path. an attacker, or an unaligned model, doesn’t care who owns it or its out of scope. they will hack whatever is in the path to achieve their goal.
one more concerning thing is, why are codex cloud, claude(assuming anthropic does the same) publicly accessible web applications connected directly to private github repositories?
again shouting my lungs out, coding agents on the cloud is worst thing happened in terms of security, it is going backwards.
your browser becomes a attack surface, a lame xss, stolen creds, phishing, browser exploits, all these bugs can achieve similar impactful bugs as we shown. like, you don't need to pivot anymore and worry much about exfiling, just compromise cloud agent its all over either through client-side browser or the server.

Hacktron founder @S1r1u5_ argues OpenAI is running a “Manhattan Project” on Slack and GitHub, giving it the same basic attack surface as any startup:
"Every repository is running on github .com/openai. It's the same thing that Hacktron uses or any other company uses."
"We have friends at OpenAI who are much more capable than what we could do. But what I can say is, why is it running on Slack? Why are you running this Manhattan Project from Slack? Why are you hosting your repositories on github? That looks silly to me."
"Your attack surface becomes Slack. You can hack a Slack employee and go through that and get into OpenAI. You can hack GitHub, go through that and get into OpenAI."
"My claim is it shouldn't be running on B2B SaaS if you are building Manhattan Projects. That's all I'm saying. I can think of numerous ways on how to get into that."
@HacktronAI @rootxharsh
Jay ツ 🇮🇳 retweeted

@bsidesahmedabad is here.
So is the Barracks WarGames LHE.
FREE for all.
Online Qualifiers on 12th September.
Top 40 move to finals on 26th September at Bsides on-site.
Top 3 from these qualifiers get Bsides pass on us.
Epic final prizes. Swags. Career ops. And more.
Jay ツ 🇮🇳 retweeted

If you're going to take the big career risk, do it between 22 and 25.
Not because you'll magically be braver then. Because that's the last window before marriage, kids, and real responsibility make the same risk cost ten times more.
Jay ツ 🇮🇳 retweeted
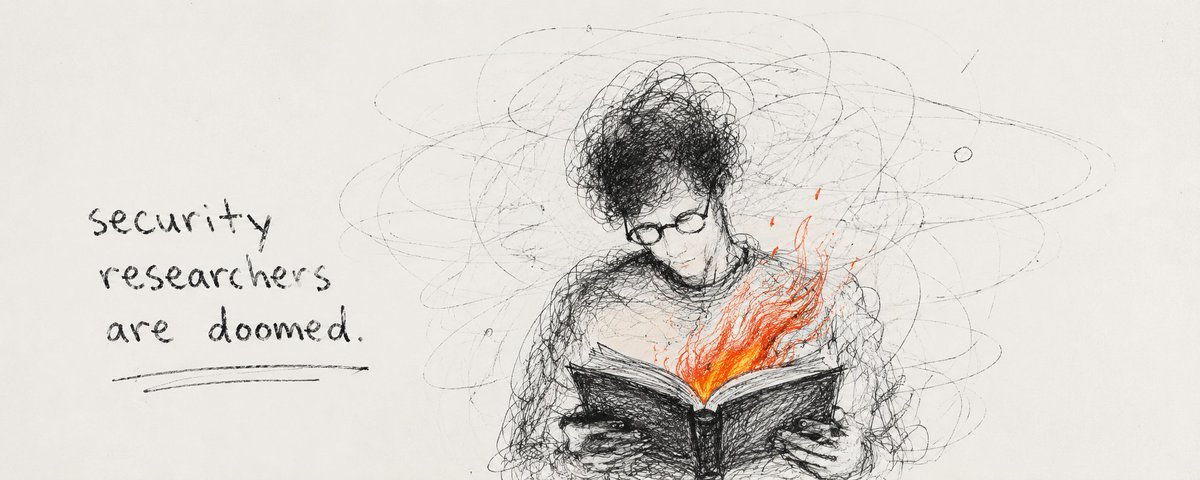
“Security researchers are doomed because of AI.”
I kept hearing versions of this, so I went back through 500 years of people saying the same thing every time a machine learned a human skill.
Some were idiots.
Some were right.
Here’s where I landed.
Jay ツ 🇮🇳 retweeted

Seems that wp2shell PoCs are now floating around the internet, so we've published our blog post including our research methodology for finding the bug as well as a deep dive into the chain itself - slcyber.io/research-center/e…
Jay ツ 🇮🇳 retweeted

Here's the YouTube video with appropriate audio youtube.com/watch?v=-TiET_K-…

Jay ツ 🇮🇳 retweeted

Wrote about the open weight problem as well a few weeks back. IMO, it’s the biggest issue that we have with agent security/trust with no obvious mitigation.
originhq.com/research/the-mo…


Jay ツ 🇮🇳 retweeted

Andrej Karpathy quietly shipped the best second brain idea in years
not an app. a pattern. let an llm maintain a wiki of your notes.
you dump sources, it reads them, links them, files them. knowledge compounds like interest.
someone built it into a free claude code plugin.
setup is two commands:
claude plugin marketplace add AgriciDaniel/claude-obsidian
claude plugin install claude-obsidian@agricidaniel-claude-obsidian
then open obsidian, open claude code in the same folder, type /wiki.
that's it. your notes are now queryable by claude and
they get richer every time you read something.
bookmark this. best thing you'll build this weekend.


Jay ツ 🇮🇳 retweeted

I wrote about what we should do to secure critical US infrastructure before open source AI models are highly competent at hacking josephthacker.com/hacking/20…

Jay ツ 🇮🇳 retweeted

The best hackers I know aren't smarter than me.
They've just read more than me. Somewhere in their memory is the one obscure writeup that turns a dead end into a finding. Preview is that memory, on tap. For you, and for your agent.
-> rag.preview.is


Jay ツ 🇮🇳 retweeted

m14r41/pentestingchecklist: Comprehensive, data-driven security assessment checklists across 23 platforms web, API, mobile, cloud, Active Directory, Kubernetes, LLM, and more. Expandable hierarchy, global search, progress track... github.com/m14r41/Pentesting…

Jay ツ 🇮🇳 retweeted
“I don't like giving up on people. I’d rather torture them into greatness.”
— Nvidia CEO, Jensen Huang

Jay ツ 🇮🇳 retweeted

GLM-5.2 is Fully Open, Frontier Intelligence Belongs to Everyone
Today, the sudden restriction of certain frontier models is deeply regrettable. At a time when access to frontier models is abruptly cut off for non-technical reasons, we are even more convinced of one thing: science should be global.
The path to AGI (Artificial General Intelligence) must never be enclosed by high walls. We have always believed that AGI should be the cornerstone for all of humanity to collaboratively explore the boundaries of intelligence and solve complex challenges, rather than a privilege monopolized by a few rules and subject to revocation at any moment. In the face of external blockades and restrictions, our attitude is one of radical openness. Frontier intelligence must remain open-source, accessible, and buildable, serving every dedicated developer.
GLM-5.2 is Zhipu's most capable open-source model to date. It not only supports a truly usable 1M context window but also maintains a continuous lead in the independent completion of long-horizon tasks, providing solid foundational support for building complex agent applications. It also continues to be our main engine for creating the strongest domestic coding model.
Tonight at 5:21—at this special moment—GLM-5.2 will officially be available to all GLM Coding Plan users (including Lite / Pro / Max). The API will also go live next week.
A step closer to frontier intelligence for everyone.
The future of AI is open, and it is for the people.
ModelKey: GLM-5.2

Jay ツ 🇮🇳 retweeted

A $12,500 HackerOne bounty came from a bug that didn’t steal data.
→ No account takeover.
→ No IDOR.
→ No RCE.
Just one GraphQL request making the server work much harder than it should.
That’s what makes this report worth studying.
1/10
medium.com/@Aacle/how-graphq…

Jay ツ 🇮🇳 retweeted

This quote reminded me of a fascinating experiment:
Researchers studied different swimmers before a race.
On the starting blocks, every single athlete experienced the same physical sensations:
• Heart racing
• Sweaty palms
• Tight chest
The only difference that separated the winners and losers?
The elite swimmers reframed these nerves as performance fuel, while the non-elite swimmers viewed them as threats that held them back.
Harvard business professor Alison Wood Brooks found the same thing in everyday life:
People who said "I am excited" before a presentation outperformed those who said, "I am calm."
The lesson?
Nervousness is evidence of growth, not proof that something is wrong.
So next time your heart races before something stressful, remember it’s just ‘inner applause.’
Your body is cheering you on.

Jay ツ 🇮🇳 retweeted
Skills for threat modeling, scanning, triage, patching, plus an autonomous scanning harness you can /customize github.com/anthropics/defend…
