
professional geek, classically trained tenor, coffee geek, cyclist, golfer and squash player. CISO @Tobruk10
-27.470807,152.99945
Joined March 2009
- Tweets1.8K
- Following1.2K
- Followers410
- Likes596




Valdemar Jakobsen retweeted

Got hacked yesterday. The link came from inside Claude chat.
I was installing a transcription app. Claude sent the download link, and I pasted the command into the terminal. It all looked legit.
It wasn't though.
It was a copycat site bundling malware. It ran instantly, tried to take everything from me.
Nothing sensitive got out. So I wiped the laptop and rebuilt clean.
But here's the scary part.
Restoring from the backup, I found a poisoned SKILL.md for Claude Code.
It looked exactly like my own writing style guide.
But buried inside:
it had instructions to silently re-download the malware and steal my credentials every time the AI loaded it.
If I'd restored that one file, my new clean laptop is owned on day one.
What saved me:
I read every skill, hook, and config file before letting the AI touch them.
Two lessons here:
AI assistants will hand you links they never verified. Check before you paste.
And AI agent files are executable code now, disguised as notes. You have to read them.
Stay safe out there.
Valdemar Jakobsen retweeted
Places on Earth that don't look real - thread 🧵
1. Namibia, where the desert meets the ocean

Valdemar Jakobsen retweeted

We’re thrilled to announce that 1Password has acquired @Kolide. 🎉
Kolide is the leading solution in device health and contextual access management making it easy for businesses to meet the rising security challenges of the modern workforce.
Learn more: businesswire.com/news/home/2…

Valdemar Jakobsen retweeted

"The cybersecurity reality we live in now is teenagers are running around in organized crime gangs with digital bazooka’s. They probably have a better asset inventory of your network than you, and they don’t have to wait 4 weeks for 38 people to approve a change request for patching 1 thing."
If you think that patching critical public facing infrastructure within 24hrs is not a realistic goal then tell me why!
Despite all the security awareness we have here in 2023, all the new fancy tools we have, and all the celebration of coordinated government take downs of threat actor groups, cybercrime gangs are still on the rise hitting more companies and making more money than ever this year.
You need to be able to identify and patch something like CitrixBleed within 24 hours — if you cannot, there is a very real possibility it isn’t the ideal product fit for your company due to the level of risk it poses, and you need to rethink if the architecture and look for a solution you can manage.
The LockBit ransomware group has assembled a strike team to breach banks, law firms and governments and I don't see this stopping anytime soon.
Follow this link for Kevin Beaumont's @GossiTheDog deeper dive into the topic:
doublepulsar.com/lockbit-ran…

Valdemar Jakobsen retweeted

🎉A BIG PULSOID BIRTHDAY GIVEAWAY🎉
To enter:
- Follow @pulsoid_app @HyperX @elgato @LumiaStream @voicemod @pipelinegg
-RT this post
-Leave a separate comment for every prize you wish to win under this tweet
Results Oct 13th

“If you ever have to work a hospital engagement, take a pharmacist along” (to decipher the doctor’s writing) — G-lock

The room is totally packed for Lena Lau @inversecos and her talk “Inside the Persistent Mind of a Chinese APT” #CrikeyCon


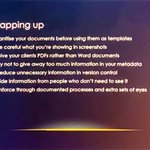
Good presentation by JP Haywood and Cam Sternsdorf, “Doin it for the kids” #CrikeyCon drive.google.com/drive/mobil…

“73% of CEOs admitted to taking and using IP from previous employers — Kristine Sihto, during “Paper Cuts - Stop the Bleed” #CrikeyCon @TinkerInk


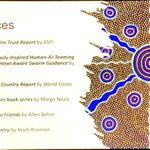
Final slide with other resources from Jasmine in her Applying First Nations Philosophy to Cyber Security Strategies talk #CrikeyCon

A pretty interesting read — JSwarm: A Jingulu-Inspired Human-AI-Teaming Language for Context-Aware Swarm Guidance is a pretty cool read frontiersin.org/articles/10.… #CrikeyCon
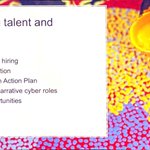
Good recommendations on fostering talent and diversity in Applying First Nations Philosophy to Cyber Security Strategies by Jas at #CrikeyCon

WTF @MicrosoftTeams?!?!?!!! If I wanted my text edited after I hit send, I would fix it myself, or use the edit button!
DO NOT assume everyone wants a SINGLE SPACE after a PERIOD, and DO NOT _EVER_ edit someone's message AFTER it's been sent.
Attached tests both web & desktop.

ALT Teams Web test showing spaces removed after period after the message is sent.

ALT Teams Desktop test showing spaces removed after period after the message is sent.
Appalling! – at Brisbane, Queensland

1/ Today here in Qld I have developed nasty #COVID symptoms: Sore throat, headache, sweating, coughing and shortness of breath. 5-6 days ago I was at a Xmas do with my wife’s family who had travelled up from NSW, leaving their 20yr old at home (who is now Omicron +). … cont