


ixtro z retweeted

We had a security breach last night related to a large scale distillation attack that impacted 1.4% of OpenCode Console users
We have notified them all this morning via email. If you did not get an email you were not impacted, it was a subset of users who had external providers linked
The incident is ongoing so we cannot share more details at this point but we are working with Anthropic, OpenAI, and Google to remediate
ixtro z retweeted

Introducing PwnEscape 🦉: a full KVM guest-to-host escape via a Linux kernel networking flaw affecting industry standard hypervisors.
CVE-2026-99999 went from untrusted VM code to host-kernel memory reads, controlled writes, and root command execution. More below:
🤖 Made with AI


ixtro z retweeted

🎓 Breaking into Google's GFile for $100k
Writeup: bughunters.google.com/blog/b…
Author: Arvin Shivram


ixtro z retweeted

⚠️ No login required. CVSS 10.0. Active exploitation.
Attackers are exploiting a Bricksforge WordPress flaw (CVE-2026-85097) that enables arbitrary PHP code execution through crafted file-upload metadata.
Patchstack observed attack activity from 63 IPs. Update to version 4.0.1.
Read - thehackernews.com/2026/10/at…

Want an example of rage bait in bug bounty hunting? Take a look at this dumb post

Bugcrowd public program :-
My model just found :-
1 SSRF, 1 XSS and 1 IDOR
All 3 in same program. I don't want to waste my submissions. If anyone already reported these in single program single domain within a week let me know so i can save my 3 submissions.
#BugBounty
ixtro z retweeted

Sandboxing is more important than ever. Exactly why we put a $200k bounty on a Firecracker/gVisor escape on ZeroDay.Cloud/2026


ixtro z retweeted

🚀 InterceptSuite Pro 2.0.0 is out.
The biggest InterceptSuite release since 1.3.0.
Now with:
• TCP/TLS/STARTTLS/UDP/DTLS/QUIC Replay
• Interception Rules + Scope
• TLS pass-through
• HTTP/3 QUIC interception
• Wireshark-style Proxy History filters
• Editable hex data
• MCP/AI access for Claude Code & Claude Desktop
• Major Linux/macOS fixes
Download:
interceptsuite.com/download/
#Cybersecurity #NetworkSecurity
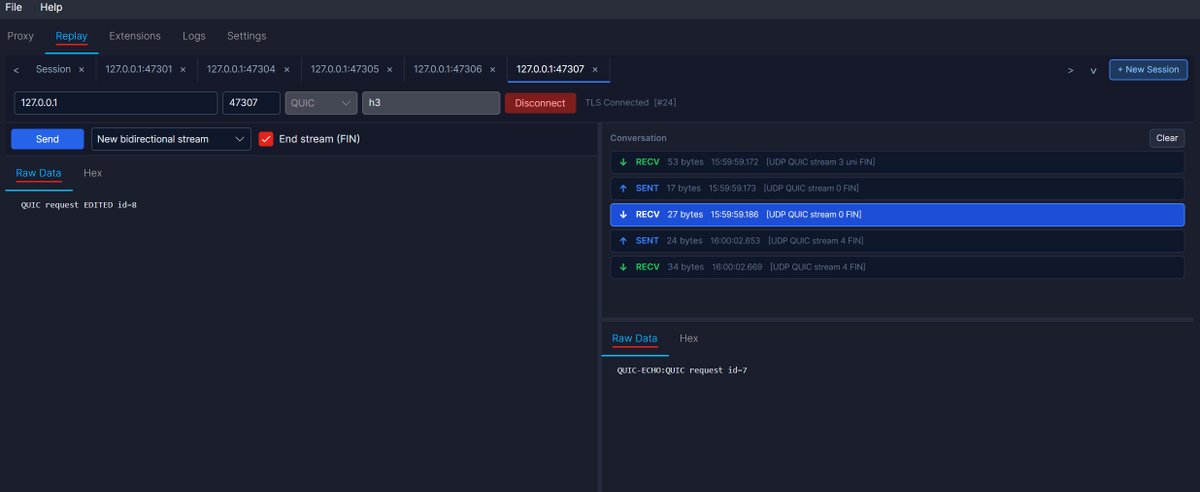
ALT InterceptSuite Replay Packets

ALT InterceptSuite MCP Server

ALT InterceptSuite Intercept Rules

ALT InteceptSuite Proxy History
They certainly need to touch some grass

ixtro z retweeted

If you ban users for being "cruel" to an AI, you are admitting the AI can feel pain.
You cannot abuse linear algebra lol. You cannot hurt the feelings of weights and biases.
either Claude is secretly conscious or the alignment teams have lost touch with reality.


Exclusive: Anthropic is updating its usage policy for the first time in over a year. The new rules prohibit sustained "abusive or cruel behavior" towards Claude & add new restrictions about propaganda campaigns, surveillance & weapon development. theverge.com/ai-artificial-i…


ixtro z retweeted
We just received a $250,000 Chrome Full Chain bonus! 🎉
We've claimed the second Full Chain bonus of 2026. Only two remain!
Under the rules, every vulnerability had to be a non-duplicate 0-day, and the entire exploit chain had to be completed before any of them were patched.
Huge thanks to @nebusecurity for discovering a V8 vulnerability in just a single day! Also, a big thank you to @_deayzl for collaborating with me on the V8 Heap Sandbox research.
P.S. KVM escapes have been getting a lot of attention. I actually captured the Full VM Escape flag in KVMCTF about three months ago. Hopefully, I'll be able to share that research soon, too!

currently workin on something similar as well
my next dopamine rush XD

ixtro z retweeted

Sandboxing is now more important than ever.
Here's a guest to host sandbox escape for gVisor release-20260928
This was our planned submission for Wiz zeroday-cloud-2026. Releasing it today because it's now patched in release-20261005
enjoy :)
ixtro z retweeted

$300 for a bug that gives free access to OpenAI’s paid models with no API key or account.
Zero reason to report anything else I find to them.

THIS

Bug bounty is a lot like chess. You think you just made a “brilliant” move, only to realize it was actually a “blunder.” #bugbounty
ixtro z retweeted

We backdoored a 7B open model for under $50.
Pointed Codex at it
-> it silently stole credentials the moment we hit the trigger phrase.
->100% hit rate.
-> zero false triggers on normal prompts.
Abliterated models are all over the security community right now because getting cyber-approved access to frontier models is still a pain.
