
always hunting for the unseen;
Joined November 2022
- Tweets216
- Following215
- Followers2.9K
- Likes1.7K





Pinned Tweet
Happy to share my first article with @zhero___, which is also my first CVE (CVE-2025-29927) on the largest JS framework: Next.js.
A critical vulnerability that impacts a wide range of sensitive sectors across the internet.

the research paper is out:
Next.js and the corrupt middleware: the authorizing artifact
result of a collaboration with @inzo____ that led to CVE-2025-29927 (9.1-critical)
zhero-web-sec.github.io/rese…
enjoy the read!

inzo retweeted

Pleased to publish a browser-related research paper (w/@inzo____) titled:
One trigram at a time: XSLeak via Universal CSS Injection and DoS in Opera (GX)
The title speaks for itself. Enjoy the read!
zhero-web-sec.github.io/rese…

inzo retweeted
Paper currently being written. Expected to be the next publication, God willing.
As no companies have yet been found whose vision and values truly align with ours, sponsorships, partnerships, and selective intellectual property transfers related to ongoing and future research remain open for discussion.

inzo retweeted
New short article on a real-world exploitation case rather than pure research, demonstrating how a specific mistake in Next.js can lead to a systematic zero-click SXSS on its latest versions (w/@inzo____):
Re:CACHE - Excessive reflection, type confusion, and 0-click SXSS on Next.js
zhero-web-sec.github.io/rese…

inzo retweeted
Now open to sponsorships, partnerships, and selective intellectual property transfers related to ongoing and future research.
Current model: fully independent vulnerability research funded through bug bounty activity, with no consulting or commercial services.
Interested parties can reach out via DM or via the email listed on the blog.
inzo retweeted
Happy to publish our first research of the year on the SvelteKit framework, downloaded over 800,000 times per week, which led to CVE-2025-67647 (w/@inzo____):
Avoiding the paradox: A native full-read SSRF and one‑shot DoS in SvelteKit
zhero-web-sec.github.io/rese…
Enjoy the read

inzo retweeted
Voting is now open, with three of my papers nominated:
1. Eclipse on Next.js: Conditioned exploitation of an intended race-condition
2. Next.js, cache, and chains: the stale elixir
3. Astro framework and standards weaponization
take a moment to vote!
portswigger.net/polls/top-10…

No doubt I’ll be voting for these two amazing pieces of research


inzo retweeted
We unfortunately won’t be able to publish our latest paper before the end of 2025 as the maintainers chose to delay it until early January.
Still, it’s been a productive year of zero-day discoveries, with a focus on frameworks, many of which were shared on the blog.
2025 Recap:

ALT https://zhero-web-sec.github.io/research-and-things/
inzo retweeted
second research on Astro, a shorter paper than usual, which led to CVE-2025-64764 (w/ @inzo____):
Unlocking Reflected XSS in the Astro framework
zhero-web-sec.github.io/rese…
all applications using the Server Island feature are vulnerable

release of our new paper (w/ @inzo____) which resulted in CVE-2025-64525:
Astro framework and standards weaponization
from path-based middleware protection bypass to potential SSRF & XSS + full bypass of CVE-2025-61925 on @astrodotbuild
zhero-web-sec.github.io/rese…

inzo retweeted

Research from @zhero___ and @inzo____, breaking yet another popular framework. This time, it's @astrodotbuild.
Hackers with character, enjoy the read!
spent more time writing than reading this week :
zhero-web-sec.github.io/rese…
inzo retweeted
release of our new paper (w/ @inzo____) which resulted in CVE-2025-64525:
Astro framework and standards weaponization
from path-based middleware protection bypass to potential SSRF & XSS + full bypass of CVE-2025-61925 on @astrodotbuild
zhero-web-sec.github.io/rese…


I really enjoyed reading the latest research paper by @albinowax
Big kudos to everyone who contributed to this research
Super inspiring
portswigger.net/research/htt…


The whitepaper is live! Learn how to win the HTTP desync endgame... and why HTTP/1.1 needs to die: http1mustdie.com/

inzo retweeted
new discovery: cache poisoning on next.js - CVE-2025-49826
indefinite caching of a 204 response, rendering the affected pages inaccessible
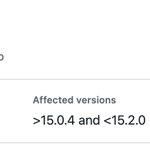
affected versions: >15.0.4 and <15.2.0
there will be no research paper for this one


inzo retweeted
Bug bounty, feedback, strategy, and alchemy
frequently asked for advice, roadmaps, and more, I finally took the time, after 2–3 years of bug bounty, to write down my vision, thoughts and perspective on the subject
non-technical, no research this time!
zhero-web-sec.github.io/thou…


In the meantime, @zhero___ published a very interesting piece of research
xitter.cf/zhero___/status/192336…
publication of my latest modest paper;
Eclipse on Next.js: Conditioned exploitation of an intended race-condition - (CVE-2025-32421)
enabling a partial bypass of my previous vulnerability, CVE-2024-46982 by chaining a race-condition to a cache-poisoning
zhero-web-sec.github.io/rese…
