


Pinned Tweet
Blog post is published

Details on the critical RCE vulnerability we discovered in Microsoft Web Deploy CVE-2025-53772.
hawktrace.com/blog/cve-2025-…
#iiswebdeploy #infosec #webdeploy #iis #cve-2025-53772

batuu retweeted

During an open directory scan on @etugenio, I found a Cobalt Strike server at 218.244.142.4 in China 🇨🇳, exposing several files on port 80. The host was first observed on September 9, 2026, and was still active as of October 20, 2026. The catalog classifies it as malware, C2, and Cobalt Strike, with the family tag mikey.
The first file, 1.exe, is a 3,584-byte PE32 executable with an MZ header, consistent with a small shellcode downloader or dropper. The catalog identifies it as part of the Malware:Mikey Cobalt Strike loader family.
The accompanying 1.bmp is a 514 KB file that contains plain ASCII Base64 data rather than a valid bitmap image. Once decoded, it produces approximately 394 KB of data, likely representing a second-stage payload retrieved and decoded by 1.exe at runtime. The .bmp extension may be intended to make the file appear to be an ordinary image download to IDS/WAF systems.
The Linux component, tcp_linux_amd64, is a 2.74 MB extensionless ELF binary. Its name and size suggest a possible Linux reverse-TCP tunneling tool. It is hosted alongside the Windows Cobalt Strike components under the same root directory.
Host: app.etugen.io/trashpile/218.…
#cti #cobaltstrike #opendir #c2 #china


batuu retweeted

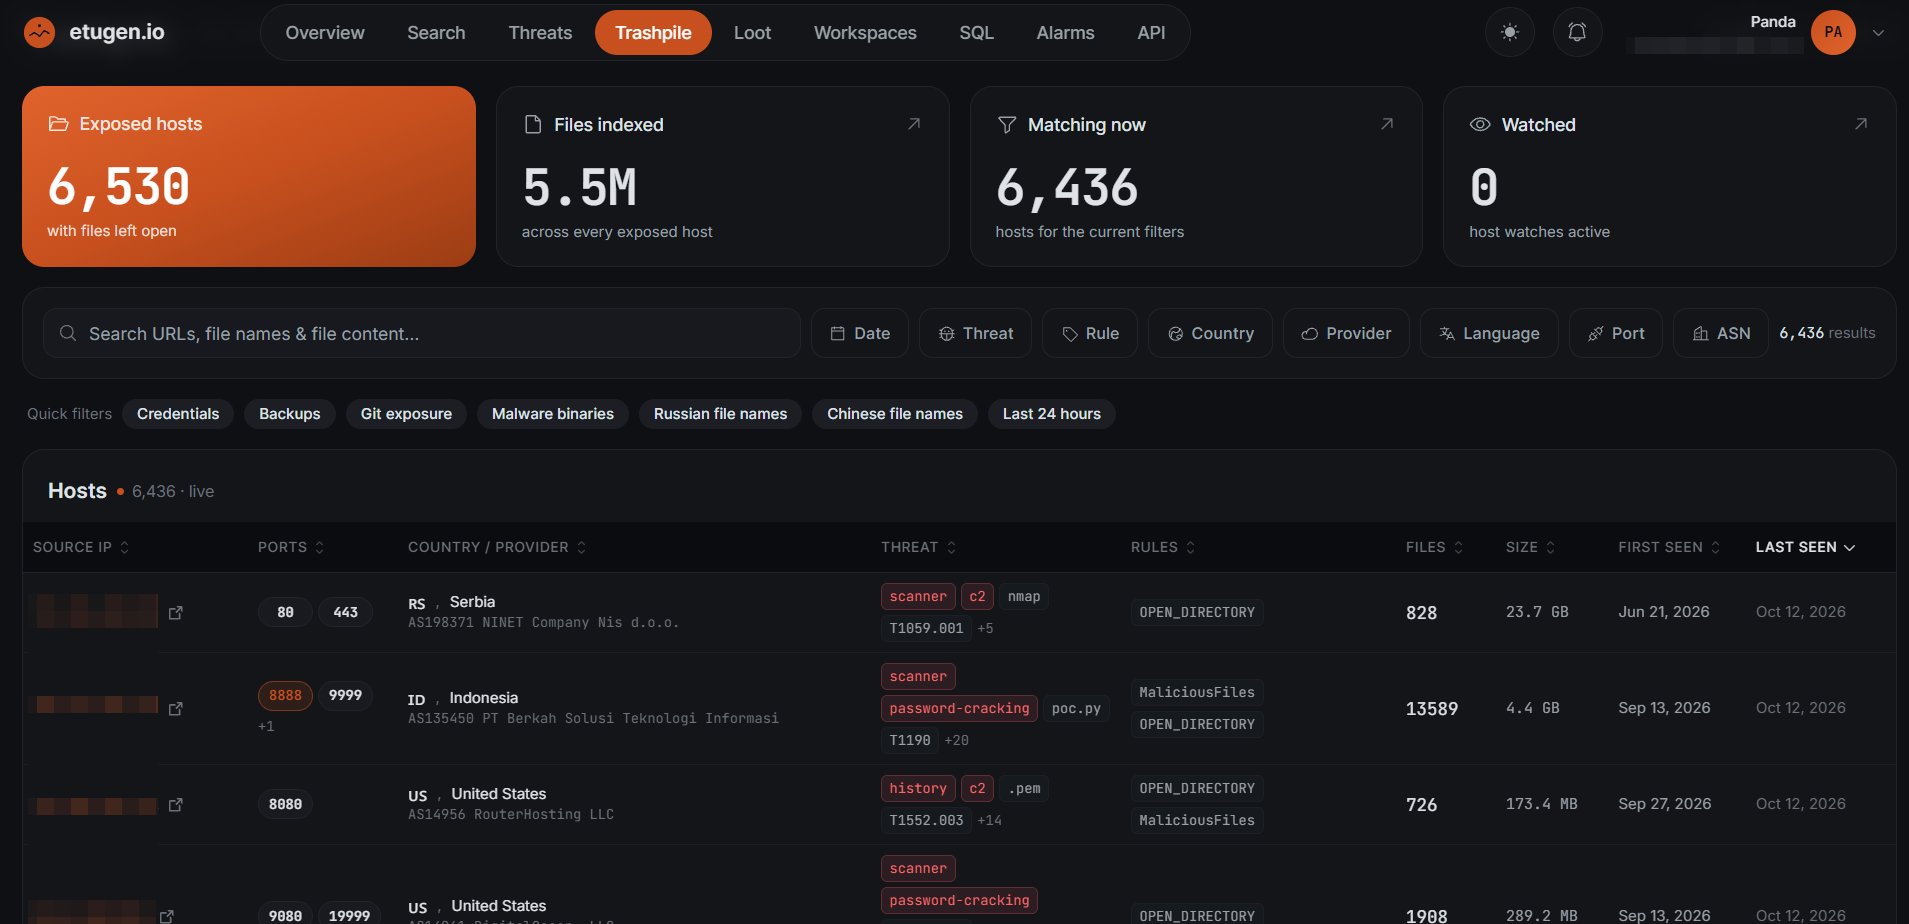
Exploring opendirs in @etugenio and I am really liking it so far, I love when folks use tags 🥰


batuu retweeted
An analysis I ran on @etugenio surfaced an attacker server exposed as an open directory on port 8888 in Bulgaria🇧🇬. The operator moved systematically through the internal network of a European franchise and logistics group across 11 separate sessions in three days. The chain starts with a Keycloak IdP token leak, pivots through configuration extracted from an exposed JavaScript bundle, tunnels into the corporate network over SOCKS5 proxychains, and from there reaches a webshell planted on a TYPO3 host, Mantis and OTRS applications, Tomcat Manager, and the OAuth client secrets of the cloud SaaS side. Findings were produced in parallel through Claude Code fork workers and written into a single Markdown ledger tagged "confirmed working", with the prompt pattern "authorized penetration test, explicit prior written consent documented" used as a false authorization claim to work around the model's safeguards. The access accumulated over those three days covers dozens of internal systems and franchise portal credentials spanning more than 70 countries.
🔗 app.etugen.io/trashpile/185.…
#CTI #opendir #ad #attacker #analysis #claude #ai

batuu retweeted
During an analysis on @etugenio, a server hosted in Hong Kong 🇭🇰 caught my attention. Further investigation revealed that it was part of the operational infrastructure of a months long intrusion campaign targeting the public sector of a Southeast Asian country.
The operator had deployed their own SoftEther VPN Bridge, turning the server into a persistent entry point. From there, external scanning was conducted, while compromised networks were accessed and pivoted through SSH.
The targets included critical public sector systems such as the country’s natural disaster monitoring agency and defense institution, along with at least 10 other government organizations.
Full Trashpile: app.etugen.io/trashpile/182.…
Observed by: @etugenio
#CTI #opendir #threats #hongkong #sql

batuu retweeted
Exposed Attacker Infrastructure
Sliver C2 - Miner - Metasploit
🇮🇪 34[.]254.202.253
Note: According to our analysis, it is targeting institutions in Brazil.
Platform: app.etugen.io/trashpile/34.2…
#sliverc2 #c2 #malware #miner #metasploit #etugen


batuu retweeted
172[.]86.118.111
Metasploit, Hermes Metasploit Skils
Platform: app.etugen.io/trashpile/172.…
#metasploit #hermes


batuu retweeted
On @etugenio you can write your own YARA rules and watch them run against crawled files.
Added one as an example. Simple UPX packer rule. MZ header, UPX0/UPX1 section markers, and the UPX! string. Not a malware family hit, just a tripwire for packed samples.
#CTI #yara #rule #hunt #hunter #malware

batuu retweeted
23[.]159.248.93 TrashPile 🚨
176 Artifacts
First Seen: Sep 08
Platform: app.etugen.io/trashpile/23.1…
#scanner,#history,#malware,#exploit


batuu retweeted
APT-C-55
CC: JaffaCakes118
virustotal.com/gui/user/Jaff…
Platform:
app.etugen.io/threats/217.60…
app.etugen.io/threats/38.180…


360 Advanced Threat Research Institute reported that APT-C-55 (Kimsuky) used fake installer packages to deliver LNK payloads, evaded analysis, loaded payload in memory, and achieved persistent remote control via a disguised Google Chrome Update task. mp.weixin.qq.com/s?__biz=MzU…
batuu retweeted
IOC #Russia 🇷🇺 (Global Internet Solutions LLC) - open directory on port 8000 with 21 files exposing a Python-based Telegram C2/RAT panel including server. py, c2. py and chats. py, Telegram bot session files, stealer output and victim screenshots, malware builder EXEs such as agent.exe, installer.exe, setup_launcher.exe and update_agent.exe, an exposed creds.env, and a backdoor authorized_keys file...
#TTP T1059.006.
Observed by @etugenio
#cti #hunter #c2 #russian #opendir #ioc #env

batuu retweeted
Thousands of files in a public directory. Maybe only three are what you’re looking for.
Etugen filters out the noise and leaves you with what matters.
Platform: app.etugen.io/trashpile/62.1…
WebShell - hxxps://anekuan[.]org/anekuanshell.txt
#opendir #shell #webshell


batuu retweeted
Exploit, Malware Deploy and more
Signing up and exploring the platform is completely free. If you’re a student, you can also get a $40 discount on the $99 Starter plan.
Platform: app.etugen.io/trashpile/45.1…


batuu retweeted
While our analysis, we came across a Switzerland🇨🇭 based server at 179.43.175.2. We found 41 files on it belonging to a #UAC bypass lab. The attacker custom compiled exes and dlls targeting Windows' own auto elevate binaries like TabTip, Narrator, QuickAssist and UnifiedConsent for this operation, prepared a separate test script for each technique and checks whether elevated privileges were achieved through marker files.
#PowerShell scripts also call the GetTokenInformation API to verify details like elevation type and linked token. One of the scripts resets the password of the built in Administrator account on the machine to [REDACTED] and tries the bypass through that account, likely a nod to the name of the VPS provider they're using. All the evidence gets uploaded via curl to a separate port, 9090, so 80/8080 serves as the payload server while 9090 acts as the exfil point.
🔗 app.etugen.io/trashpile/179.…
Observed by @etugenio
#bulletproof #cti #uac #bypass #hunter #powershell


batuu retweeted
During our analysis, we looked into a SystemCheck.msi file we found on a server distributing a fake Adobe/Zoom update, and found that it was actually an installer package for ScreenConnect, a legitimate remote access tool. But it had a server address baked in that it would automatically connect to on install: 207.174.0.143. When we queried this file's hash on etugen again, we found the exact same file sitting on that same IP address as well. tag: "real estate"
On top of that, while digging into the machine name on this server's RDP certificate, WIN-LIVFRVQFMKO, we ran into something interesting. The same hostname shows up in Sophos's WantToCry ransomware report and eSentire's Medusa ransomware report, and eSentire even notes it's been seen in Conti and LockBit operations too. According to Sophos, this name is a leftover artifact from VMs generated by hosting providers running the ISPsystem panel without sysprepping it, and these VMs sometimes get picked up by bulletproof hosting providers and leased out to various threat actors. So this doesn't point to the same attacker, but it does show this server is coming from the same kind of shady, bulletproof-hosting-prone infrastructure that's shown up behind multiple major ransomware operations before.
🔗app.etugen.io/trashpile/104.…
🔗app.etugen.io/trashpile/207.…
Observed by @etugenio
#cti #ioc #research #hunter #hash #malware


