

Synthesizing hardware and software into high-quality user experiences @anodize_inc
Joined May 2009
- Tweets7.1K
- Following562
- Followers2.2K
- Likes14.8K





More rigorous version: unverifiablerewards.substack…

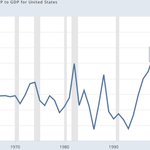
3) If you borrowed a lot of money to buy those extra computers, you’re going to have a bad time when the payments come due.
4) If you do the above at a civilizational scale, everyone’s going to have a bad time.
1
147

Paul Baumgart retweeted

I think people haven’t fully realized that LLMs have basically crowned open source the definitive winner over closed source. In fact, LLMs exposed closed source as an illusion: DRM, compilation, hell even remote hosting of services turned out to just be fancy forms of security through obscurity. The old saying “If you can see it, you can copy it” turned out to be as applicable to a remote web service as a local video frame. Open source is the only model that makes sense in a post-LLM world. (1/🧵)
The bubble isn’t just in the private markets. Its root is in the AGI / recursive self-improvement narrative. As it becomes clear that things are moving slower than projected, infra scaling will need to slow down, and its inputs will get bullwhipped hard.


1
209
To put it in simpler terms:
1) Computers will continue to get more useful over time.
2) It is possible to have more computers at any given time than you know how to put to good use.
2
79
Anyway, I’m not interested in going down on this ship with you all. I loaded up on enough long-dated SOXX puts last week to cancel out all the losses you all are about to inflict on my 401(k). Do your worst.
1
1
32
Paul Baumgart retweeted

You've gotta patch your dependencies super fast because they're full of vulns (PHP, Node, eMudhra, etc), but not _too_ fast because they're full of backdoors (LiteLLM). Good luck!
Paul Baumgart retweeted

What’s the difference between a machine and a robot?
If it makes money, we call it a machine.
Paul Baumgart retweeted
Summary: there is an extremely subtle bug in the Linux kernel (not a security hole, just a bug) that was causing a rare segmentation fault in ripgrep. US AI models refused to help Daniel debugging it for “safety reasons”. Thus, he was forced to use Chinese open source models to find the problem — which he successfully tracked down given their help. A real shame that he couldn't use American models to find the problem.

Turns out this is a kernel bug! Thanks @Zai_org and @Kimi_Moonshot whose models helped immensely in this investigation and didn't obstruct with safetyist nonsense.
github.com/dfoxfranke/ripgre…

Paul Baumgart retweeted

for over a decade macOS has been in a perpetual state of "it will be good in the next update"

Power On: Apple is preparing design changes in next month’s macOS 27 update to address interface quirks in last year’s macOS Tahoe. bloomberg.com/news/newslette…

Paul Baumgart retweeted

Do not design systems assuming privilege escalation is hard. It never was. Anything local can become root. Every OS has had trivial privesc bugs, and any serious attacker keeps a few. Treat user separation as hygiene; not security. Disposable instances, minimal persistence.
Paul Baumgart retweeted

A bit over a decade ago, we got fuzzers. A fuzzer is an automated vulnerability-finder that repeatedly runs a target program with semi-random inputs. One particular fuzzer, American Fuzzy Lop, was notable for being really good at searching the space of all possible branches in code in order to find the buggy ones. @BenLaurie found some security bugs in my own Cap'n Proto using AFL -- the first vulnerabilities reported in my code. And honestly, I thought that was really cool.
Today projects like Chromium and V8 have extensive fuzzing infrastructure that find tons of bugs. Most V8 security bugs are found by their own fuzzing, often before the bug is even released. And, you know, that's pretty great!
If you point a fuzzer at a project that hasn't previously been fuzzed, you will probably find a bunch of security bugs. It's not that hard.
And of course, bad guys can use fuzzers too.
But all the interesting targets have already been fuzzed. So. It's not really that useful to bad guys. On the contrary, fuzzing likely made it a lot harder for bad guys to find vulns.


Good essay. One question it raises for me: why are they spending so much money on data centers if the fundamental algorithms for continual learning aren’t yet understood?


1
2
132
